



Cybersecurity News in Asia

RECENT STORIES:

SEGA moves faster with flow-based network monitoring
Deepfakes and impersonators can fool people, but they should not bypas...
FOMO Pay expands cross-border compliance infrastructure amid rising fr...
From Defence Cooperation to Shared Security: Building a Resilient Paki...
Cyber insurers and legal professionals prepare for claims over harms b...
CyberDSA Sets 19 – 21 October 2027 Return as Industry Participat...
LOGIN REGISTER
CybersecAsia
  • Features
    • Featured

      How CISOs can set human boundaries for autonomous cybersecurity

      How CISOs can set human boundaries for autonomous cybersecurity

      Wednesday, October 7, 2026, 11:05 AM Asia/Singapore | Features, Newsletter, Tips
    • Featured

      Securing the agentic enterprise – at machine speed

      Securing the agentic enterprise – at machine speed

      Tuesday, October 6, 2026, 5:00 PM Asia/Singapore | Features, Newsletter
    • Featured

      Why businesses need to treat AI agents like privileged insiders

      Why businesses need to treat AI agents like privileged insiders

      Thursday, October 1, 2026, 10:00 AM Asia/Singapore | Features, Opinions, Sponsored
  • Opinions
  • Tips
  • Whitepapers
  • AWARDS 2026
  • Directory
  • E-Learning

Select Page

News

Business email compromise rackets still going strong, cybersecurity firm warns

By CybersecAsia editors | Thursday, June 5, 2025, 1:17 PM Asia/Singapore

Business email compromise rackets still going strong, cybersecurity firm warns

Are organizations training Finance personnel and all staff to be vigilant?

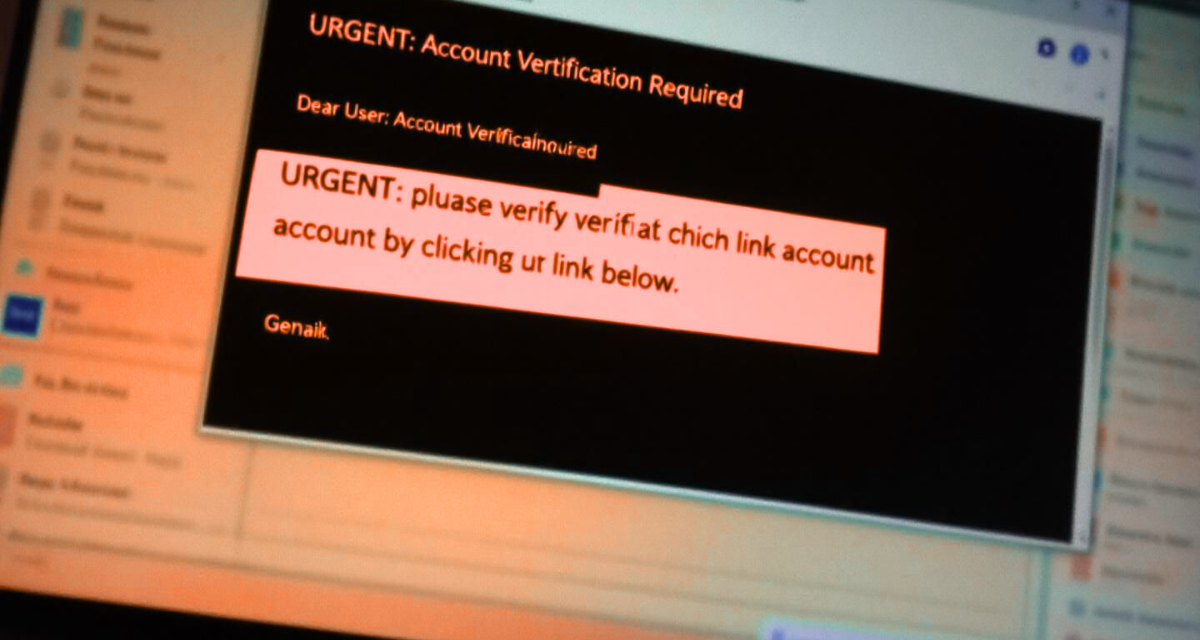
A cybersecurity firm’s analysts have noticed that, in recent weeks, several organizations have reported attempts by attackers to deceive finance departments into processing fraudulent payments.

Attackers had sent emails that appeared to come from company executives, such as the CEO, instructing staff to pay invoices for supposed consulting services. The emails typically imitated ongoing correspondence between the firm’s leadership and external contractors or law firms.

In some cases, the attackers had referenced previous messages or included fabricated email threads to make the requests appear legitimate. Also, while the sender’s display name matched that of a known executive or partner, the actual email address was unrelated and changed frequently.

Some of these Business Email Compromise (BEC) incidents included fake invoices as attachments, while others had relied solely on the content of the email to prompt urgent action. The primary tactic was to exploit employees’ trust in internal communications, and their reluctance to question requests from senior management.

Other incidents had featured emails that mimicked communications between a CEO and contractor firms to request urgent payment for a fake invoice, but the invoices were not attached, according to a spokesperson for Kaspersky, the firm that disclosed this incidence-response trend.

Organizations need to train staff to be vigilant for BEC attacks:

  • Making sure emails involving sensitive and important requests from key leaders have the correct originating email address and domain, and matching sender name.
  • When a sender is legitimate, but the content of the message seems strange, staff should contact the supposed sender via an alternative, unhackable means of communication.
  • Being constantly on guard for phishing attempts and spoofed URLs, such as a “1” instead of “I”, or “0” replacing the letter “O”.
  • Using the proper email authentication protocols, email security filters and AI/ML features to flag suspicious communications and behavioral patterns.

Finally, even though cybercriminals and malicious insiders may learn a target firm’s processes and system weaknesses, they will find it difficult to pull off a BEC successfully when the organization’s policies mandate non-negotiable multi-stage, multi-party identity verifications for financial transactions or sensitive data.
Share:

PreviousInfostealer threat group shows resilience despite major takedown and taunts
NextWill EDR killers be standard fare in cybercriminals’ arsenals in 2025?

Related Posts

Watch out for festive cyber scams this Lunar New Year

Watch out for festive cyber scams this Lunar New Year

Friday, January 19, 2024

Is the world more secure in their remote-working security now?

Is the world more secure in their remote-working security now?

Tuesday, June 8, 2021

18-month regional e-commerce bug bounty program goes public

18-month regional e-commerce bug bounty program goes public

Monday, June 14, 2021

Further evidence of Chinese Threat Actors found in SEA telecom firms

Further evidence of Chinese threat actors found in SEA telecom firms

Wednesday, August 4, 2021

Leave a reply Cancel reply

You must be logged in to post a comment.

Voters-draw/RCA-Sponsors

Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
previous arrow
next arrow

CybersecAsia Voting Placement

Gamification listing or Participate Now

LEARN MORE

Vote Now -Placement(Google Ads)

Top-Sidebar-banner

Whitepapers

  • Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Cyber threats have become more frequent and sophisticated, targeting organizations of all sizes across all …Download Whitepaper
  • Zero Trust Made Simple: Why it matters and how to get started

    Zero Trust Made Simple: Why it matters and how to get started

    Data breaches and cyberattacks are no longer limited to large, high-profile organizations.Download Whitepaper
  • Cloud Secure Edge: Remote access, better security

    Cloud Secure Edge: Remote access, better security

    ​SonicWall Cloud Secure Edge™ is a modern, cloud-native Security Service Edge (SSE) solution that addresses …Download Whitepaper
  • Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Insider threats continue to be a major cybersecurity risk in 2024. Explore more insights on …Download Whitepaper

Middle-sidebar-banner

Case Studies

  • FOMO Pay expands cross-border compliance infrastructure amid rising fraud risks

    FOMO Pay expands cross-border compliance infrastructure amid rising fraud risks

    To unify onboarding and ongoing reviews the payment firm adds identity, liveness, business-ownership, sanctions screening …Read more
  • How a Vietnamese D2C retailer built its own secure digital infrastructure

    How a Vietnamese D2C retailer built its own secure digital infrastructure

    Would your organization build your own digital infrastructure – including AI governance and cybersecurity – …Read more
  • Cyber protection for medical clinics in Singapore

    Cyber protection for medical clinics in Singapore

    As Singapore’s healthcare sector becomes increasingly digital and interconnected, clinics are facing heightened cyber risks, …Read more
  • India’s WazirX strengthens governance and digital asset security

    India’s WazirX strengthens governance and digital asset security

    Revamping its custody infrastructure using multi‑party computation tools has improved operational resilience and institutional‑grade safeguardsRead more

Bottom sidebar

Other News

  • From Defence Cooperation to Shared Security: Building a Resilient Pakistan-China Partnership

    Friday, October 9, 2026
    QINGDAO, China, Oct. 9, 2026 …Read More »
  • CyberDSA Sets 19 – 21 October 2027 Return as Industry Participation Builds at Fourth Edition

    Thursday, October 8, 2026
    CyberDSA moves towards its milestone …Read More »
  • CyberLogitec Brings Tag-Free Collision Prevention to Busan New Port

    Tuesday, October 6, 2026
    Digital twin places workers and …Read More »
  • Aligning with Global Regulations: iMQ Technology’s SQ713x Secure Element Achieves SESIP and PSA Certified Level 3

    Monday, October 5, 2026
    Passes Keysight’s physical attack testing …Read More »
  • Cymulate Receives Frost & Sullivan’s 2026 Indian Competitive Strategy Leadership Recognition for Advancing Continuous Security Validation

    Monday, October 5, 2026
    The recognition highlights Cymulate’s competitive …Read More »
  • Our Brands
  • DigiconAsia
  • MartechAsia
  • Home
  • About Us
  • Contact Us
  • Sitemap
  • Privacy & Cookies
  • Terms of Use
  • Advertising & Reprint Policy
  • Media Kit
  • Subscribe
  • Manage Subscriptions
  • Newsletter

Copyright © 2026 CybersecAsia All Rights Reserved.