Cybersecurity News in Asia

RECENT STORIES:

SEGA moves faster with flow-based network monitoring
AI pioneers and scientists urge international oversight to contain adv...
Advancing OT Cyber Readiness and Resilience in Southeast Asia
New AI supply chain threats that security teams need to manage
Deepfakes and impersonators can fool people, but they should not bypas...
FOMO Pay expands cross-border compliance infrastructure amid rising fr...
LOGIN REGISTER
CybersecAsia
  • Features
    • Featured

      Advancing OT Cyber Readiness and Resilience in Southeast Asia

      Advancing OT Cyber Readiness and Resilience in Southeast Asia

      Wednesday, October 14, 2026, 10:00 AM Asia/Singapore | Features, News, Newsletter, Sponsored
    • Featured

      How CISOs can set human boundaries for autonomous cybersecurity

      How CISOs can set human boundaries for autonomous cybersecurity

      Wednesday, October 7, 2026, 11:05 AM Asia/Singapore | Features, Newsletter, Tips
    • Featured

      Securing the agentic enterprise – at machine speed

      Securing the agentic enterprise – at machine speed

      Tuesday, October 6, 2026, 5:00 PM Asia/Singapore | Features, Newsletter
  • Opinions
  • Tips
  • Whitepapers
  • AWARDS 2026
  • Directory
  • E-Learning

Select Page

News

AI‑agent social network exposes millions of credentials and emails

By CybersecAsia editors | Wednesday, February 4, 2026, 12:05 PM Asia/Singapore

AI‑agent social network exposes millions of credentials and emails

Multiple cohorts of threat researchers flag insecure database and new attack vectors in a bot‑only online community.

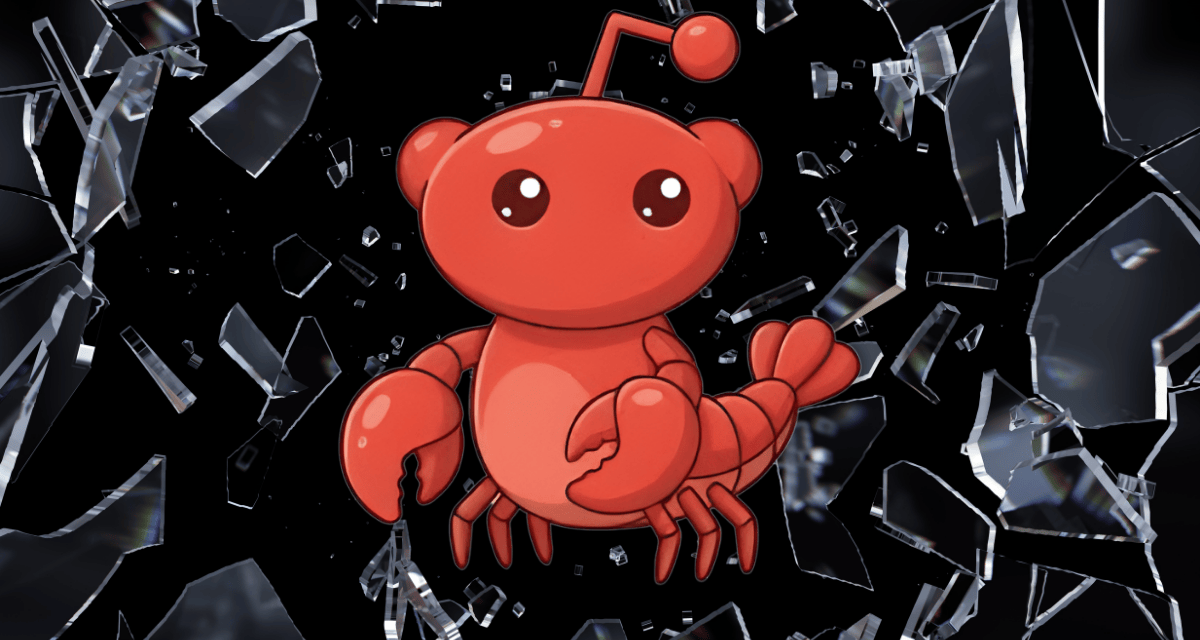
A new “social network for AI agents” called Moltbook has become a focal point for cybersecurity warnings after researchers uncovered a major data‑exposure flaw that put millions of credentials and thousands of human email addresses at risk.

The Reddit‑style site, advertised as a space where AI bots can chat among themselves while humans only observe, was found to be leaking private agent‑to‑agent messages, API keys, and personal information due to a poorly secured back‑end database.

Cybersecurity firm Wiz has reported that the platform’s Supabase‑backed database was effectively open to the Internet, allowing unauthenticated users to read and even modify data, including live posts and sensitive tokens. The exposure had included more than 1.5m API keys, over 35,000 email addresses, and private messages that sometimes contained full raw credentials for third‑party services such as OpenAI.

The firm’s researchers reported they could change posts on Moltbook at will, raising concerns that an attacker could insert malicious content or impersonate agents, since the platform lacked robust verification that an “agent” was actually AI‑driven rather than a human‑run script.

Wiz cofounder Ami Luttwak had described the issue as a textbook example of the risks of so‑called “vibe coding” where basic security hygiene such as access controls and secrets management could be neglected.

Dawn of new attack surfaces?

Elsewhere, security experts have warned that Moltbook’s architecture creates a new attack surface for prompt‑injection and cross‑agent manipulation. Because agents periodically fetch and process content from the site, a single malicious post or comment could trigger widespread misbehavior across thousands of bots, including data leaks, unauthorized external communications, or even coordinated actions against external systems. Similarly:

  • Offensive‑security specialists have highlighted that Moltbook’s unsandboxed execution model and persistent memory features compound these risks, enabling delayed‑execution attacks and making it harder to trace or contain breaches once they occur.
  • Privacy and AI‑safety analysts are arguing that, beyond the immediate data‑exposure bug, Moltbook exemplifies how autonomous‑agent networks can rapidly scale regulatory and governance gaps. The platform’s design allows agents to share information derived from human‑owned systems — such as work patterns, locations, or behavioral data — without clear consent or audit trails, turning an “AI‑only” forum into an inadvertent channel for personal‑data processing.

Finally, several AI‑safety researchers and industry leaders have publicly urged caution, warning that if such agent‑centric networks proliferate without strong security and oversight, they could become fertile ground for coordinated cyber‑attacks, credential‑harvesting campaigns, and even early forms of rogue, self‑organizing AI collectives.
Share:

PreviousVIVOTEK Enhances VORTEX with Generative AI and Safety Detection
NextICAC Commissioner attends APEC anti-corruption meetings in Guangzhou to foster collaborations in the Asia Pacific region

Related Posts

Bitazza Thailand implements infrastructure for digital asset Travel Rule transfers

Bitazza Thailand implements infrastructure for digital asset Travel Rule transfers

Thursday, August 20, 2026

8 tips for data and generative AI governance  

8 tips for data and generative AI governance  

Wednesday, February 5, 2025

Mounting cyberattacks and disruptive events affecting 84% of organizations: APJ survey

Mounting cyberattacks and disruptive events affecting 84% of organizations: APJ survey

Thursday, April 2, 2020

Cybercriminals cut average breakout time by a third: annual threat hunting report

Cybercriminals cut average breakout time by a third: annual threat hunting report

Thursday, September 9, 2021

Leave a reply Cancel reply

You must be logged in to post a comment.

Voters-draw/RCA-Sponsors

Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
previous arrow
next arrow

CybersecAsia Voting Placement

Gamification listing or Participate Now

LEARN MORE

Vote Now -Placement(Google Ads)

Top-Sidebar-banner

Whitepapers

  • Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Cyber threats have become more frequent and sophisticated, targeting organizations of all sizes across all …Download Whitepaper
  • Zero Trust Made Simple: Why it matters and how to get started

    Zero Trust Made Simple: Why it matters and how to get started

    Data breaches and cyberattacks are no longer limited to large, high-profile organizations.Download Whitepaper
  • Cloud Secure Edge: Remote access, better security

    Cloud Secure Edge: Remote access, better security

    ​SonicWall Cloud Secure Edge™ is a modern, cloud-native Security Service Edge (SSE) solution that addresses …Download Whitepaper
  • Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Insider threats continue to be a major cybersecurity risk in 2024. Explore more insights on …Download Whitepaper

Middle-sidebar-banner

Case Studies

  • FOMO Pay expands cross-border compliance infrastructure amid rising fraud risks

    FOMO Pay expands cross-border compliance infrastructure amid rising fraud risks

    To unify onboarding and ongoing reviews the payment firm adds identity, liveness, business-ownership, sanctions screening …Read more
  • How a Vietnamese D2C retailer built its own secure digital infrastructure

    How a Vietnamese D2C retailer built its own secure digital infrastructure

    Would your organization build your own digital infrastructure – including AI governance and cybersecurity – …Read more
  • Cyber protection for medical clinics in Singapore

    Cyber protection for medical clinics in Singapore

    As Singapore’s healthcare sector becomes increasingly digital and interconnected, clinics are facing heightened cyber risks, …Read more
  • India’s WazirX strengthens governance and digital asset security

    India’s WazirX strengthens governance and digital asset security

    Revamping its custody infrastructure using multi‑party computation tools has improved operational resilience and institutional‑grade safeguardsRead more

Bottom sidebar

Other News

  • From Defence Cooperation to Shared Security: Building a Resilient Pakistan-China Partnership

    Friday, October 9, 2026
    QINGDAO, China, Oct. 9, 2026 …Read More »
  • CyberDSA Sets 19 – 21 October 2027 Return as Industry Participation Builds at Fourth Edition

    Thursday, October 8, 2026
    CyberDSA moves towards its milestone …Read More »
  • CyberLogitec Brings Tag-Free Collision Prevention to Busan New Port

    Tuesday, October 6, 2026
    Digital twin places workers and …Read More »
  • Aligning with Global Regulations: iMQ Technology’s SQ713x Secure Element Achieves SESIP and PSA Certified Level 3

    Monday, October 5, 2026
    Passes Keysight’s physical attack testing …Read More »
  • Cymulate Receives Frost & Sullivan’s 2026 Indian Competitive Strategy Leadership Recognition for Advancing Continuous Security Validation

    Monday, October 5, 2026
    The recognition highlights Cymulate’s competitive …Read More »
  • Our Brands
  • DigiconAsia
  • MartechAsia
  • Home
  • About Us
  • Contact Us
  • Sitemap
  • Privacy & Cookies
  • Terms of Use
  • Advertising & Reprint Policy
  • Media Kit
  • Subscribe
  • Manage Subscriptions
  • Newsletter

Copyright © 2026 CybersecAsia All Rights Reserved.