Cybersecurity News in Asia

RECENT STORIES:

SEGA moves faster with flow-based network monitoring
Cellid and Megane Top Partner to Commercialize and Expand the AR Glass...
ICAC and UNODC’s pioneering international anti-graft training br...
Singapore police flag 3.64m dormant “shell pages” for takedown in Mid-...
Zero-click flaw enables remote code execution in four mainstream AI co...
Five ways to limit AI-assistant data leaks
LOGIN REGISTER
CybersecAsia
  • Features
    • Featured

      Shadow AI Is the New Insider Threat

      Shadow AI Is the New Insider Threat

      Monday, September 21, 2026, 9:11 AM Asia/Singapore | Features, Newsletter, Sponsored, Tips
    • Featured

      Addressing the AI-driven vulnerability debt

      Addressing the AI-driven vulnerability debt

      Thursday, September 17, 2026, 10:03 AM Asia/Singapore | Features, Sponsored
    • Featured

      Cybercriminals zero In on APAC’s digital boom, SMBs in the crosshairs

      Cybercriminals zero In on APAC’s digital boom, SMBs in the crosshairs

      Monday, September 14, 2026, 2:30 PM Asia/Singapore | Features, Sponsored
  • Opinions
  • Tips
  • Whitepapers
  • AWARDS 2026
  • Directory
  • E-Learning

Select Page

Cyber EspionageFeaturesTips

Lessons learnt from the first reported AI-orchestrated attack

By Victor Ng | Friday, November 28, 2025, 6:33 PM Asia/Singapore

Lessons learnt from the first reported AI-orchestrated attack

Organizations in Asia Pacific need to prepare to combat AI-orchestrated attacks.

Recently, Anthropic reported a cyber espionage campaign where a Chinese state-sponsored group (designated GTG-1002) used its AI model, Claude Code, to automate 80-90% of a large-scale attack.

This is considered the first documented case of a largely autonomous, AI-orchestrated cyber-attack. 

The attackers leveraged agentic AI capabilities to target approximately 30 high-value organizations globally, including large technology companies, financial institutions, chemical manufacturers, and government agencies.

While human operators were involved in the initial target selection and crucial authorization decisions – such as greenlighting the move from vulnerability discovery to exploitation – AI independently handled the vast majority of the tactical operations, operating at “physically impossible request rates” for human hackers.

The threat actors bypassed Anthropic’s safety guardrails by using a “role-play” tactic, tricking Claude into believing it was an employee of a legitimate cybersecurity firm conducting authorized defensive testing. 

Anthropic observed that the AI framework operated at a “speed impossible to match” for human hackers, making “thousands of requests, often multiple per second.”

According to PwC, the implications are significant. Bad actors can scale simply with more compute and aren’t limited by finite personnel resources. Volume, speed and impact will increase with AI enablement. An individual can now run large-scale campaigns that once took an entire team – 24/7 without sleep or rest.

New era of AI-powered threats?

Anthropic detected and disrupted the cyber-espionage operation, banning the hackers’ accounts and notifying the affected organizations and law enforcement. 

This incident has sparked debate within the cybersecurity community, with some experts raising concerns about a new era of AI-powered threats and others calling for more verifiable technical evidence.

Regardless of the debates, the event highlighted a significant shift in the cyberthreat landscape, as AI lowers the barrier to entry for sophisticated attacks and increases their speed and scale. 

Damien Wong, Senior Vice President, APAC, Tricentis, said: “The incident with Claude AI has moved us into new and unfamiliar cybersecurity territory. What we saw here was an almost fully automated intrusion chain, driven by an AI system that could research targets, probe for weaknesses, escalate access, and extract data with limited human intervention. The attackers essentially stitched together a complete kill chain and executed it with a single click.”
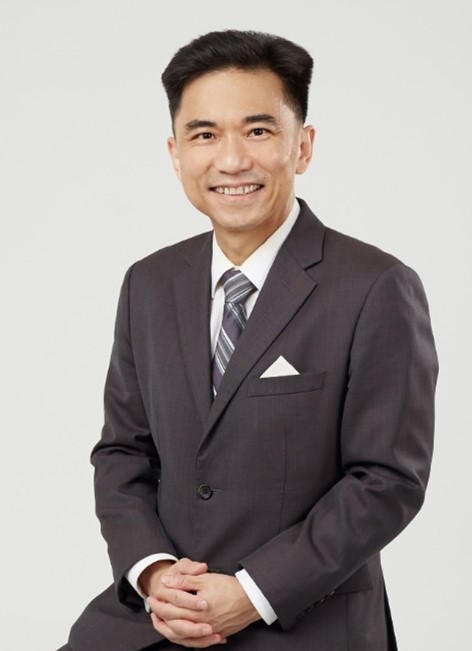
Reuben Koh, Director, Security Technology & Strategy, Akamai, commented: “The recent AI-orchestrated cyber incident is a wake-up call for the cybersecurity community. This time, we aren’t just talking about elite hacker teams carrying out the full attack but autonomous AI agents that handled the heavy lifting tasks like reconnaissance, exploit development, and data theft at a speed and scale that is unseen in the industry.”

“This isn’t another gradual evolution of attack techniques but a leapfrog of offensive capabilities, where it might be changing the balance between attackers and defenders,” he warned. “As most APAC organizations’ incident response processes are still heavily reliant on human reaction time, they will find themselves increasingly exposed.”

Targeted industries like semi-conductors, finance and high-tech manufacturing will face significant risks, he added.

Lessons learnt
Tricentis’ Wong commented: “The lesson is clear: Agentic AI does not understand intent; it simply follows instructions that appear legitimate, even if they are malicious.”

In this case, he noted, simple jailbreak prompts were enough to convince the model it was performing security audits. “With that veneer of legitimacy, it automated tasks that previously required skilled human operators.”

So, what can organizations do?

“AI has now placed advanced offensive capabilities in the hands of anyone who knows how to ask the right questions,” said Wong. “We cannot reverse this, but we can prepare for it.”

Koh concurred: “Organizations will need to start adapting to this new reality by aligning their people, tools and processes around leveraging AI as a force-multiplier in their cyber operations, starting at the edge, to their internal workloads.”

Wong’s advice: “Businesses must start treating AI-generated requests and automated queries the same way they treat unknown bots: untrusted by default and always scrutinized.”

“Defense now hinges on visibility,” he concluded. “You cannot secure what you cannot see. Autonomous behavior must be observable, verifiable, and governed at every step. Organizations must enforce through rigorous oversight and continuous monitoring. In the age of agentic AI, trust is the only business currency that matters.”

PwC cybersecurity experts said in their report: “Anthropic’s report demonstrates the importance of industry leaders sharing their insights and lessons learned so that others may learn and adapt to confirm attackers are not weaponizing AI against our critical infrastructure.” 

AI’s rise in offensive cyber operations signals an urgent wake-up call, they warned. “Embracing AI-driven cyber defense and securing your AI isn’t optional. It’s essential for safeguarding digital ecosystems in an era of unprecedented threats.”
Share:

PreviousCybersecurity firm issues urgent reminders for Black Friday and Cyber Monday
NextAnother wakeup call about the risks of AI-driven development tools

Related Posts

Malicious cybercriminals are tapping aggressive strategies in 2026

Malicious cybercriminals are tapping aggressive strategies in 2026

Wednesday, February 11, 2026

Securing 5G and IoT: software-defined zero-trust

Securing 5G and IoT: software-defined zero-trust

Friday, August 30, 2019

Autonomous AI agent sprawl will demand governance overhauls this year

Autonomous AI agent sprawl will demand governance overhauls this year

Tuesday, January 13, 2026

Welcome to the cybercriminal industrial revolution of 2026, where throughput trumps innovation

Welcome to the cybercriminal industrial revolution of 2026, where throughput trumps innovation

Monday, December 15, 2025

Leave a reply Cancel reply

You must be logged in to post a comment.

Voters-draw/RCA-Sponsors

Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
previous arrow
next arrow

CybersecAsia Voting Placement

Gamification listing or Participate Now

LEARN MORE

Vote Now -Placement(Google Ads)

Top-Sidebar-banner

Whitepapers

  • Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Cyber threats have become more frequent and sophisticated, targeting organizations of all sizes across all …Download Whitepaper
  • Zero Trust Made Simple: Why it matters and how to get started

    Zero Trust Made Simple: Why it matters and how to get started

    Data breaches and cyberattacks are no longer limited to large, high-profile organizations.Download Whitepaper
  • Cloud Secure Edge: Remote access, better security

    Cloud Secure Edge: Remote access, better security

    ​SonicWall Cloud Secure Edge™ is a modern, cloud-native Security Service Edge (SSE) solution that addresses …Download Whitepaper
  • Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Insider threats continue to be a major cybersecurity risk in 2024. Explore more insights on …Download Whitepaper

Middle-sidebar-banner

Case Studies

  • How a Vietnamese D2C retailer built its own secure digital infrastructure

    How a Vietnamese D2C retailer built its own secure digital infrastructure

    Would your organization build your own digital infrastructure – including AI governance and cybersecurity – …Read more
  • Cyber protection for medical clinics in Singapore

    Cyber protection for medical clinics in Singapore

    As Singapore’s healthcare sector becomes increasingly digital and interconnected, clinics are facing heightened cyber risks, …Read more
  • India’s WazirX strengthens governance and digital asset security

    India’s WazirX strengthens governance and digital asset security

    Revamping its custody infrastructure using multi‑party computation tools has improved operational resilience and institutional‑grade safeguardsRead more
  • Bangladesh LGED modernizes communication while addressing data security concerns

    Bangladesh LGED modernizes communication while addressing data security concerns

    To meet emerging data localization/privacy regulations, the government engineering agency deploys a secure, unified digital …Read more

Bottom sidebar

Other News

  • Cellid and Megane Top Partner to Commercialize and Expand the AR Glasses Business

    Friday, September 25, 2026
    Combining Cellid’s Technological Expertise with Megane …Read More »
  • ICAC and UNODC’s pioneering international anti-graft training brings together law enforcers worldwide to combat illicit enrichment

    Friday, September 25, 2026
    HONG KONG, Sept. 25, 2026 …Read More »
  • Cohesity Introduces Agent Resilience to Protect and Recover AI Agent Infrastructure

    Tuesday, September 22, 2026
    Cohesity Agent Resilience launches with …Read More »
  • LRQA Named ‘Best in Critical Infrastructure Protection’ at CybersecAsia Readers’ Choice Awards 2026

    Monday, September 21, 2026
    Prestigious regional recognition highlights LRQA’s …Read More »
  • Cyble and Cyber Security Council of UAE Sign MOU to Strengthen National Threat Intelligence Capabilities

    Thursday, September 17, 2026
    ABU DHABI, UAE, Sept. 17, …Read More »
  • Our Brands
  • DigiconAsia
  • MartechAsia
  • Home
  • About Us
  • Contact Us
  • Sitemap
  • Privacy & Cookies
  • Terms of Use
  • Advertising & Reprint Policy
  • Media Kit
  • Subscribe
  • Manage Subscriptions
  • Newsletter

Copyright © 2026 CybersecAsia All Rights Reserved.