Cybersecurity News in Asia

RECENT STORIES:

SEGA moves faster with flow-based network monitoring
More than 23,500 customers affected by SIMBA data breach
Cellid and Megane Top Partner to Commercialize and Expand the AR Glass...
ICAC and UNODC’s pioneering international anti-graft training br...
Singapore police flag 3.64m dormant “shell pages” for takedown in Mid-...
Zero-click flaw enables remote code execution in four mainstream AI co...
LOGIN REGISTER
CybersecAsia
  • Features
    • Featured

      Shadow AI Is the New Insider Threat

      Shadow AI Is the New Insider Threat

      Monday, September 21, 2026, 9:11 AM Asia/Singapore | Features, Newsletter, Sponsored, Tips
    • Featured

      Addressing the AI-driven vulnerability debt

      Addressing the AI-driven vulnerability debt

      Thursday, September 17, 2026, 10:03 AM Asia/Singapore | Features, Sponsored
    • Featured

      Cybercriminals zero In on APAC’s digital boom, SMBs in the crosshairs

      Cybercriminals zero In on APAC’s digital boom, SMBs in the crosshairs

      Monday, September 14, 2026, 2:30 PM Asia/Singapore | Features, Sponsored
  • Opinions
  • Tips
  • Whitepapers
  • AWARDS 2026
  • Directory
  • E-Learning

Select Page

NewsTips

Study: Cyber resilience in APAC foundational but not future-ready

By CybersecAsia editors | Friday, April 17, 2026, 9:30 AM Asia/Singapore

Study: Cyber resilience in APAC foundational but not future-ready

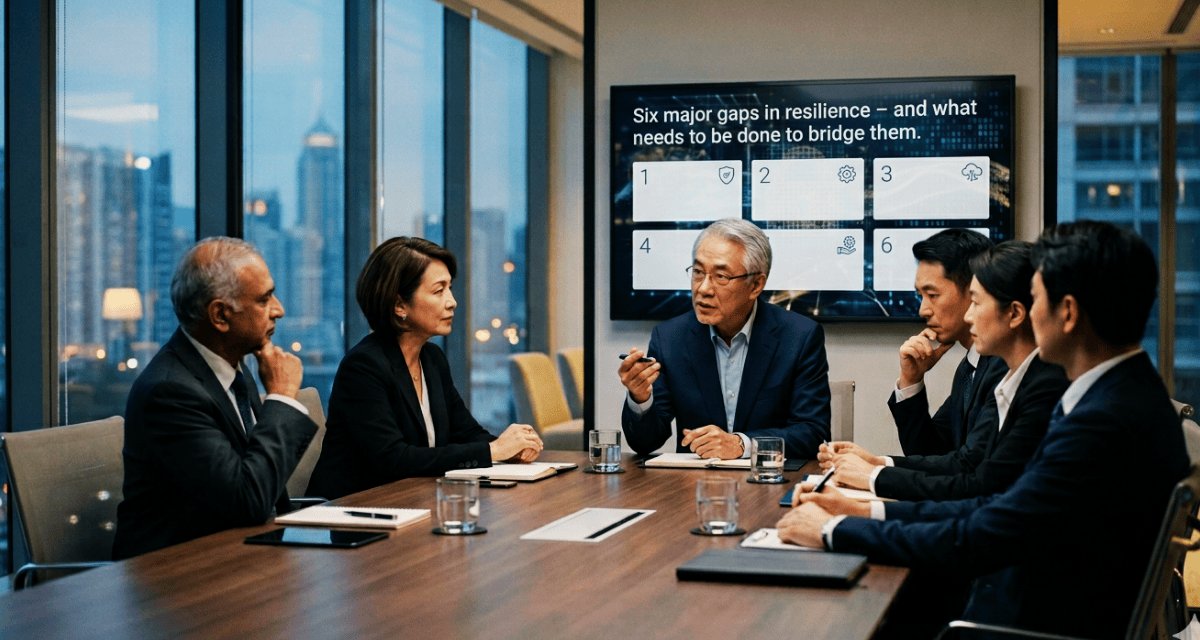
Six major gaps in resilience – and what need to be done to bridge them.

A new research report developed by EconomistImpact and supported by Telstra International, examines how organizations in APAC cope with technology disruptions, from cyber incidents to system failures, supplier outages, governance gaps, and decision‑making, particularly under real-world pressure.

The research is based on a survey of 1,420 senior executives across 11 APAC markets, with benchmarks from the United States, United Kingdom, and Germany.

Key findings from the report include:

  • Ecosystem resilience is the weakest link in digital resilience efforts
    APAC organizations are confident in their internal measures, such as training and testing, but confidence fades beyond their boundaries: only 12% have first-hand insight into suppliers’ resilience. 
    Limited information-sharing, infrequent joint simulations and weak partner governance make ecosystem interdependencies the main source of resilience failure. 
    Without active governance of key partners, disruptions spread easily, no matter how strong internal controls are. Such governance should include setting shared standards, conducting joint tests and ensuring clear visibility into third-party risks.
  • Workforce preparedness remains foundational rather than future-ready
    Resilience grows when planning and training focus on the ability to respond. Organizations must instil adaptive behaviors such as cross-functional co-ordination and under-pressure decision-making. The emphasis should be on how quickly teams can reorganize work when systems fail.
    Organizational gaps, not tools, derail incident response
    Organizations plan widely for responding to threats of digital disruption. But less than one-quarter (23%) of responses to real threats go according to plan. 
    Plans fail not due to a lack of technology, but because decision-making, co-ordination and authority structures break down in practice. Organizations cannot rely on technology investment alone to strengthen resilience.
  • Confidence is limited in external resilience enablers
    Executives express strong confidence in cybersecurity policy and planning (57%) but are far less assured in other external enablers of resilience, including the reliability of communications networks, regulatory clarity and the stability of power supply. 
    This uncertainty requires organizations to factor in redundancy and enable degraded-mode operations, across regions and cloud providers.
  • Risk management is largely reactive and monitoring is limited
    Most organizations have formal risk management frameworks, but these center mainly on cyber and IT risks. Attention to regulatory, supplier, geopolitical and climate risks is limited, and monitoring is periodic. 
    This leaves processes better suited to documenting known risks than to anticipating and managing fast-moving disruption. Continuous monitoring and forward-looking scenario-testing must become standard practice.
  • Senior leaders recognize digital resilience, but shared ownership remains limited 
    Senior-level responsibility for digital resilience tends to fall to one executive, such as the CIO. 
    At most organizations, boards are not heavily involved in review or planning of resilience-building efforts, which constrains strategic oversight and weakens enterprise-wide coordination.
Share:

PreviousPopular PC utility website served malware-laced installers for 19 hours
NextHighlights of Asia’s 2026 premier integrated security event

Related Posts

(ISC)² closes global cyber workforce numbers gap in under 10 months

(ISC)² closes global cyber workforce numbers gap in under 10 months

Friday, August 4, 2023

Report: Complex RansomOps fuel growth in ransomware economy

Report: Complex RansomOps fuel growth in ransomware economy

Thursday, April 21, 2022

Cyber insurance: requirements getting more stringent?

Cyber insurance: requirements getting more stringent?

Monday, November 28, 2022

Sextortion phishing may have been getting more personal lately

Sextortion phishing may have been getting more personal lately

Tuesday, November 26, 2024

Leave a reply Cancel reply

You must be logged in to post a comment.

Voters-draw/RCA-Sponsors

Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
previous arrow
next arrow

CybersecAsia Voting Placement

Gamification listing or Participate Now

LEARN MORE

Vote Now -Placement(Google Ads)

Top-Sidebar-banner

Whitepapers

  • Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Cyber threats have become more frequent and sophisticated, targeting organizations of all sizes across all …Download Whitepaper
  • Zero Trust Made Simple: Why it matters and how to get started

    Zero Trust Made Simple: Why it matters and how to get started

    Data breaches and cyberattacks are no longer limited to large, high-profile organizations.Download Whitepaper
  • Cloud Secure Edge: Remote access, better security

    Cloud Secure Edge: Remote access, better security

    ​SonicWall Cloud Secure Edge™ is a modern, cloud-native Security Service Edge (SSE) solution that addresses …Download Whitepaper
  • Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Insider threats continue to be a major cybersecurity risk in 2024. Explore more insights on …Download Whitepaper

Middle-sidebar-banner

Case Studies

  • How a Vietnamese D2C retailer built its own secure digital infrastructure

    How a Vietnamese D2C retailer built its own secure digital infrastructure

    Would your organization build your own digital infrastructure – including AI governance and cybersecurity – …Read more
  • Cyber protection for medical clinics in Singapore

    Cyber protection for medical clinics in Singapore

    As Singapore’s healthcare sector becomes increasingly digital and interconnected, clinics are facing heightened cyber risks, …Read more
  • India’s WazirX strengthens governance and digital asset security

    India’s WazirX strengthens governance and digital asset security

    Revamping its custody infrastructure using multi‑party computation tools has improved operational resilience and institutional‑grade safeguardsRead more
  • Bangladesh LGED modernizes communication while addressing data security concerns

    Bangladesh LGED modernizes communication while addressing data security concerns

    To meet emerging data localization/privacy regulations, the government engineering agency deploys a secure, unified digital …Read more

Bottom sidebar

Other News

  • Cellid and Megane Top Partner to Commercialize and Expand the AR Glasses Business

    Friday, September 25, 2026
    Combining Cellid’s Technological Expertise with Megane …Read More »
  • ICAC and UNODC’s pioneering international anti-graft training brings together law enforcers worldwide to combat illicit enrichment

    Friday, September 25, 2026
    HONG KONG, Sept. 25, 2026 …Read More »
  • Cohesity Introduces Agent Resilience to Protect and Recover AI Agent Infrastructure

    Tuesday, September 22, 2026
    Cohesity Agent Resilience launches with …Read More »
  • LRQA Named ‘Best in Critical Infrastructure Protection’ at CybersecAsia Readers’ Choice Awards 2026

    Monday, September 21, 2026
    Prestigious regional recognition highlights LRQA’s …Read More »
  • Cyble and Cyber Security Council of UAE Sign MOU to Strengthen National Threat Intelligence Capabilities

    Thursday, September 17, 2026
    ABU DHABI, UAE, Sept. 17, …Read More »
  • Our Brands
  • DigiconAsia
  • MartechAsia
  • Home
  • About Us
  • Contact Us
  • Sitemap
  • Privacy & Cookies
  • Terms of Use
  • Advertising & Reprint Policy
  • Media Kit
  • Subscribe
  • Manage Subscriptions
  • Newsletter

Copyright © 2026 CybersecAsia All Rights Reserved.