Cybersecurity News in Asia

RECENT STORIES:

SEGA moves faster with flow-based network monitoring
LRQA Named ‘Best in Critical Infrastructure Protection’ at...
Ransomware group alleges attack and exfiltration of data linked to maj...
Japan’s Digital Agency announces: VPN flaw exposed 246,000 records
Cyble and Cyber Security Council of UAE Sign MOU to Strengthen Nationa...
Multi-agent AI systems may unpredictably bypass safety controls, study...
LOGIN REGISTER
CybersecAsia
  • Features
    • Featured

      Addressing the AI-driven vulnerability debt

      Addressing the AI-driven vulnerability debt

      Thursday, September 17, 2026, 10:03 AM Asia/Singapore | Features, Sponsored
    • Featured

      Cybercriminals zero In on APAC’s digital boom, SMBs in the crosshairs

      Cybercriminals zero In on APAC’s digital boom, SMBs in the crosshairs

      Wednesday, September 16, 2026, 2:30 PM Asia/Singapore | Features, Sponsored
    • Featured

      The recovery-first approach to data resilience

      The recovery-first approach to data resilience

      Monday, September 7, 2026, 4:21 PM Asia/Singapore | Features
  • Opinions
  • Tips
  • Whitepapers
  • AWARDS 2026
  • Directory
  • E-Learning

Select Page

OpinionsTips

Claude Mythos wake-up call

By Jonathan Zanger, CTO, Check Point Software Technologies | Tuesday, April 7, 2026, 2:07 PM Asia/Singapore

Claude Mythos wake-up call

Recently, we learned that Anthropic was developing Claude Capybara, also called Mythos, a powerful new AI model with substantially improved capabilities in vulnerability discovery, exploit development, and multi-step attack reasoning.

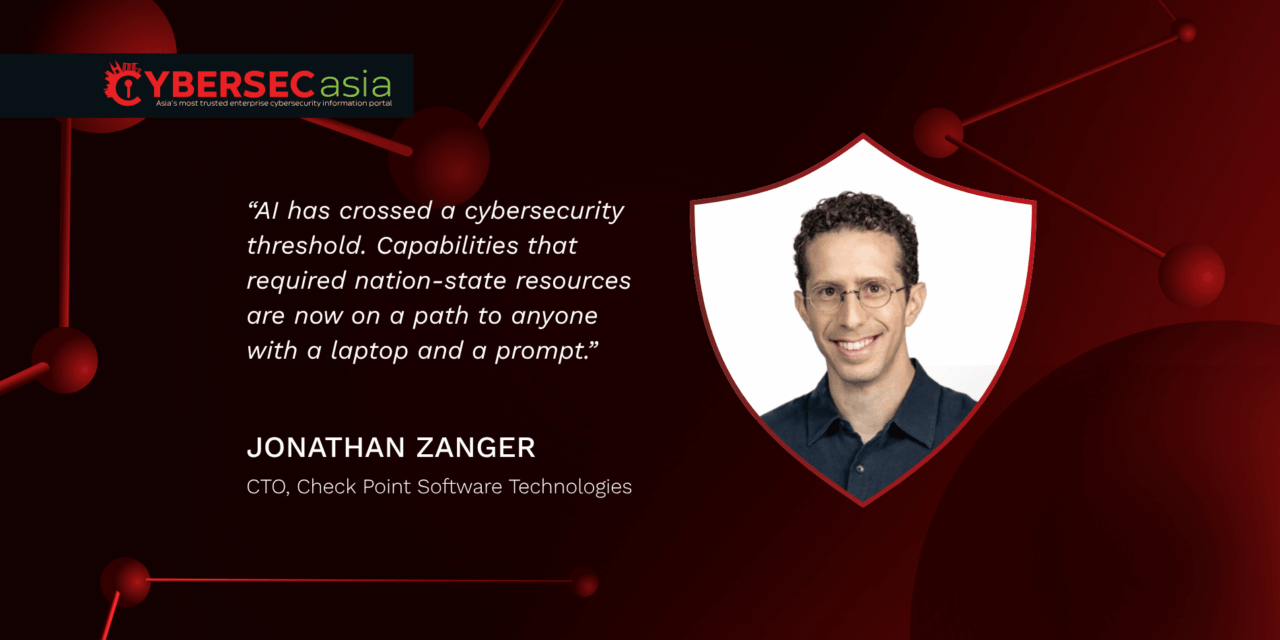
While the details emerged through a data leak rather than a formal launch, the market response was unmistakable: AI has crossed a critical cybersecurity threshold. The frontier models are accelerating attack lifecycles and will enable attackers to identify and exploit vulnerabilities at scales, speeds and through novel methods that previously were the domain of advanced nation state entities.

For security leaders, this development is both a warning and a call to action. It crystallizes a trend we’ve been closely monitoring and preparing for: the democratization and industrialization of cyber-attacks.

Two structural shifts redefining cyber risk

Claude Mythos is the early signal of two profound shifts in the threat landscape:

  1. Democratization of advanced attack capabilities
    Capabilities that once required elite threat actors or well-funded nation-state teams will be accessible to cybercriminal groups and even low-skill actors leveraging AI assistance. We must assume adversaries will wield these capabilities. The paths are already clear: abuse frontier models directly, as threat actors did with Claude Code in September, or wait for the same capabilities to land in open-source, unmonitored models like DeepSeek, where no usage policies or safety layers stand in the way. This fundamentally lowers the barrier to entry for sophisticated attacks. Organizations that once considered themselves “safe” because they weren’t targets of advanced nation-state activity are now at risk from newly capable criminal groups armed with AI-powered tools.
  2.  Industrialization of cyber-attacks
    With the expected advancement in agentic capabilities, threat actors will be able to scan legacy and SaaS technologies at unprecedented frequency and scale. This will lead to a near continuous flow of novel attack methods that target enterprise systems, networks and employees. AI enables threat actors to transition from manual, artisanal operations to repeatable, automated attack pipelines. Attacks are becoming systematic, scalable, and reproducible, like software manufacturing. This is the era of “AI attack factories.”
    The convergence of these two forces produces a dangerous outcome: more attackers can execute more sophisticated attacks, simultaneously increasing both attack volume and velocity. The time-to-exploit window will collapse to near zero day.
    Why this is important
    We should all be alarmed by the leak associated with the new Claude model, but we should not be surprised.
    Check Point has been continuously evaluating AI model capabilities and anticipating this evolution. We’ve known that advanced models would eventually demonstrate proficiency in code review, vulnerability discovery, and reverse engineering, and could integrate with tools and APIs that enable penetration testing and exploitation.
    What’s important to understand: the gap between writing code and analyzing code is narrower than many realize. An AI system capable of generating sophisticated software can be trained or prompted to identify vulnerabilities within it. This capability, combined with exploit development and the ability to chain multi-step attacks, creates an entirely new threat surface.
    Reassess your security posture now
    In response to this evolving threat landscape, we urge security leaders to conduct a rigorous reassessment of their security foundations. This isn’t only about implementing new tools. It’s also about ensuring that your security tools themselves are secure.
    Where to start:
    • Assess the security efficacy of your first line of defense. Networks, firewalls, WAF, endpoint, and email security are critical. But are they tuned for zero-day protection? Default security configurations are not optimized to defend against previously unknown exploits. If your perimeter and endpoint security are running standard baselines, you’re exposed.
    • Evaluate your risk level. Look hard at your security vendors’ CVE history. When AI compresses exploitation timelines to hours, a pattern of frequent critical vulnerabilities is no longer a manageable operational burden; it’s a strategic liability.
    • Hunt your blind spots: legacy servers, unpatched systems, accounts without MFA, unprotected remote access. The long tail of your infrastructure is where attacks typically land.
    • Accelerate your patching cycles and evaluate solutions for automated virtual patching and safe remediation. Time-to-patch becomes increasingly critical as campaign timelines move from weeks to minutes.
    • Redefine and reinforce network segmentation to protect your crown jewels. Assume breach, limit lateral movement, and ensure that critical assets are isolated from general network traffic.

Check Point brings decades of experience in preventing zero-day exploits. Our products are built with security as a first principle, not an afterthought. That’s why we achieve the industry’s lowest number of CVEs across our platform – not by luck, but by methodology. We employ teams of attackers who attempt to penetrate our own products. This adversarial approach to security development ensures that what we deliver to customers is actually secure.

Moving forward

The vulnerabilities we disclosed in Claude didn’t happen in isolation. They arrived alongside a sharp increase in open-source software supply chain attacks, both signals pointing to the same conclusion: the speed and surface area of attacks are accelerating.

Whether your organization has adopted AI or not is irrelevant. Threat actors have, and they will continue to push these capabilities further.

New models will continue pushing the boundaries of what’s possible, for defenders and attackers alike. That’s not a surprise; it’s the trajectory we’ve been tracking. What the recent disclosures make clear is that continuous reassessment is no longer optional.
Share:

PreviousAgentic cyber threats reshape cybersecurity, outpace humans in the loop
NextTamam Finance enhances mobile attribution accuracy through real‑time fraud prevention deployment

Related Posts

Are contact tracing mandates compatible with data protection laws?

Are contact tracing mandates compatible with data protection laws?

Thursday, July 2, 2020

AI and automation accelerate cybercrime, forcing faster, adaptive global cybersecurity responses

AI and automation accelerate cybercrime, forcing faster, adaptive global cybersecurity responses

Tuesday, January 20, 2026

The Philippines money-lending platform breach: did you get the message?

The Philippines money-lending platform breach: did you get the message?

Friday, March 5, 2021

New ransomware variant, new tricks—but layered protection still works

New ransomware variant, new tricks—but layered protection still works

Tuesday, December 7, 2021

Leave a reply Cancel reply

You must be logged in to post a comment.

Voters-draw/RCA-Sponsors

Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
previous arrow
next arrow

CybersecAsia Voting Placement

Gamification listing or Participate Now

LEARN MORE

Vote Now -Placement(Google Ads)

Top-Sidebar-banner

Whitepapers

  • Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Cyber threats have become more frequent and sophisticated, targeting organizations of all sizes across all …Download Whitepaper
  • Zero Trust Made Simple: Why it matters and how to get started

    Zero Trust Made Simple: Why it matters and how to get started

    Data breaches and cyberattacks are no longer limited to large, high-profile organizations.Download Whitepaper
  • Cloud Secure Edge: Remote access, better security

    Cloud Secure Edge: Remote access, better security

    ​SonicWall Cloud Secure Edge™ is a modern, cloud-native Security Service Edge (SSE) solution that addresses …Download Whitepaper
  • Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Insider threats continue to be a major cybersecurity risk in 2024. Explore more insights on …Download Whitepaper

Middle-sidebar-banner

Case Studies

  • How a Vietnamese D2C retailer built its own secure digital infrastructure

    How a Vietnamese D2C retailer built its own secure digital infrastructure

    Would your organization build your own digital infrastructure – including AI governance and cybersecurity – …Read more
  • Cyber protection for medical clinics in Singapore

    Cyber protection for medical clinics in Singapore

    As Singapore’s healthcare sector becomes increasingly digital and interconnected, clinics are facing heightened cyber risks, …Read more
  • India’s WazirX strengthens governance and digital asset security

    India’s WazirX strengthens governance and digital asset security

    Revamping its custody infrastructure using multi‑party computation tools has improved operational resilience and institutional‑grade safeguardsRead more
  • Bangladesh LGED modernizes communication while addressing data security concerns

    Bangladesh LGED modernizes communication while addressing data security concerns

    To meet emerging data localization/privacy regulations, the government engineering agency deploys a secure, unified digital …Read more

Bottom sidebar

Other News

  • LRQA Named ‘Best in Critical Infrastructure Protection’ at CybersecAsia Readers’ Choice Awards 2026

    Monday, September 21, 2026
    Prestigious regional recognition highlights LRQA’s …Read More »
  • Cyble and Cyber Security Council of UAE Sign MOU to Strengthen National Threat Intelligence Capabilities

    Thursday, September 17, 2026
    ABU DHABI, UAE, Sept. 17, …Read More »
  • Cohesity Research Finds Most Cyber Recovery Plans Are Built for the Wrong Outcome

    Thursday, September 17, 2026
    78% organizations prioritize restoring systems …Read More »
  • SU Group Secures Exclusive Distribution Rights for Portable X-Ray System in Hong Kong and Macau

    Tuesday, September 15, 2026
    Second International Distribution Deal of …Read More »
  • SU Group Holdings Limited Announces Proposed Acquisition of KM Safety Solution Company Limited

    Tuesday, September 15, 2026
    HONG KONG, Sept. 15, 2026 …Read More »
  • Our Brands
  • DigiconAsia
  • MartechAsia
  • Home
  • About Us
  • Contact Us
  • Sitemap
  • Privacy & Cookies
  • Terms of Use
  • Advertising & Reprint Policy
  • Media Kit
  • Subscribe
  • Manage Subscriptions
  • Newsletter

Copyright © 2026 CybersecAsia All Rights Reserved.