Cybersecurity News in Asia

RECENT STORIES:

SEGA moves faster with flow-based network monitoring
From frontier policy to boardroom action: how enterprises should gover...
How can APAC enterprises face AI governance questions deftly? Key ques...
China-linked cyber espionage group shifts focus to another brand of ro...
Cohesity Delivers New Managed Clean Room Capability to Enhance HCLTech...
Visa Launches Enhanced A2A Protect Innovations to Help Financial Insti...
LOGIN REGISTER
CybersecAsia
  • Features
    • Featured

      Dealing with agentic AI governance and resilience challenges

      Dealing with agentic AI governance and resilience challenges

      Tuesday, September 1, 2026, 11:51 AM Asia/Singapore | Features
    • Featured

      How well do you know your agent?

      How well do you know your agent?

      Thursday, August 20, 2026, 3:21 PM Asia/Singapore | Features
    • Featured

      Bringing proof of identity to the digital economy

      Bringing proof of identity to the digital economy

      Wednesday, August 19, 2026, 10:50 AM Asia/Singapore | Features
  • Opinions
  • Tips
  • Whitepapers
  • AWARDS 2026
  • Directory
  • E-Learning

Select Page

News

Taiwan high-speed rail spoofing case exposes OT governance gaps, not isolated vulnerabilities

By CybersecAsia editors | Tuesday, May 12, 2026, 9:41 AM Asia/Singapore

Taiwan high-speed rail spoofing case exposes OT governance gaps, not isolated vulnerabilities

When legacy OT is allowed to sit outside standard IT governance, blind spots/governance gaps can develop, say industry observers

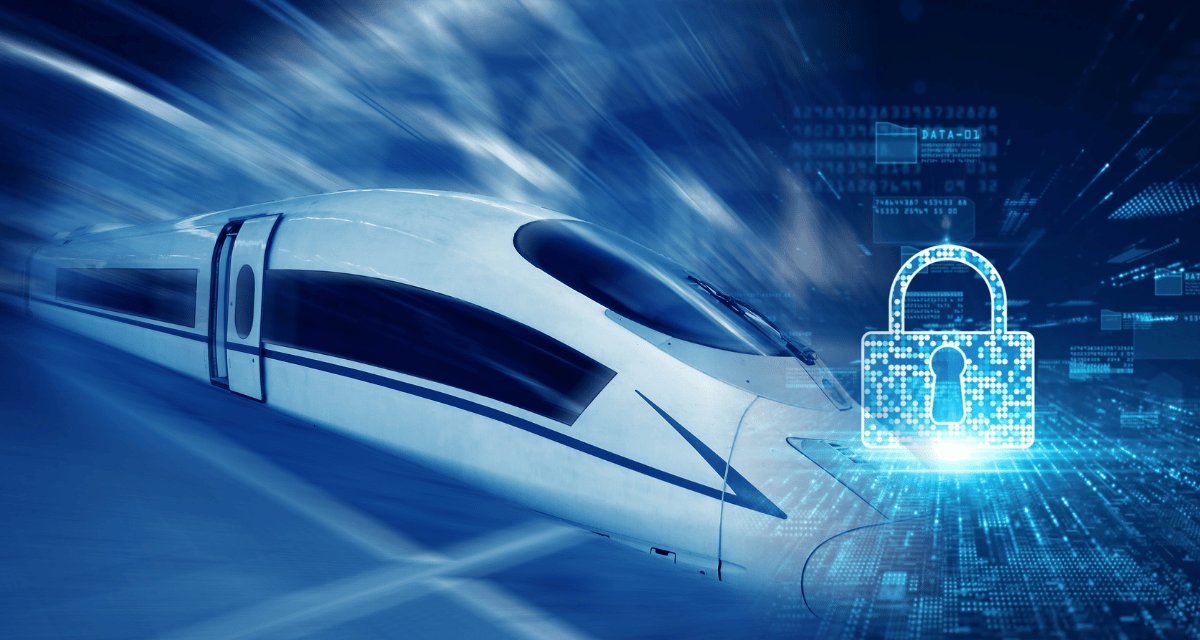
Taiwan’s High-Speed Rail has been forced into the spotlight after a student allegedly used radio-signal spoofing to trigger false emergency alerts, halting four trains for 48 minutes on 5 April 2026 and exposing how vulnerable critical infrastructure can be when old systems are not tightly governed.

The case is a reminder that a low-cost technical exploit can still create immediate operational disruption, even without physical access to the network. According to one perspective, BleepingComputer, the event was a basic but serious operational security failure: a case of software-defined radio equipment and handheld radios being used to transmit a false “General Alarm”, reinforcing that the disruption came from exploiting weak controls around rail communications rather than from any physical intrusion.

Another commentary, from the Computer Emergency Response Team (CERT) of Thailand, broadens the issue beyond one railway, highlighting how commercially available radio tools and aging infrastructure can be turned into real-world disruption, arguing that critical systems need continuous modernization, testing, and security assessment. That moves the story away from one student’s actions and towards the bigger question of whether transport operators are ready for the capabilities now available to low-cost attackers.

On 9 May, Stella Robertson of Domino Theory had thrown in a third take: that the breach was not evidence of a highly sophisticated adversary, but of poor operational discipline and long-neglected system hygiene. Its reporting has noted that the system’s keys may not have been rotated in nearly two decades, a detail that, if accurate, would make the incident as much about governance failure as technical weakness. Her report noted that hardening the cyber resilience of operational technology is a global challenge: “It involves legacy equipment and facilities, which often lack well-developed playbooks for situations that were not anticipated when the systems were first designed. These systems also tend to operate in a closed, internal loop that receives less scrutiny — people assume everything is fine as long as nothing major goes wrong.”

Finally, according to Takanori Nishiyama, SVP (APAC), Keeper Security, “the case illustrates a structural gap in (some parts of) the region where legacy interfaces and automated systems sit outside standard IT governance….” which can result in systemic blind spots in access control, oversight, and operational resilience.
Share:

PreviousLinux kernel zero day enables root privilege escalation across most distros
NextFraudulent Android apps offers illegal data retrieval service to millions of users

Related Posts

APAC battled growing levels of hacktivism, data leaks and more last year: data analysis

APAC battled growing levels of hacktivism, data leaks and more last year: data analysis

Monday, March 3, 2025

Phishing campaigns targeting Facebook business accounts on the rise

Phishing campaigns targeting Facebook business accounts on the rise

Tuesday, August 15, 2023

Free reverse engineering tool helps cyber defenders explore malware code easily

Free reverse engineering tool helps cyber defenders explore malware code easily

Thursday, August 13, 2020

Trend Micro acquires Cloud Conformity

Trend Micro acquires Cloud Conformity

Tuesday, October 22, 2019

Leave a reply Cancel reply

You must be logged in to post a comment.

Voters-draw/RCA-Sponsors

Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
previous arrow
next arrow

CybersecAsia Voting Placement

Gamification listing or Participate Now

PARTICIPATE NOW

Vote Now -Placement(Google Ads)

Top-Sidebar-banner

Whitepapers

  • Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Cyber threats have become more frequent and sophisticated, targeting organizations of all sizes across all …Download Whitepaper
  • Zero Trust Made Simple: Why it matters and how to get started

    Zero Trust Made Simple: Why it matters and how to get started

    Data breaches and cyberattacks are no longer limited to large, high-profile organizations.Download Whitepaper
  • Cloud Secure Edge: Remote access, better security

    Cloud Secure Edge: Remote access, better security

    ​SonicWall Cloud Secure Edge™ is a modern, cloud-native Security Service Edge (SSE) solution that addresses …Download Whitepaper
  • Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Insider threats continue to be a major cybersecurity risk in 2024. Explore more insights on …Download Whitepaper

Middle-sidebar-banner

Case Studies

  • How a Vietnamese D2C retailer built its own secure digital infrastructure

    How a Vietnamese D2C retailer built its own secure digital infrastructure

    Would your organization build your own digital infrastructure – including AI governance and cybersecurity – …Read more
  • Cyber protection for medical clinics in Singapore

    Cyber protection for medical clinics in Singapore

    As Singapore’s healthcare sector becomes increasingly digital and interconnected, clinics are facing heightened cyber risks, …Read more
  • India’s WazirX strengthens governance and digital asset security

    India’s WazirX strengthens governance and digital asset security

    Revamping its custody infrastructure using multi‑party computation tools has improved operational resilience and institutional‑grade safeguardsRead more
  • Bangladesh LGED modernizes communication while addressing data security concerns

    Bangladesh LGED modernizes communication while addressing data security concerns

    To meet emerging data localization/privacy regulations, the government engineering agency deploys a secure, unified digital …Read more

Bottom sidebar

Other News

  • Cohesity Delivers New Managed Clean Room Capability to Enhance HCLTech VaultNXT

    Wednesday, September 2, 2026
    Cohesity Clean Room solution and …Read More »
  • Visa Launches Enhanced A2A Protect Innovations to Help Financial Institutions Stop Fraud Before Money Leaves Accounts

    Wednesday, September 2, 2026
    New unified fraud score is …Read More »
  • Malaysia’s Cybersecurity Leaders to Convene at the 34th Edition Cyber Security Summit Malaysia 2026

    Tuesday, September 1, 2026
    Summit to Bring Together More …Read More »
  • ICAC Commissioner in Vienna to meet new UNODC Chief to foster anti-corruption strategic collaboration and unveil ICAC’s AI enforcement system “Tianma” at UNODC’s anti-graft conference

    Tuesday, September 1, 2026
    VIENNA, Sept. 1, 2026 /PRNewswire/ …Read More »
  • Visa Expands Support for its Clients and the Industry as Organisations Navigate New AI Era of Cybersecurity

    Friday, August 28, 2026
    Latest Visa Vulnerability Agentic Harness release …Read More »
  • Our Brands
  • DigiconAsia
  • MartechAsia
  • Home
  • About Us
  • Contact Us
  • Sitemap
  • Privacy & Cookies
  • Terms of Use
  • Advertising & Reprint Policy
  • Media Kit
  • Subscribe
  • Manage Subscriptions
  • Newsletter

Copyright © 2026 CybersecAsia All Rights Reserved.