Cybersecurity News in Asia

RECENT STORIES:

SEGA moves faster with flow-based network monitoring
AI pioneers and scientists urge international oversight to contain adv...
Advancing OT Cyber Readiness and Resilience in Southeast Asia
New AI supply chain threats that security teams need to manage
Deepfakes and impersonators can fool people, but they should not bypas...
FOMO Pay expands cross-border compliance infrastructure amid rising fr...
LOGIN REGISTER
CybersecAsia
  • Features
    • Featured

      Advancing OT Cyber Readiness and Resilience in Southeast Asia

      Advancing OT Cyber Readiness and Resilience in Southeast Asia

      Wednesday, October 14, 2026, 10:00 AM Asia/Singapore | Features, News, Newsletter, Sponsored
    • Featured

      How CISOs can set human boundaries for autonomous cybersecurity

      How CISOs can set human boundaries for autonomous cybersecurity

      Wednesday, October 7, 2026, 11:05 AM Asia/Singapore | Features, Newsletter, Tips
    • Featured

      Securing the agentic enterprise – at machine speed

      Securing the agentic enterprise – at machine speed

      Tuesday, October 6, 2026, 5:00 PM Asia/Singapore | Features, Newsletter
  • Opinions
  • Tips
  • Whitepapers
  • AWARDS 2026
  • Directory
  • E-Learning

Select Page

News

Researchers prove physical attacks expose weaknesses in CPU “trusted execution environments”

By CybersecAsia editors | Tuesday, October 7, 2025, 2:10 PM Asia/Singapore

Researchers prove physical attacks expose weaknesses in CPU “trusted execution environments”

Exposed flaws in trusted execution environments prompt urgent reworking of security strategies in cloud-based software apps and infrastructures.

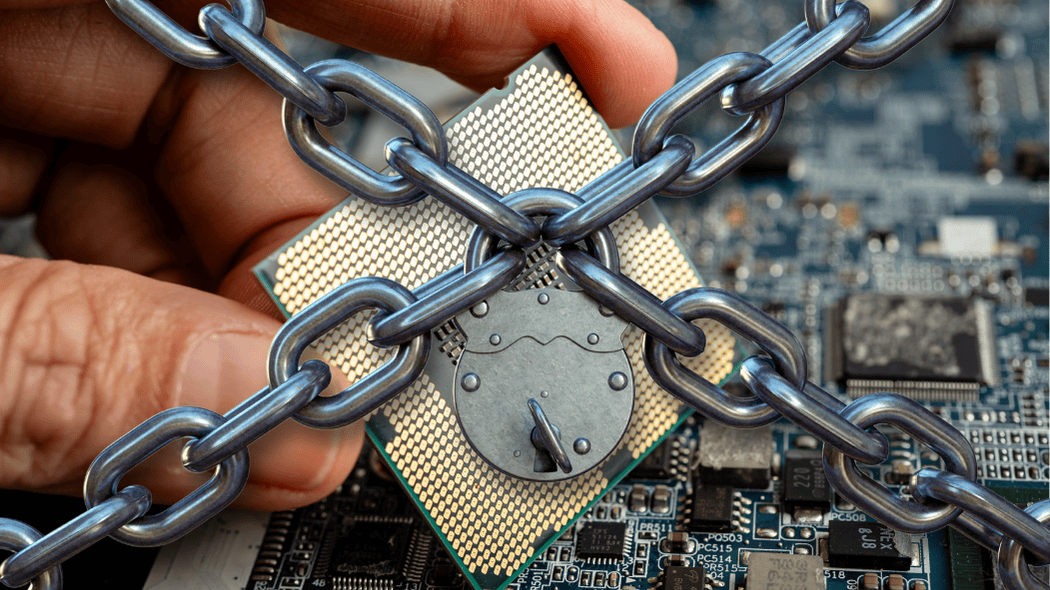
Security researchers have exposed new vulnerabilities that severely undermine the so-called trusted execution environments (TEEs) of the computer processors (central processing units or CPUs) of two manufacturers.

These TEEs, which are foundational to modern cloud and network security protocols, are embedded in CPUs from AMD and Intel, and they handle sensitive operations within encrypted zones to defend against unauthorized access in social media chat apps and cloud collaboration software.

On 30 September 2025, researchers unveiled two physical attacks, named “Battering RAM” and “Wiretap”, that circumvent TEE defenses. Both attacks exploit a critical design flaw: deterministic encryption, which generates identical ciphertext from identical plaintext at a given memory address.

By physically inserting a tiny device called an “interposer” between the processor and memory module, attackers can monitor and manipulate encrypted data as it travels within the system:

  • Battering RAM not only allows decryption of protected information but also permits injection of malicious payloads or the destruction of critical processes, potentially letting attackers place backdoors or corrupt authenticated data.
  • Wiretap operates covertly to passively decrypt streamed data without alerting existing security monitors.

A key point highlighted by both chipmakers is that their official threat models do not account for direct physical access to hardware, meaning such scenarios are excluded from their security guarantees. Nevertheless, industry feedback and online commentary emphasize that disregard for physical attacks is risky. One Reddit user has noted: When it comes to hardware security, “physical access equates to game over.”

With this threat development, organizations relying on TEEs will need to reconsider their risk profiles and defense assumptions, particularly for systems placed in potentially vulnerable locations such as third-party data centers. As the research makes clear, comprehensive security strategies must encompass not just remote attacks but also threats arising from direct hardware compromise.

Both chipmakers have published advisories / disclaimers for these hardware cracks.


Share:

PreviousPsst… know anyone interested in selling his/her identity?
NextAugust CVE with severity of 9.8 vulnerability amplified by ransomware group

Related Posts

Three critical RCE flaws could have allowed malicious takeover of AI servers

Three critical RCE flaws could have allowed malicious takeover of AI servers

Tuesday, August 5, 2025

Indonesia’s central bank admits to suffering ransomware attack in Dec 2021

Indonesia’s central bank admits to suffering ransomware attack in Dec 2021

Tuesday, January 25, 2022

Amid crumbling public faith in online information, are voters worried about deepfakes?

Amid crumbling public faith in online information, are voters worried about deepfakes?

Wednesday, August 28, 2024

2021 ended with the ‘terrifying three’ in the spotlight

2021 ended with the ‘terrifying three’ in the spotlight

Monday, January 17, 2022

Leave a reply Cancel reply

You must be logged in to post a comment.

Voters-draw/RCA-Sponsors

Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
previous arrow
next arrow

CybersecAsia Voting Placement

Gamification listing or Participate Now

LEARN MORE

Vote Now -Placement(Google Ads)

Top-Sidebar-banner

Whitepapers

  • Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Cyber threats have become more frequent and sophisticated, targeting organizations of all sizes across all …Download Whitepaper
  • Zero Trust Made Simple: Why it matters and how to get started

    Zero Trust Made Simple: Why it matters and how to get started

    Data breaches and cyberattacks are no longer limited to large, high-profile organizations.Download Whitepaper
  • Cloud Secure Edge: Remote access, better security

    Cloud Secure Edge: Remote access, better security

    ​SonicWall Cloud Secure Edge™ is a modern, cloud-native Security Service Edge (SSE) solution that addresses …Download Whitepaper
  • Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Insider threats continue to be a major cybersecurity risk in 2024. Explore more insights on …Download Whitepaper

Middle-sidebar-banner

Case Studies

  • FOMO Pay expands cross-border compliance infrastructure amid rising fraud risks

    FOMO Pay expands cross-border compliance infrastructure amid rising fraud risks

    To unify onboarding and ongoing reviews the payment firm adds identity, liveness, business-ownership, sanctions screening …Read more
  • How a Vietnamese D2C retailer built its own secure digital infrastructure

    How a Vietnamese D2C retailer built its own secure digital infrastructure

    Would your organization build your own digital infrastructure – including AI governance and cybersecurity – …Read more
  • Cyber protection for medical clinics in Singapore

    Cyber protection for medical clinics in Singapore

    As Singapore’s healthcare sector becomes increasingly digital and interconnected, clinics are facing heightened cyber risks, …Read more
  • India’s WazirX strengthens governance and digital asset security

    India’s WazirX strengthens governance and digital asset security

    Revamping its custody infrastructure using multi‑party computation tools has improved operational resilience and institutional‑grade safeguardsRead more

Bottom sidebar

Other News

  • From Defence Cooperation to Shared Security: Building a Resilient Pakistan-China Partnership

    Friday, October 9, 2026
    QINGDAO, China, Oct. 9, 2026 …Read More »
  • CyberDSA Sets 19 – 21 October 2027 Return as Industry Participation Builds at Fourth Edition

    Thursday, October 8, 2026
    CyberDSA moves towards its milestone …Read More »
  • CyberLogitec Brings Tag-Free Collision Prevention to Busan New Port

    Tuesday, October 6, 2026
    Digital twin places workers and …Read More »
  • Aligning with Global Regulations: iMQ Technology’s SQ713x Secure Element Achieves SESIP and PSA Certified Level 3

    Monday, October 5, 2026
    Passes Keysight’s physical attack testing …Read More »
  • Cymulate Receives Frost & Sullivan’s 2026 Indian Competitive Strategy Leadership Recognition for Advancing Continuous Security Validation

    Monday, October 5, 2026
    The recognition highlights Cymulate’s competitive …Read More »
  • Our Brands
  • DigiconAsia
  • MartechAsia
  • Home
  • About Us
  • Contact Us
  • Sitemap
  • Privacy & Cookies
  • Terms of Use
  • Advertising & Reprint Policy
  • Media Kit
  • Subscribe
  • Manage Subscriptions
  • Newsletter

Copyright © 2026 CybersecAsia All Rights Reserved.