Cybersecurity News in Asia

RECENT STORIES:

SEGA moves faster with flow-based network monitoring
The new cybersecurity imperative is continuous resilience
Autonomous AI agents now exploit software vulnerabilities with little ...
Malicious JavaScript hits visitors to 178 websites through Web Experim...
Will your AI agents always do only what you want them to?
LOGIN REGISTER
CybersecAsia
  • Features
    • Featured

      Will your AI agents always do only what you want them to?

      Will your AI agents always do only what you want them to?

      Thursday, November 19, 2026, 10:09 AM Asia/Singapore | Features
    • Featured

      Curbing S E Asia’s tsunami of gaming scams and payment fraud

      Curbing S E Asia’s tsunami of gaming scams and payment fraud

      Wednesday, November 18, 2026, 12:24 PM Asia/Singapore | Features, Newsletter
    • Featured

      From VPNs to zero-trust access

      From VPNs to zero-trust access

      Tuesday, November 17, 2026, 1:00 PM Asia/Singapore | Features, Newsletter, Sponsored
  • Opinions
  • Tips
  • Whitepapers
  • AWARDS 2026
  • Directory
  • E-Learning

Select Page

News

Multi-supply-chain breach disclosed, involving customer design and personnel data

By CybersecAsia editors | Wednesday, June 24, 2026, 12:07 PM Asia/Singapore

Multi-supply-chain breach disclosed, involving customer design and personnel data

Reportedly, over 630GB across 204,300 files allegedly leaked, including data from multiple big tech firms being offered for sale.

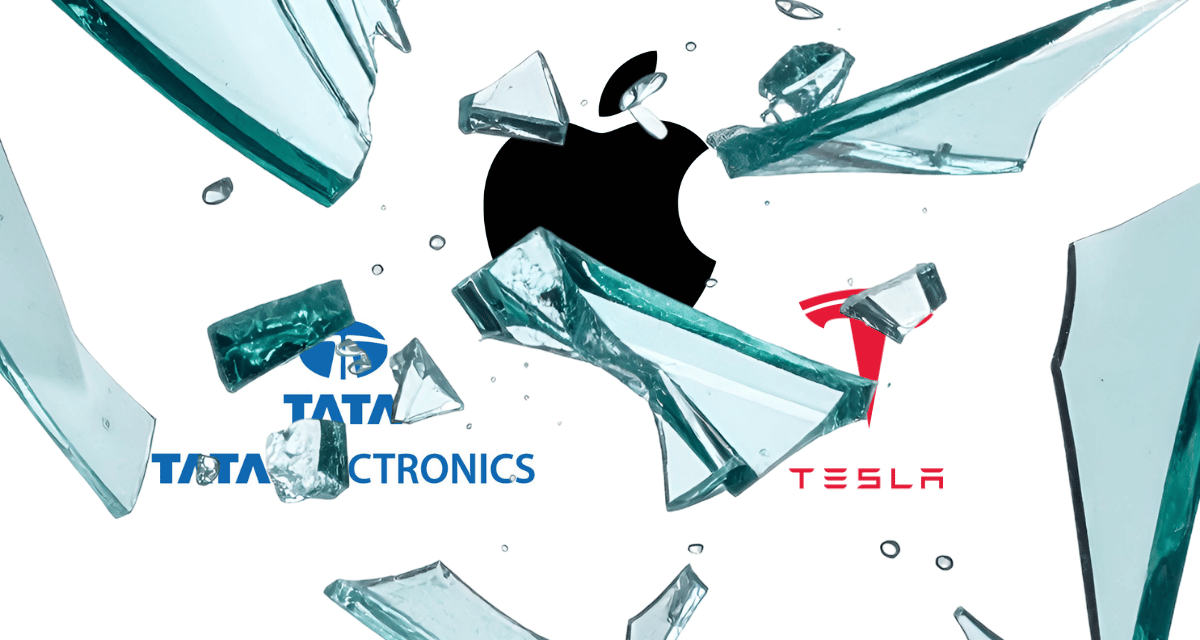
A key Indian semiconductor and electronics manufacture has announced on 22 June 2026 that it had detected a cybersecurity incident on parts of its systems several weeks ago and had immediately activated its incident-response procedures.

While stressing that the breach did not interrupt operations across the businesses, Tata Electronics’s statement it did not provide a detailed accounting of what was taken, or how long the attackers may have had access.

According to a hacker forum post, the scope of the leak appears substantial, with cybercriminals offering more than 630 gigabytes of data across more than 204,300 files, described as obtain through a span of many years rather than through a single isolated event. That scale suggests the attackers may have gathered a broad mix of operational records, internal communications, and technical documents before the breach was discovered.

A TechCrunch report noted that it had reviewed a sample of the files and found documents that appeared to include Apple supplier specifications and Tesla manufacturing materials, though the news outlet could not independently verify whether every file was authentic, or whether the entire trove was complete. If accurate, that would point to exposure not just of Tata Electronics’ own internal data, but also of highly sensitive information tied to major customers.

The leaked cache was also described as including Outlook email conversations, SAP-related information, event logs, and employee passport copies, including documents tied to foreign nationals. Cybersecurity researcher Rajshekhar Rajaharia told TechCrunch that the forum listing appeared to include files connected to several Tata Electronics customers, among them Apple and Tesla.

Reuters has reported that Tata Electronics had begun notifying some employees at its iPhone assembly operations about the incident last week. The same report said Apple was examining its possible exposure, and that a ransom demand had been made to Tata Electronics. That combination of customer notification, internal review, and extortion pressure suggests the firm is treating the incident as a serious supply-chain security matter, not just a routine IT breach.

The incident also highlights how much risk can concentrate in global manufacturing networks. The incident is not only about stolen files, but also about the fragility of the interconnected systems that support high-volume electronics production.
Share:

PreviousRansomware emerges as the costliest cyber insurance claim component: analysis
NextDJI Enterprise Advances Industry with New Framework for Dock as First Responder (DFR) Deployments

Related Posts

Lessons to learn from the KuCoin breach

Lessons to learn from the KuCoin breach

Wednesday, September 30, 2020

Address machine identity risks, protect AI, and improve security strategies: survey

Address machine identity risks, protect AI, and improve security strategies: survey

Tuesday, March 25, 2025

Newly discovered UEFI motherboard firmware trojan found to have existed since 2016

Newly discovered UEFI motherboard firmware trojan found to have existed since 2016

Wednesday, July 27, 2022

Are SMEs in South-east Asia prone to paying off cyber ransoms?

Are SMEs in South-east Asia prone to paying off cyber ransoms?

Tuesday, August 16, 2022

Leave a reply Cancel reply

You must be logged in to post a comment.

Voters-draw/RCA-Sponsors

Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
previous arrow
next arrow

CybersecAsia Voting Placement

Gamification listing or Participate Now

LEARN MORE

Vote Now -Placement(Google Ads)

Top-Sidebar-banner

Whitepapers

  • Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Cyber threats have become more frequent and sophisticated, targeting organizations of all sizes across all …Download Whitepaper
  • Zero Trust Made Simple: Why it matters and how to get started

    Zero Trust Made Simple: Why it matters and how to get started

    Data breaches and cyberattacks are no longer limited to large, high-profile organizations.Download Whitepaper
  • Cloud Secure Edge: Remote access, better security

    Cloud Secure Edge: Remote access, better security

    ​SonicWall Cloud Secure Edge™ is a modern, cloud-native Security Service Edge (SSE) solution that addresses …Download Whitepaper
  • Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Insider threats continue to be a major cybersecurity risk in 2024. Explore more insights on …Download Whitepaper

Middle-sidebar-banner

Case Studies

  • FOMO Pay expands cross-border compliance infrastructure amid rising fraud risks

    FOMO Pay expands cross-border compliance infrastructure amid rising fraud risks

    To unify onboarding and ongoing reviews the payment firm adds identity, liveness, business-ownership, sanctions screening …Read more
  • How a Vietnamese D2C retailer built its own secure digital infrastructure

    How a Vietnamese D2C retailer built its own secure digital infrastructure

    Would your organization build your own digital infrastructure – including AI governance and cybersecurity – …Read more
  • Cyber protection for medical clinics in Singapore

    Cyber protection for medical clinics in Singapore

    As Singapore’s healthcare sector becomes increasingly digital and interconnected, clinics are facing heightened cyber risks, …Read more
  • India’s WazirX strengthens governance and digital asset security

    India’s WazirX strengthens governance and digital asset security

    Revamping its custody infrastructure using multi‑party computation tools has improved operational resilience and institutional‑grade safeguardsRead more

Bottom sidebar

Other News

  • GovWare 2026 closes with a clear focus on securing AI that can act

    Thursday, November 19, 2026
    Across the conference and exhibition, …Read More »
  • Visa Launches Threat Intelligence Platform to Strengthen Cyber and Fraud Defense

    Wednesday, November 18, 2026
    New research commissioned by Visa …Read More »
  • As Hijacked Billboards Make Headlines, CAYIN SMP Players Keep Screens in Owners’ Hands

    Monday, November 16, 2026
    After a run of hijacked …Read More »
  • Cohesity Expands Cyber Resilience and AI Data Capabilities for Microsoft Environments

    Friday, November 13, 2026
    Recent innovations strengthen data security …Read More »
  • Cequence Security and KPMG Collaborate on Joint Report Examining how Organisations can Govern and Secure Agentic AI

    Wednesday, November 11, 2026
    New Cequence data in the …Read More »
  • Our Brands
  • DigiconAsia
  • MartechAsia
  • Home
  • About Us
  • Contact Us
  • Sitemap
  • Privacy & Cookies
  • Terms of Use
  • Advertising & Reprint Policy
  • Media Kit
  • Subscribe
  • Manage Subscriptions
  • Newsletter

Copyright © 2026 CybersecAsia All Rights Reserved.