Cybersecurity News in Asia

RECENT STORIES:

SEGA moves faster with flow-based network monitoring
The new cybersecurity imperative is continuous resilience
Autonomous AI agents now exploit software vulnerabilities with little ...
Malicious JavaScript hits visitors to 178 websites through Web Experim...
Will your AI agents always do only what you want them to?
LOGIN REGISTER
CybersecAsia
  • Features
    • Featured

      Will your AI agents always do only what you want them to?

      Will your AI agents always do only what you want them to?

      Thursday, November 19, 2026, 10:09 AM Asia/Singapore | Features
    • Featured

      Curbing S E Asia’s tsunami of gaming scams and payment fraud

      Curbing S E Asia’s tsunami of gaming scams and payment fraud

      Wednesday, November 18, 2026, 12:24 PM Asia/Singapore | Features, Newsletter
    • Featured

      From VPNs to zero-trust access

      From VPNs to zero-trust access

      Tuesday, November 17, 2026, 1:00 PM Asia/Singapore | Features, Newsletter, Sponsored
  • Opinions
  • Tips
  • Whitepapers
  • AWARDS 2026
  • Directory
  • E-Learning

Select Page

News

Mid-game e-sports wallhacking: will organizers finally take the hint?

By CybersecAsia editors | Thursday, April 4, 2024, 5:27 PM Asia/Singapore

Mid-game e-sports wallhacking: will organizers finally take the hint?

Griefing, swatting and other malicious hacking trends have hit new high scores of concern and frustration: time to harden event defenses!

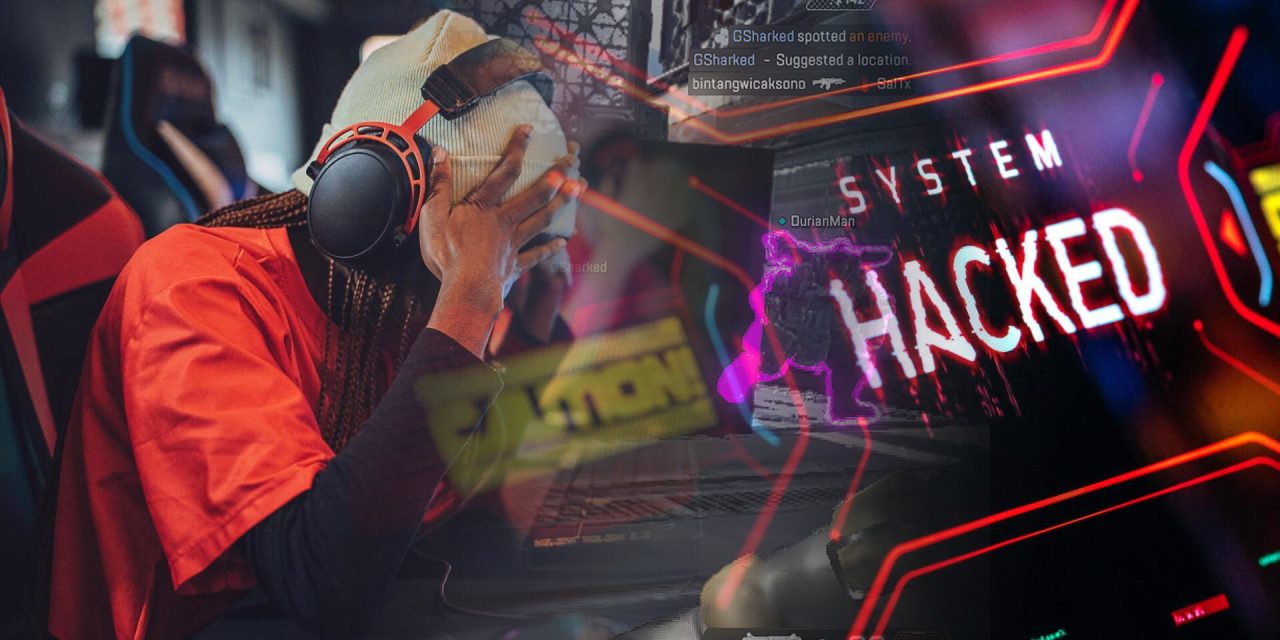
Recently, two competitive e-sports players were hacked mid-game during the Apex Legends Global Series. This had led to the organizers postponing the tournament.

Hackers had apparently applied what is called a “wallhack” to the targeted participants, making it appear they were cheating in the competition.

The affected players promptly announced that they were being hacked and not in control of their terminals, showing proof with onscreen messages from the hacker announcing: “Apex hacking global series by Destroyer2009 & R4ndom.”

Subsequently, it was announced that “no remote code execution vulnerability” within the gaming infrastructure had been exploited for the hack. 

On 20 March, the hacker that had supposedly been involved in the incidents had publicly announced that it was “just for fun”, and refused to reveal the exact hacking method, stating that the gaming firms offer no financial compensation for players who find and report bugs and exploits.

Moral of the story?

Normally, game designers try to prevent hackers from creating software that lets them play games in ways that ruin the fun for other players. The games industry has a unique attack surface that does not necessarily apply as acutely to other industries: Player Fun.

According to Jamie Boote, Associate Principal Consultant, Synopsys Software Integrity Group, when people on the internet attempt to disrupt other people’s enjoyment (known as ‘griefing’) e-sports streaming becomes a popular target. “Examples can range from the digital to the physical. Digital griefing can be trying to join the streamer’s multiplayer gaming session and harassing the player in game or attempting to identify and hack into the streamer’s PC to disrupt their stream. More dangerous examples of criminal harassment move beyond griefing and could involve calling 911, deceiving the responders into believing that there is a dangerous situation at the streamer’s home address, and claiming that there is an armed gunman or other dangerous situation. Due to the SWAT team’s response, this practice is known as ‘swatting’ and has resulted in fatal shootings.”

Boote has recommended e-sports organizers to adopt strong measures to protect their own infrastructure: from providing hardening guidelines, to mandating that participants install software security agents similar to corporate Bring Your Own Device plans, to providing and mandating centrally controlled computers and networking equipment. “Organizers will have to assume that it’s a matter of when, not if, an event will happen like this again, and know how to prevent or minimize disruption (when) it does,” he said.
Share:

PreviousInaugural Milipol Asia-Pacific & TechX Summit powers up innovation for homeland security
NextIs AI viewed as a double-edged sword by Japan SMEs?

Related Posts

Securing a distributed workforce in a post-pandemic world

Securing a distributed workforce in a post-pandemic world

Saturday, December 5, 2020

Securing the agentic enterprise – at machine speed

Securing the agentic enterprise – at machine speed

Tuesday, October 6, 2026

Lazarus Group likely weaponizing legitimate software to target firms with poor patching discipline

Lazarus Group likely weaponizing legitimate software to target firms with poor patching discipline

Tuesday, November 7, 2023

Know the five commandments of online safety

Know the five commandments of online safety

Thursday, August 26, 2021

Leave a reply Cancel reply

You must be logged in to post a comment.

Voters-draw/RCA-Sponsors

Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
previous arrow
next arrow

CybersecAsia Voting Placement

Gamification listing or Participate Now

LEARN MORE

Vote Now -Placement(Google Ads)

Top-Sidebar-banner

Whitepapers

  • Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Cyber threats have become more frequent and sophisticated, targeting organizations of all sizes across all …Download Whitepaper
  • Zero Trust Made Simple: Why it matters and how to get started

    Zero Trust Made Simple: Why it matters and how to get started

    Data breaches and cyberattacks are no longer limited to large, high-profile organizations.Download Whitepaper
  • Cloud Secure Edge: Remote access, better security

    Cloud Secure Edge: Remote access, better security

    ​SonicWall Cloud Secure Edge™ is a modern, cloud-native Security Service Edge (SSE) solution that addresses …Download Whitepaper
  • Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Insider threats continue to be a major cybersecurity risk in 2024. Explore more insights on …Download Whitepaper

Middle-sidebar-banner

Case Studies

  • FOMO Pay expands cross-border compliance infrastructure amid rising fraud risks

    FOMO Pay expands cross-border compliance infrastructure amid rising fraud risks

    To unify onboarding and ongoing reviews the payment firm adds identity, liveness, business-ownership, sanctions screening …Read more
  • How a Vietnamese D2C retailer built its own secure digital infrastructure

    How a Vietnamese D2C retailer built its own secure digital infrastructure

    Would your organization build your own digital infrastructure – including AI governance and cybersecurity – …Read more
  • Cyber protection for medical clinics in Singapore

    Cyber protection for medical clinics in Singapore

    As Singapore’s healthcare sector becomes increasingly digital and interconnected, clinics are facing heightened cyber risks, …Read more
  • India’s WazirX strengthens governance and digital asset security

    India’s WazirX strengthens governance and digital asset security

    Revamping its custody infrastructure using multi‑party computation tools has improved operational resilience and institutional‑grade safeguardsRead more

Bottom sidebar

Other News

  • GovWare 2026 closes with a clear focus on securing AI that can act

    Thursday, November 19, 2026
    Across the conference and exhibition, …Read More »
  • Visa Launches Threat Intelligence Platform to Strengthen Cyber and Fraud Defense

    Wednesday, November 18, 2026
    New research commissioned by Visa …Read More »
  • As Hijacked Billboards Make Headlines, CAYIN SMP Players Keep Screens in Owners’ Hands

    Monday, November 16, 2026
    After a run of hijacked …Read More »
  • Cohesity Expands Cyber Resilience and AI Data Capabilities for Microsoft Environments

    Friday, November 13, 2026
    Recent innovations strengthen data security …Read More »
  • Cequence Security and KPMG Collaborate on Joint Report Examining how Organisations can Govern and Secure Agentic AI

    Wednesday, November 11, 2026
    New Cequence data in the …Read More »
  • Our Brands
  • DigiconAsia
  • MartechAsia
  • Home
  • About Us
  • Contact Us
  • Sitemap
  • Privacy & Cookies
  • Terms of Use
  • Advertising & Reprint Policy
  • Media Kit
  • Subscribe
  • Manage Subscriptions
  • Newsletter

Copyright © 2026 CybersecAsia All Rights Reserved.