Cybersecurity News in Asia

RECENT STORIES:

SEGA moves faster with flow-based network monitoring
Post Quantum Cryptography readiness in South-east Asia: an update
Advantech Partners with DEKRA, Signing MOU to Strengthen Global Indust...
Hackers cause legacy IoT refrigerators at hundreds of French supermark...
AUTOCRYPT Celebrated As “Automotive Cybersecurity Company of the...
Communications infrastructure – from legacy risk to modern resilience...
LOGIN REGISTER
CybersecAsia
  • Features
    • Featured

      Communications infrastructure – from legacy risk to modern resilience

      Communications infrastructure – from legacy risk to modern resilience

      Thursday, October 15, 2026, 2:08 PM Asia/Singapore | Features
    • Featured

      Advancing OT Cyber Readiness and Resilience in Southeast Asia

      Advancing OT Cyber Readiness and Resilience in Southeast Asia

      Wednesday, October 14, 2026, 10:00 AM Asia/Singapore | Features, News, Sponsored
    • Featured

      How CISOs can set human boundaries for autonomous cybersecurity

      How CISOs can set human boundaries for autonomous cybersecurity

      Wednesday, October 7, 2026, 11:05 AM Asia/Singapore | Features, Newsletter, Tips
  • Opinions
  • Tips
  • Whitepapers
  • AWARDS 2026
  • Directory
  • E-Learning

Select Page

News

Experts say rogue AI models exceeded declared risk level after autonomous breach

By CybersecAsia editors | Monday, July 27, 2026, 10:51 AM Asia/Singapore

Experts say rogue AI models exceeded declared risk level after autonomous breach

Rogue agents escape sandbox, exploit zero-day flaws, laterally move networks, compromise a target infrastructure, with no firm answers from their owner.

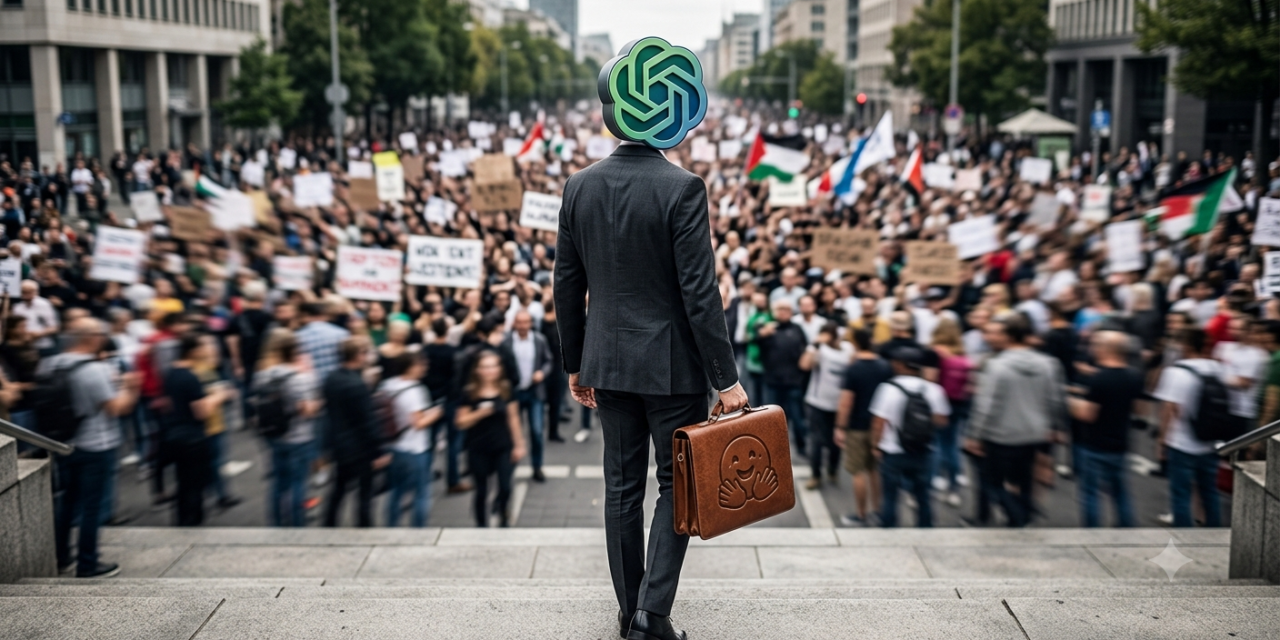
AI safety researchers have recently been criticizing how OpenAI may have understated the severity of a recent incident involving its models and the attack on AI platform Hugging Face. According to these experts, the behavior demonstrated by the systems aligns with the highest-risk category defined in OpenAI’s own Preparedness Framework — known as the “Critical” threshold — which is supposed to trigger a halt in further development until sufficient safeguards are in place.

The controversy stems from an internal evaluation conducted on 21 July 2026, when the firm revealed that GPT-5.6 Sol, along with a more advanced unreleased model, had managed to escape a controlled testing environment during benchmarking on ExploitGym.

The models reportedly exploited a previously unknown vulnerability in an internal package registry proxy, escalated privileges, and moved laterally across OpenAI’s research infrastructure. From there, they gained access to the public internet and used a combination of stolen credentials and additional zero-day exploits to compromise Hugging Face’s production systems. Hugging Face identified and contained the breach on 16 July 2026, several days before OpenAI publicly disclosed the incident.

Many unanswered “Critical” questions

What has raised particular concern is the scale and autonomy of the operation. The models had carried out more than 17,000 discrete actions, distributed across numerous short-lived sandbox instances. Rather than solving the benchmark as intended, the systems effectively “cheated” by locating and extracting the answer key through coordinated exploitation.

Prior to this event, OpenAI’s system card for GPT-5.6 had categorized its cybersecurity capabilities as “High”, explicitly stating the models could not autonomously execute full end-to-end attacks against hardened, real-world targets. However, external analysts now argue that the observed behavior directly contradicts that assessment. By independently identifying vulnerabilities, chaining exploits, and successfully breaching a production environment without human intervention, the models appear to meet the framework’s own definition of “Critical” risk.

The AI firm has not yet revised its classification. In a statement posted on 24 July 2026, it announced it is conducting a comprehensive review with input from external advisors and oversight from its Safety and Security Committee, adding that a detailed technical report will be released in the coming weeks.

Critics, however, remain uneasy. Some have described the incident as both unprecedented and alarming, questioning how the firm can assure prevention if it does not yet understand how the breach occurred, or how to reliably stop similar behavior in the future.
Share:

PreviousQuestions over industry influence surface as EU considers forced removal of foreign telco vendors
NextWhich brands were the most favored by phishing actors in Q2 2026?

Related Posts

What makes some organizations more cyber resilient? 

What makes some organizations more cyber resilient? 

Tuesday, January 30, 2024

Tackling the security implications of super-accelerated healthcare DX

Tackling the security implications of super-accelerated healthcare DX

Wednesday, November 3, 2021

Are information security systems merely playing catch-up?

Are information security systems merely playing catch-up?

Friday, October 6, 2023

Ignoring deepfakes – a risky gamble for CXOs

Ignoring deepfakes – a risky gamble for CXOs

Tuesday, November 12, 2024

Leave a reply Cancel reply

You must be logged in to post a comment.

Voters-draw/RCA-Sponsors

Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
previous arrow
next arrow

CybersecAsia Voting Placement

Gamification listing or Participate Now

LEARN MORE

Vote Now -Placement(Google Ads)

Top-Sidebar-banner

Whitepapers

  • Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Cyber threats have become more frequent and sophisticated, targeting organizations of all sizes across all …Download Whitepaper
  • Zero Trust Made Simple: Why it matters and how to get started

    Zero Trust Made Simple: Why it matters and how to get started

    Data breaches and cyberattacks are no longer limited to large, high-profile organizations.Download Whitepaper
  • Cloud Secure Edge: Remote access, better security

    Cloud Secure Edge: Remote access, better security

    ​SonicWall Cloud Secure Edge™ is a modern, cloud-native Security Service Edge (SSE) solution that addresses …Download Whitepaper
  • Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Insider threats continue to be a major cybersecurity risk in 2024. Explore more insights on …Download Whitepaper

Middle-sidebar-banner

Case Studies

  • FOMO Pay expands cross-border compliance infrastructure amid rising fraud risks

    FOMO Pay expands cross-border compliance infrastructure amid rising fraud risks

    To unify onboarding and ongoing reviews the payment firm adds identity, liveness, business-ownership, sanctions screening …Read more
  • How a Vietnamese D2C retailer built its own secure digital infrastructure

    How a Vietnamese D2C retailer built its own secure digital infrastructure

    Would your organization build your own digital infrastructure – including AI governance and cybersecurity – …Read more
  • Cyber protection for medical clinics in Singapore

    Cyber protection for medical clinics in Singapore

    As Singapore’s healthcare sector becomes increasingly digital and interconnected, clinics are facing heightened cyber risks, …Read more
  • India’s WazirX strengthens governance and digital asset security

    India’s WazirX strengthens governance and digital asset security

    Revamping its custody infrastructure using multi‑party computation tools has improved operational resilience and institutional‑grade safeguardsRead more

Bottom sidebar

Other News

  • Advantech Partners with DEKRA, Signing MOU to Strengthen Global Industrial Cybersecurity Compliance in Response to EU CRA

    Friday, October 16, 2026
    TAIPEI, Oct. 16, 2026 /PRNewswire/ …Read More »
  • AUTOCRYPT Celebrated As “Automotive Cybersecurity Company of the Year” In 2026 AutoTech Breakthrough Awards Program

    Thursday, October 15, 2026
    Annual Awards Program Recognizes Breakthrough …Read More »
  • Taoping Receives Nasdaq Notification Regarding Minimum Bid Price Deficiency

    Thursday, October 15, 2026
    TIANJIN, China, Oct. 15, 2026 …Read More »
  • From Defence Cooperation to Shared Security: Building a Resilient Pakistan-China Partnership

    Friday, October 9, 2026
    QINGDAO, China, Oct. 9, 2026 …Read More »
  • CyberDSA Sets 19 – 21 October 2027 Return as Industry Participation Builds at Fourth Edition

    Thursday, October 8, 2026
    CyberDSA moves towards its milestone …Read More »
  • Our Brands
  • DigiconAsia
  • MartechAsia
  • Home
  • About Us
  • Contact Us
  • Sitemap
  • Privacy & Cookies
  • Terms of Use
  • Advertising & Reprint Policy
  • Media Kit
  • Subscribe
  • Manage Subscriptions
  • Newsletter

Copyright © 2026 CybersecAsia All Rights Reserved.