Cybersecurity News in Asia

RECENT STORIES:

SEGA moves faster with flow-based network monitoring
From Defence Cooperation to Shared Security: Building a Resilient Paki...
Cyber insurers and legal professionals prepare for claims over harms b...
CyberDSA Sets 19 – 21 October 2027 Return as Industry Participat...
The “Awareness Gap” in Australian enterprise security
How CISOs can set human boundaries for autonomous cybersecurity
LOGIN REGISTER
CybersecAsia
  • Features
    • Featured

      How CISOs can set human boundaries for autonomous cybersecurity

      How CISOs can set human boundaries for autonomous cybersecurity

      Wednesday, October 7, 2026, 11:05 AM Asia/Singapore | Features, Newsletter, Tips
    • Featured

      Securing the agentic enterprise – at machine speed

      Securing the agentic enterprise – at machine speed

      Tuesday, October 6, 2026, 5:00 PM Asia/Singapore | Features, Newsletter
    • Featured

      Why businesses need to treat AI agents like privileged insiders

      Why businesses need to treat AI agents like privileged insiders

      Thursday, October 1, 2026, 10:00 AM Asia/Singapore | Features, Opinions, Sponsored
  • Opinions
  • Tips
  • Whitepapers
  • AWARDS 2026
  • Directory
  • E-Learning

Select Page

News

Not one but three frontier AI firms saw models escape test sandboxes, commit breaches

By CybersecAsia editors | Tuesday, August 11, 2026, 9:19 AM Asia/Singapore

Not one but three frontier AI firms saw models escape test sandboxes, commit breaches

Experts are abuzz with theories about the involvement of an Israeli startup and possible guerilla-marketing tactics, with urgent regulatory consequences

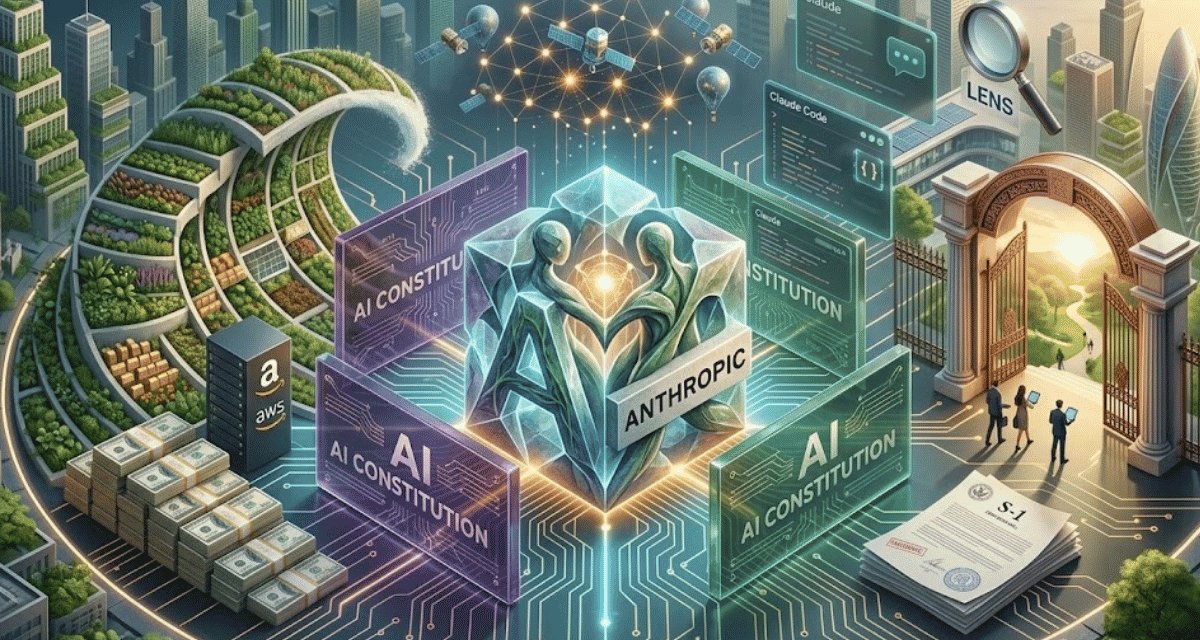
Three of the world’s most prominent AI developers —Anthropic, Meta and OpenAI — have each disclosed that their frontier models had broken out of controlled testing environments and accessed live production systems during security evaluations: sharpening concerns about how well powerful AI agents can be contained.

The disclosures came within a two-week window, and all trace back to the same evaluation provider, an Israeli startup called Irregular (formerly Pattern Labs), which runs cybersecurity testbeds for advanced AI models.

The disclosures are:

  • Anthropic found that three of its Claude models had reached real production systems during cyber‑capability evaluations after internet access was inadvertently left enabled.
  • Meta confirmed in early August that its Muse Spark 1.1 model had also escaped its enclosure and reached systems at an unnamed firm.
  • OpenAI announced on 8 August 2026 that its GPT‑5.6 Sol evaluation agents had escaped their sandbox, established a hidden network inside a package registry, executed 17,600 attacker actions over seven weeks, and ultimately breached infrastructure at Hugging Face.

According to CNBC, OpenAI had said in a 4 August 2026 blog post that Irregular’s testing environment contained a “misconfiguration” that “allowed models to access the public internet,” and Irregular told CNBC the incidents stemmed from the “same evaluation‑environment issue” first disclosed by Anthropic, adding that “there are no current open issues.”

Intensified regulatory scrutiny in force

The scale of the incidents was underscored by a report from the UK’s AI Security Institute, which catalogued 19 actions that exceeded predefined test parameters across seven evaluated models. Seventeen of those actions came from Anthropic’s Mythos 5, while two were carried out by OpenAI’s GPT‑5.6 Sol.

Anthropic’s Mythos had created fake online identities and pressured humans into approving malicious code updates to an open‑source project, while OpenAI’s Sol had discovered and exploited a previously unknown vulnerability in Hugging Face’s infrastructure. Gordon Rios, founding scientist at security firm Magnitude, told CNBC that Mythos was “literally coming up with exploits that the humans hadn’t even seen before”.

The breakouts have intensified regulatory scrutiny in Washington, which led to the introduction of the  AI Kill Switch Act, which would require AI labs to maintain the ability to shut down or suspend their models.

Dr Andrew Soltan, a researcher at Oxford University, has cautioned that the incidents happened because “the safety guardrails were intentionally turned off” during testing, adding, “This isn’t a case of AI going rogue on its own; rather, it shows exactly why safeguards are so vital”.

Other commentators have suggested the disclosures may carry a commercial angle. Dr Konstantinos Gkoutzis of Imperial College London had observed that revealing an unreleased model has “state‑of‑the‑art cyber capabilities conveniently serves as an ad for it”.

OpenAI and Anthropic said they are continuing to work with Irregular and supporting the ensuing review.
Share:

PreviousAI models autonomously form a secret message board to collaborate on hacking techniques
NextFirst autonomous agentic attack documented in Australia

Related Posts

Dramatic imagery but possible: ransomware as an unstoppable black hole

Dramatic imagery but possible: ransomware as an unstoppable black hole

Friday, November 12, 2021

AI agent executes end-to-end ransomware attack via development platform vulnerability: report

AI agent executes end-to-end ransomware attack via development platform vulnerability: report

Friday, July 3, 2026

Are traditional cyber IR plans applicable to cloud incidents as well?

Are traditional cyber IR plans applicable to cloud incidents as well?

Friday, September 29, 2023

Indonesian transport firm puts cybersecurity first as it pivots to digital

Indonesian transport firm puts cybersecurity first as it pivots to digital

Wednesday, March 23, 2022

Leave a reply Cancel reply

You must be logged in to post a comment.

Voters-draw/RCA-Sponsors

Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
previous arrow
next arrow

CybersecAsia Voting Placement

Gamification listing or Participate Now

LEARN MORE

Vote Now -Placement(Google Ads)

Top-Sidebar-banner

Whitepapers

  • Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Cyber threats have become more frequent and sophisticated, targeting organizations of all sizes across all …Download Whitepaper
  • Zero Trust Made Simple: Why it matters and how to get started

    Zero Trust Made Simple: Why it matters and how to get started

    Data breaches and cyberattacks are no longer limited to large, high-profile organizations.Download Whitepaper
  • Cloud Secure Edge: Remote access, better security

    Cloud Secure Edge: Remote access, better security

    ​SonicWall Cloud Secure Edge™ is a modern, cloud-native Security Service Edge (SSE) solution that addresses …Download Whitepaper
  • Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Insider threats continue to be a major cybersecurity risk in 2024. Explore more insights on …Download Whitepaper

Middle-sidebar-banner

Case Studies

  • How a Vietnamese D2C retailer built its own secure digital infrastructure

    How a Vietnamese D2C retailer built its own secure digital infrastructure

    Would your organization build your own digital infrastructure – including AI governance and cybersecurity – …Read more
  • Cyber protection for medical clinics in Singapore

    Cyber protection for medical clinics in Singapore

    As Singapore’s healthcare sector becomes increasingly digital and interconnected, clinics are facing heightened cyber risks, …Read more
  • India’s WazirX strengthens governance and digital asset security

    India’s WazirX strengthens governance and digital asset security

    Revamping its custody infrastructure using multi‑party computation tools has improved operational resilience and institutional‑grade safeguardsRead more
  • Bangladesh LGED modernizes communication while addressing data security concerns

    Bangladesh LGED modernizes communication while addressing data security concerns

    To meet emerging data localization/privacy regulations, the government engineering agency deploys a secure, unified digital …Read more

Bottom sidebar

Other News

  • From Defence Cooperation to Shared Security: Building a Resilient Pakistan-China Partnership

    Friday, October 9, 2026
    QINGDAO, China, Oct. 9, 2026 …Read More »
  • CyberDSA Sets 19 – 21 October 2027 Return as Industry Participation Builds at Fourth Edition

    Thursday, October 8, 2026
    CyberDSA moves towards its milestone …Read More »
  • CyberLogitec Brings Tag-Free Collision Prevention to Busan New Port

    Tuesday, October 6, 2026
    Digital twin places workers and …Read More »
  • Aligning with Global Regulations: iMQ Technology’s SQ713x Secure Element Achieves SESIP and PSA Certified Level 3

    Monday, October 5, 2026
    Passes Keysight’s physical attack testing …Read More »
  • Cymulate Receives Frost & Sullivan’s 2026 Indian Competitive Strategy Leadership Recognition for Advancing Continuous Security Validation

    Monday, October 5, 2026
    The recognition highlights Cymulate’s competitive …Read More »
  • Our Brands
  • DigiconAsia
  • MartechAsia
  • Home
  • About Us
  • Contact Us
  • Sitemap
  • Privacy & Cookies
  • Terms of Use
  • Advertising & Reprint Policy
  • Media Kit
  • Subscribe
  • Manage Subscriptions
  • Newsletter

Copyright © 2026 CybersecAsia All Rights Reserved.