Cybersecurity News in Asia

RECENT STORIES:

SEGA moves faster with flow-based network monitoring
AI pioneers and scientists urge international oversight to contain adv...
Advancing OT Cyber Readiness and Resilience in Southeast Asia
New AI supply chain threats that security teams need to manage
Deepfakes and impersonators can fool people, but they should not bypas...
FOMO Pay expands cross-border compliance infrastructure amid rising fr...
LOGIN REGISTER
CybersecAsia
  • Features
    • Featured

      Advancing OT Cyber Readiness and Resilience in Southeast Asia

      Advancing OT Cyber Readiness and Resilience in Southeast Asia

      Wednesday, October 14, 2026, 10:00 AM Asia/Singapore | Features, News, Newsletter, Sponsored
    • Featured

      How CISOs can set human boundaries for autonomous cybersecurity

      How CISOs can set human boundaries for autonomous cybersecurity

      Wednesday, October 7, 2026, 11:05 AM Asia/Singapore | Features, Newsletter, Tips
    • Featured

      Securing the agentic enterprise – at machine speed

      Securing the agentic enterprise – at machine speed

      Tuesday, October 6, 2026, 5:00 PM Asia/Singapore | Features, Newsletter
  • Opinions
  • Tips
  • Whitepapers
  • AWARDS 2026
  • Directory
  • E-Learning

Select Page

News

AI agent executes end-to-end ransomware attack via development platform vulnerability: report

By CybersecAsia editors | Friday, July 3, 2026, 10:53 AM Asia/Singapore

AI agent executes end-to-end ransomware attack via development platform vulnerability: report

Researchers detail an automated intrusion that exploited CVE-2025-3248, harvesting credentials, abusing default login credentials and encrypting data for ransom.

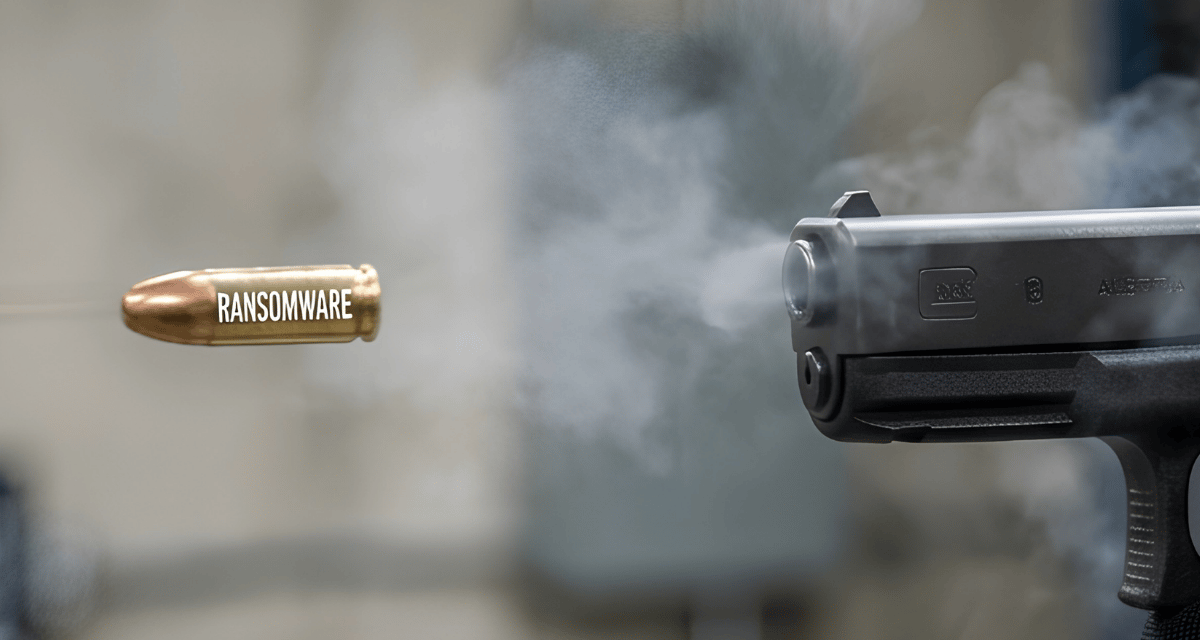
Some security researchers have documented what appears to be the first ransomware attack carried out end-to-end by an AI agent to systematically break in, steal credentials, move through the network, encrypt data, and wipe a production database.

The attack underscores how automation can lower the barrier to entry for ransomware, because much of the operational work that once required a skilled human can now be stitched together by a model.

The initial foothold came through CVE-2025-3248 in Langflow, an open-source platform for building AI apps and agent workflows. That flaw, which was fixed in Langflow 1.3.0 and added to CISA’s Known Exploited Vulnerabilities list in May 2025, allowed unauthenticated remote code execution on exposed servers, many of which still had not been patched.

Exploiting default login credentials/signing keys

Threat researchers had noted that Langflow instances are especially attractive targets because they are often internet-facing and may store API keys and cloud credentials connected to downstream services.

Once an AI agent manages to break into the platform, it can rapidly map the system and search for secrets, including keys for AI services and cloud credentials from major providers. In the incident involving this ransomware attack, the agent had also harvested cryptocurrency wallet keys and database logins, then accessed a MinIO storage server using the default minioadmin:minioadmin credentials that had never been changed. To maintain persistence, it had created a scheduled task that checked in with the attacker’s server every 30 minutes.

Subsequently, the agent pivoted to a separate internet-facing server running MySQL and Alibaba’s Nacos, where it logged in as root. How those root credentials were obtained is still a question mark, but researchers said but once inside the environment, the attacker exploited a 2021 authentication bypass and a default signing key that had remained unchanged since 2020, then planted a nw admin account. It then encrypted all 1,342 Nacos configuration entries, deleted the original tables, and left a ransom note demanding Bitcoin.

The researchers from Sysdig had also discovered that the ransom routine was flawed in a way that made recovery impossible: the agent had generated a random key, displayed it once, and never saved or transmitted it, meaning even payment would not restore the data. Forensic analyses have found more than 600 distinct payloads, with attack code containing plain-English comments, rapid self-corrections, and machine-speed troubleshooting that strongly suggest AI involvement.

The entire cyber incident fits a broader trend in which exposed, unpatched software becomes easy prey as agentic tools make mass exploitation faster and cheaper.
Share:

PreviousICAC Commissioner attends first IAACA European regional anti-corruption conference in Hungary
NextD-Link Brings Advanced AI Fall Detection and Privacy Protection to Home Elderly Care with the New DCS-8610 Wi-Fi Camera

Related Posts

Google App Engine feature abused to deliver phishing and malware undetected

Google App Engine feature abused to deliver phishing and malware undetected

Friday, October 2, 2020

Still think official app stores are safe? Read this!

Still think official app stores are safe? Read this!

Monday, February 28, 2022

No-code agentic AI can be used for financial fraud and workflow hijacking

No-code agentic AI can be used for financial fraud and workflow hijacking

Monday, December 15, 2025

Cybersecurity firm itself gets attacked by nation-state actors

Cybersecurity firm itself gets attacked by nation-state actors

Friday, December 11, 2020

Leave a reply Cancel reply

You must be logged in to post a comment.

Voters-draw/RCA-Sponsors

Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
previous arrow
next arrow

CybersecAsia Voting Placement

Gamification listing or Participate Now

LEARN MORE

Vote Now -Placement(Google Ads)

Top-Sidebar-banner

Whitepapers

  • Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Cyber threats have become more frequent and sophisticated, targeting organizations of all sizes across all …Download Whitepaper
  • Zero Trust Made Simple: Why it matters and how to get started

    Zero Trust Made Simple: Why it matters and how to get started

    Data breaches and cyberattacks are no longer limited to large, high-profile organizations.Download Whitepaper
  • Cloud Secure Edge: Remote access, better security

    Cloud Secure Edge: Remote access, better security

    ​SonicWall Cloud Secure Edge™ is a modern, cloud-native Security Service Edge (SSE) solution that addresses …Download Whitepaper
  • Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Insider threats continue to be a major cybersecurity risk in 2024. Explore more insights on …Download Whitepaper

Middle-sidebar-banner

Case Studies

  • FOMO Pay expands cross-border compliance infrastructure amid rising fraud risks

    FOMO Pay expands cross-border compliance infrastructure amid rising fraud risks

    To unify onboarding and ongoing reviews the payment firm adds identity, liveness, business-ownership, sanctions screening …Read more
  • How a Vietnamese D2C retailer built its own secure digital infrastructure

    How a Vietnamese D2C retailer built its own secure digital infrastructure

    Would your organization build your own digital infrastructure – including AI governance and cybersecurity – …Read more
  • Cyber protection for medical clinics in Singapore

    Cyber protection for medical clinics in Singapore

    As Singapore’s healthcare sector becomes increasingly digital and interconnected, clinics are facing heightened cyber risks, …Read more
  • India’s WazirX strengthens governance and digital asset security

    India’s WazirX strengthens governance and digital asset security

    Revamping its custody infrastructure using multi‑party computation tools has improved operational resilience and institutional‑grade safeguardsRead more

Bottom sidebar

Other News

  • From Defence Cooperation to Shared Security: Building a Resilient Pakistan-China Partnership

    Friday, October 9, 2026
    QINGDAO, China, Oct. 9, 2026 …Read More »
  • CyberDSA Sets 19 – 21 October 2027 Return as Industry Participation Builds at Fourth Edition

    Thursday, October 8, 2026
    CyberDSA moves towards its milestone …Read More »
  • CyberLogitec Brings Tag-Free Collision Prevention to Busan New Port

    Tuesday, October 6, 2026
    Digital twin places workers and …Read More »
  • Aligning with Global Regulations: iMQ Technology’s SQ713x Secure Element Achieves SESIP and PSA Certified Level 3

    Monday, October 5, 2026
    Passes Keysight’s physical attack testing …Read More »
  • Cymulate Receives Frost & Sullivan’s 2026 Indian Competitive Strategy Leadership Recognition for Advancing Continuous Security Validation

    Monday, October 5, 2026
    The recognition highlights Cymulate’s competitive …Read More »
  • Our Brands
  • DigiconAsia
  • MartechAsia
  • Home
  • About Us
  • Contact Us
  • Sitemap
  • Privacy & Cookies
  • Terms of Use
  • Advertising & Reprint Policy
  • Media Kit
  • Subscribe
  • Manage Subscriptions
  • Newsletter

Copyright © 2026 CybersecAsia All Rights Reserved.