Cybersecurity News in Asia

RECENT STORIES:

SEGA moves faster with flow-based network monitoring
AI pioneers and scientists urge international oversight to contain adv...
Advancing OT Cyber Readiness and Resilience in Southeast Asia
New AI supply chain threats that security teams need to manage
Deepfakes and impersonators can fool people, but they should not bypas...
FOMO Pay expands cross-border compliance infrastructure amid rising fr...
LOGIN REGISTER
CybersecAsia
  • Features
    • Featured

      Advancing OT Cyber Readiness and Resilience in Southeast Asia

      Advancing OT Cyber Readiness and Resilience in Southeast Asia

      Wednesday, October 14, 2026, 10:00 AM Asia/Singapore | Features, News, Newsletter, Sponsored
    • Featured

      How CISOs can set human boundaries for autonomous cybersecurity

      How CISOs can set human boundaries for autonomous cybersecurity

      Wednesday, October 7, 2026, 11:05 AM Asia/Singapore | Features, Newsletter, Tips
    • Featured

      Securing the agentic enterprise – at machine speed

      Securing the agentic enterprise – at machine speed

      Tuesday, October 6, 2026, 5:00 PM Asia/Singapore | Features, Newsletter
  • Opinions
  • Tips
  • Whitepapers
  • AWARDS 2026
  • Directory
  • E-Learning

Select Page

News

Scammers are now hooking low-hanging bait with crypto malvertising

By CybersecAsia editors | Sunday, May 11, 2025, 11:31 PM Asia/Singapore

Scammers are now hooking low-hanging bait with crypto malvertising

They are deploying fake crypto ads, using stealthy malware, and spoof crypto-celebrities to lure victims with promises of quick riches.

According to the threat researchers from a cybersecurity firm, a persistent malvertising campaign is plaguing Facebook, leveraging the reputations of well-known cryptocurrency exchanges to lure victims into a maze of malware.

The threat involves the deployment of cleverly disguised front-end scripts and custom payloads on users’ devices, all under the guise of legitimate cryptocurrency platforms and influencers.

The malvertising campaign has been operating for several months, consistently producing new advertisements. It heavily leverages the imagery and trust associated with cryptocurrency brands, and it remains active with fresh ads appearing regularly.

Tactics used
The initial malware is allegedly delivered via covert communication between a malicious website’s front end and local host, a method that evades detection by most security vendors. By orchestrating malware deployment through a seemingly harmless intermediary, attackers remain stealthy. Next:

  • Hundreds of ads impersonating trusted cryptocurrency exchanges and trading platforms have been put online, to drastically increase the odds that potential victims will view the malicious ads and be convinced to interact with the prompts. The cybercriminals use Meta’s ad network to tout quick financial gains and crypto bonuses, with some ads seeking to bolster credibility by featuring the image of public figures such as Elon Musk or Cristiano Ronaldo.
  • Advanced tracking and evasion: The threat actors use sophisticated anti-sandbox checks, only delivering malware to users who meet specific demographic or behavioral profiles. Query parameters related to Facebook Ads are used to detect legitimate victims, while suspicious or automated analysis environments receive benign content. Any user who views a malicious ad is redirected to a website that impersonates a known cryptocurrency platform, with subsequent prompts to download a “desktop client”. However, if the site detects suspicious conditions (for example, missing ad-tracking parameters or an environment typical of automated security analysis), it displays harmless, unrelated content instead. Also, no malicious content will be displayed for users who loaded the website without the specific query parameters of the Facebook ads: some examples being utm_campaign, utm_content, fbid, cid. If the user is not logged into Facebook, or if the IP address and operating system do not interest the attackers, the website will not display malicious content.
  • Newer variants take a step further, prompting users to open the site using Microsoft Edge; opening it with other browsers leads to random, non-malicious content, further complicating detection efforts. One particularly deceptive instance is a Facebook clone that mirrors TradingView’s official Facebook page. From the profile pictures to posts and comments touting a free ‘Annual Ultimate Subscription’, everything is fabricated, except for the central buttons that redirect victims to the real Facebook website.
  • Researchers have uncovered hundreds of Facebook accounts promoting these malware-delivering pages, all pushing financial benefits. In one notable example, a single page ran over 100 ads in a single day (9 April, 2025). While many ads are quickly removed, some garner thousands of views before takedown. Targeting is frequently fine-tuned, such as focusing on men aged 18+ in Bulgaria and Slovakia — to maximize reach.
  • All analyzed malware samples had the name installer.msi and measured around 800KB. After installation, the malicious software would open the page of the impersonated entity through msedge_proxy.exe. Victims also receive a suspicious DLL file that launches a local .NET-based server on ports 30308 or 30303 (in a newer version). By dynamically adjusting to the victim’s environment and continuously updating payloads, the threat actors maintain a resilient, highly evasive operation. Multiple layers of obfuscation, sandbox checks, and real-time payload evolution make this campaign a sophisticated challenge for researchers and security providers. 

The threat researchers, hailing from Bitdefender Labs, have citing facing and uncovering multiple techniques that had prevented end-to-end analysis of the threat — from the measures taken on the malicious websites (displaying non-malicious content based on traffic metadata), to anti-sandbox actions (for example, the looped PowerShell task would not download the final payload in dynamic analysis environments).

Despite the sophistication and innovation of the campaign, immunization involves compliance with the golden rules of basic cybersecurity hygiene.
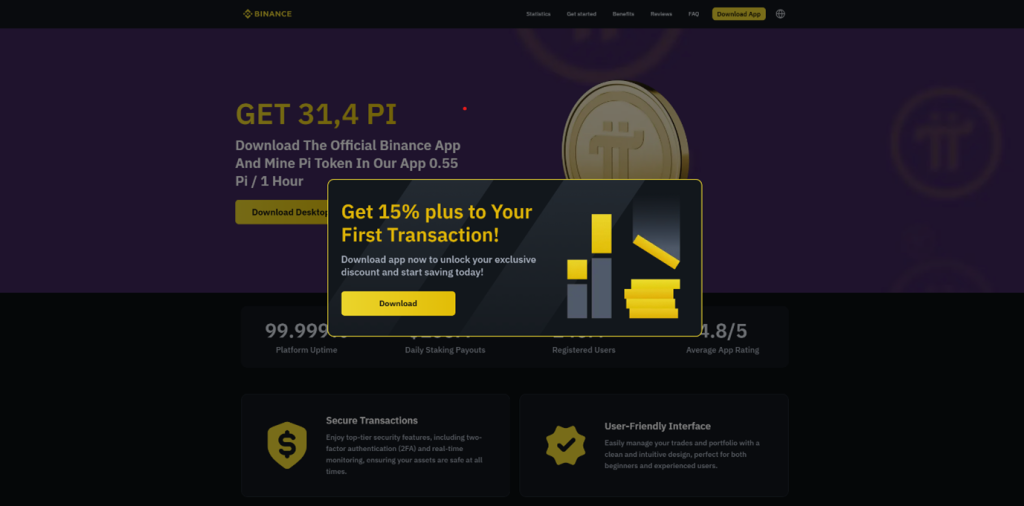
A typically alluring fake ad luring people to download sophisticated multi-stage malware
Share:

PreviousBeware the friendly widget bearing perks and convenience
NextDo not let hackers halt your plant: Checklists for reviewing OT cyber resilience

Related Posts

2019: A year of frantic ransomware evolution

2019: A year of frantic ransomware evolution

Thursday, May 28, 2020

Protected Health Information are a hot commodity on the Dark Web

Protected Health Information are a hot commodity on the Dark Web

Friday, February 5, 2021

5 easy tips to become super safe online

5 easy tips to become super safe online

Wednesday, March 18, 2020

Waves of new ransomware surface after 2022 LockBit codebase leak

Waves of new ransomware surface after 2022 LockBit codebase leak

Wednesday, October 25, 2023

Leave a reply Cancel reply

You must be logged in to post a comment.

Voters-draw/RCA-Sponsors

Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
previous arrow
next arrow

CybersecAsia Voting Placement

Gamification listing or Participate Now

LEARN MORE

Vote Now -Placement(Google Ads)

Top-Sidebar-banner

Whitepapers

  • Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Cyber threats have become more frequent and sophisticated, targeting organizations of all sizes across all …Download Whitepaper
  • Zero Trust Made Simple: Why it matters and how to get started

    Zero Trust Made Simple: Why it matters and how to get started

    Data breaches and cyberattacks are no longer limited to large, high-profile organizations.Download Whitepaper
  • Cloud Secure Edge: Remote access, better security

    Cloud Secure Edge: Remote access, better security

    ​SonicWall Cloud Secure Edge™ is a modern, cloud-native Security Service Edge (SSE) solution that addresses …Download Whitepaper
  • Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Insider threats continue to be a major cybersecurity risk in 2024. Explore more insights on …Download Whitepaper

Middle-sidebar-banner

Case Studies

  • FOMO Pay expands cross-border compliance infrastructure amid rising fraud risks

    FOMO Pay expands cross-border compliance infrastructure amid rising fraud risks

    To unify onboarding and ongoing reviews the payment firm adds identity, liveness, business-ownership, sanctions screening …Read more
  • How a Vietnamese D2C retailer built its own secure digital infrastructure

    How a Vietnamese D2C retailer built its own secure digital infrastructure

    Would your organization build your own digital infrastructure – including AI governance and cybersecurity – …Read more
  • Cyber protection for medical clinics in Singapore

    Cyber protection for medical clinics in Singapore

    As Singapore’s healthcare sector becomes increasingly digital and interconnected, clinics are facing heightened cyber risks, …Read more
  • India’s WazirX strengthens governance and digital asset security

    India’s WazirX strengthens governance and digital asset security

    Revamping its custody infrastructure using multi‑party computation tools has improved operational resilience and institutional‑grade safeguardsRead more

Bottom sidebar

Other News

  • From Defence Cooperation to Shared Security: Building a Resilient Pakistan-China Partnership

    Friday, October 9, 2026
    QINGDAO, China, Oct. 9, 2026 …Read More »
  • CyberDSA Sets 19 – 21 October 2027 Return as Industry Participation Builds at Fourth Edition

    Thursday, October 8, 2026
    CyberDSA moves towards its milestone …Read More »
  • CyberLogitec Brings Tag-Free Collision Prevention to Busan New Port

    Tuesday, October 6, 2026
    Digital twin places workers and …Read More »
  • Aligning with Global Regulations: iMQ Technology’s SQ713x Secure Element Achieves SESIP and PSA Certified Level 3

    Monday, October 5, 2026
    Passes Keysight’s physical attack testing …Read More »
  • Cymulate Receives Frost & Sullivan’s 2026 Indian Competitive Strategy Leadership Recognition for Advancing Continuous Security Validation

    Monday, October 5, 2026
    The recognition highlights Cymulate’s competitive …Read More »
  • Our Brands
  • DigiconAsia
  • MartechAsia
  • Home
  • About Us
  • Contact Us
  • Sitemap
  • Privacy & Cookies
  • Terms of Use
  • Advertising & Reprint Policy
  • Media Kit
  • Subscribe
  • Manage Subscriptions
  • Newsletter

Copyright © 2026 CybersecAsia All Rights Reserved.