
Cybersecurity News in Asia

LOGIN REGISTER
CybersecAsia
  • Features
    • Featured

      Will your AI agents always do only what you want them to?

      Will your AI agents always do only what you want them to?

      Thursday, November 19, 2026, 10:09 AM Asia/Singapore | Features
    • Featured

      Curbing S E Asia’s tsunami of gaming scams and payment fraud

      Curbing S E Asia’s tsunami of gaming scams and payment fraud

      Wednesday, November 18, 2026, 12:24 PM Asia/Singapore | Features, Newsletter
    • Featured

      From VPNs to zero-trust access

      From VPNs to zero-trust access

      Tuesday, November 17, 2026, 1:00 PM Asia/Singapore | Features, Newsletter, Sponsored
  • Opinions
  • Tips
  • Whitepapers
  • AWARDS 2026
  • Directory
  • E-Learning

Select Page

NewsTips

Foxconn breach highlights non-human identity crisis

By CybersecAsia editors | Thursday, May 14, 2026, 2:47 PM Asia/Singapore

Foxconn breach highlights non-human identity crisis

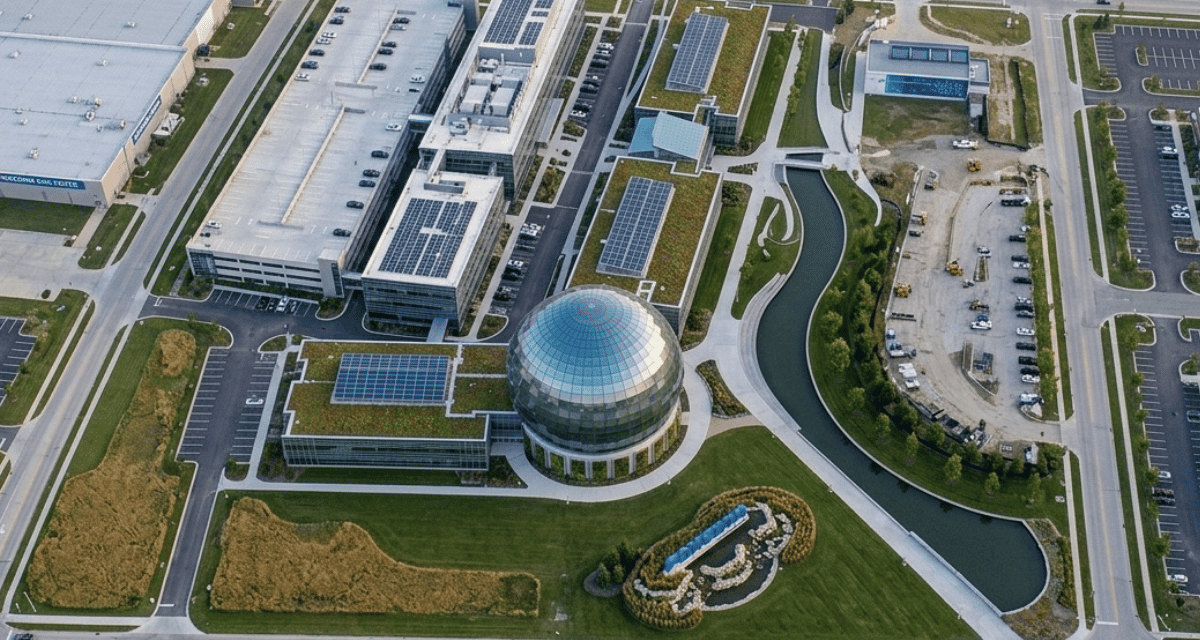
Recent Foxconn breach brings into focus the highly interconnected nature of global manufacturing supply chains, with an explosive growth in non-human identities.

The semiconductor industry is gearing up in APAC, with major operations in Taiwan, China, South Korea, Japan, Singapore, Vietnam, and Malaysia. It is also an increasingly high-stakes industry due to geopolitics and industry demand.

It has recently been widely reported that the Nitrogen ransomware group crippled Foxconn’s North American manufacturing facilities and forced a multi-day production standstill that required staff to resort to manual operations. 

The attackers claim to have exfiltrated 8TB of sensitive data encompassing 11 million files, including confidential technical blueprints and schematics belonging to major partners like Google and Intel.

Takanori Nishiyama, Senior Vice President APAC, Keeper Security, commented: “The reported exfiltration of 8TB of data from Foxconn highlights the highly interconnected nature of the global manufacturing supply chain. When 11 million files, including technical blueprints and engineering schematics, are alleged to have been compromised, the competitive advantage and reputations of these organizations are placed at substantial risk.”

Multiple targets in manufacturing

Nishiyama explained “Modern manufacturing is no longer just about physical assembly; it is a complex digital ecosystem where a single point of failure can halt production across multiple continents.”

He pointed out that ransomware groups frequently target victims that provide a path into other organizations. “By compromising a primary supplier, attackers gain a vantage point into the sensitive schematics and project data of the entire tech sector.”

Relying on perimeter defenses is no longer sufficient in this threat landscape. Identity-related solutions such as Privileged Access Management (PAM) have become a foundational requirement for supply chain resilience. 

Modern PAM platforms mitigate the risks associated with third-party vendors, standing access and overprivileged accounts that can provide attackers with unfettered access to an organization. PAM reduces the attacker’s window of opportunity by enabling Just-In-Time (JIT) access, which ensures privileges are granted only when necessary and revoked immediately after a task is completed.

AI and automation

The expansion of AI and automation in smart factories has also led to an explosion of Non-Human Identities (NHIs), such as service accounts and API keys. 

“These identities often hold persistent, high-level privileges that blend into normal system activity, making them prime targets for lateral movement,” Nishiyama warned.

Keeper’s 20026 Global Insight Report found that 89% of IT and security leaders cite managing the growing number of human and non-human identities as a primary challenge. 

“In an environment of Foxconn’s complexity, that challenge is acute, said Nishiyama. “Every remote contractor, service account and automated process represents a potential access point.”

What must be in place

Nishiyama emphasized that, without a unified zero-trust architecture to govern these identities, the entire supply chain remains vulnerable to lateral movement and data theft.

“The operational lesson is consistent regardless of how this incident unfolded,” he concluded. “Where IT infrastructure, operational technology and third-party supplier access intersect, the identity layer is the last reliable line of defense for high-value data.” 

He added: “Privileged access must be time limited, verified and fully auditable at every layer, across human and service accounts, third-party access and the automated processes that increasingly sit at the heart of modern manufacturing.”
Share:

PreviousUS$72 billion leakage at checkout
NextAI-generated zero day raises agentic cyber abuse concerns

Related Posts

Not one but three frontier AI firms saw models escape test sandboxes, commit breaches

Not one but three frontier AI firms saw models escape test sandboxes, commit breaches

Tuesday, August 11, 2026

Hackers drain reserves of a Bitcoin sidechain, forcing a shutdown

Hackers drain reserves of a Bitcoin sidechain, forcing a shutdown

Tuesday, September 8, 2026

SingAREN showcases what a national research community needs for cyber protection

SingAREN showcases what a national research community needs for cyber protection

Wednesday, February 7, 2024

Making secrets management frictionless in DevOps can boost cybersecurity

Making secrets management frictionless in DevOps can boost cybersecurity

Thursday, November 18, 2021

Leave a reply Cancel reply

You must be logged in to post a comment.

Voters-draw/RCA-Sponsors

Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
previous arrow
next arrow

CybersecAsia Voting Placement

Gamification listing or Participate Now

LEARN MORE

Vote Now -Placement(Google Ads)

Top-Sidebar-banner

Whitepapers

  • Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Cyber threats have become more frequent and sophisticated, targeting organizations of all sizes across all …Download Whitepaper
  • Zero Trust Made Simple: Why it matters and how to get started

    Zero Trust Made Simple: Why it matters and how to get started

    Data breaches and cyberattacks are no longer limited to large, high-profile organizations.Download Whitepaper
  • Cloud Secure Edge: Remote access, better security

    Cloud Secure Edge: Remote access, better security

    ​SonicWall Cloud Secure Edge™ is a modern, cloud-native Security Service Edge (SSE) solution that addresses …Download Whitepaper
  • Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Insider threats continue to be a major cybersecurity risk in 2024. Explore more insights on …Download Whitepaper

Middle-sidebar-banner

Case Studies

  • FOMO Pay expands cross-border compliance infrastructure amid rising fraud risks

    FOMO Pay expands cross-border compliance infrastructure amid rising fraud risks

    To unify onboarding and ongoing reviews the payment firm adds identity, liveness, business-ownership, sanctions screening …Read more
  • How a Vietnamese D2C retailer built its own secure digital infrastructure

    How a Vietnamese D2C retailer built its own secure digital infrastructure

    Would your organization build your own digital infrastructure – including AI governance and cybersecurity – …Read more
  • Cyber protection for medical clinics in Singapore

    Cyber protection for medical clinics in Singapore

    As Singapore’s healthcare sector becomes increasingly digital and interconnected, clinics are facing heightened cyber risks, …Read more
  • India’s WazirX strengthens governance and digital asset security

    India’s WazirX strengthens governance and digital asset security

    Revamping its custody infrastructure using multi‑party computation tools has improved operational resilience and institutional‑grade safeguardsRead more

Bottom sidebar

Other News

  • GovWare 2026 closes with a clear focus on securing AI that can act

    Thursday, November 19, 2026
    Across the conference and exhibition, …Read More »
  • Visa Launches Threat Intelligence Platform to Strengthen Cyber and Fraud Defense

    Wednesday, November 18, 2026
    New research commissioned by Visa …Read More »
  • As Hijacked Billboards Make Headlines, CAYIN SMP Players Keep Screens in Owners’ Hands

    Monday, November 16, 2026
    After a run of hijacked …Read More »
  • Cohesity Expands Cyber Resilience and AI Data Capabilities for Microsoft Environments

    Friday, November 13, 2026
    Recent innovations strengthen data security …Read More »
  • Cequence Security and KPMG Collaborate on Joint Report Examining how Organisations can Govern and Secure Agentic AI

    Wednesday, November 11, 2026
    New Cequence data in the …Read More »
  • Our Brands
  • DigiconAsia
  • MartechAsia
  • Home
  • About Us
  • Contact Us
  • Sitemap
  • Privacy & Cookies
  • Terms of Use
  • Advertising & Reprint Policy
  • Media Kit
  • Subscribe
  • Manage Subscriptions
  • Newsletter

Copyright © 2026 CybersecAsia All Rights Reserved.