Cybersecurity News in Asia

RECENT STORIES:

SEGA moves faster with flow-based network monitoring
IQuest Research Releases IQuest-Q1 Technical Report, Detailing Trainin...
The future of enterprise storage will be built on data trust
Russian intelligence-linked hackers infiltrate organisations across tw...
Leaked exploit details preceded emergency PHP2Shell patches
New GASA Research: 71% of Adults Surveyed Across 13 Asian Markets Enco...
LOGIN REGISTER
CybersecAsia
  • Features
    • Featured

      Communications infrastructure – from legacy risk to modern resilience

      Communications infrastructure – from legacy risk to modern resilience

      Thursday, October 15, 2026, 2:08 PM Asia/Singapore | Features
    • Featured

      Advancing OT Cyber Readiness and Resilience in Southeast Asia

      Advancing OT Cyber Readiness and Resilience in Southeast Asia

      Wednesday, October 14, 2026, 10:00 AM Asia/Singapore | Features, News, Sponsored
    • Featured

      How CISOs can set human boundaries for autonomous cybersecurity

      How CISOs can set human boundaries for autonomous cybersecurity

      Wednesday, October 7, 2026, 11:05 AM Asia/Singapore | Features, Newsletter, Tips
  • Opinions
  • Tips
  • Whitepapers
  • AWARDS 2026
  • Directory
  • E-Learning

Select Page

Features

Weaponization of GenAI by adversaries

By Victor Ng | Wednesday, November 5, 2025, 10:15 AM Asia/Singapore

Weaponization of GenAI by adversaries

Threat actors are no longer just experimenting with GenAI — they’re operationalizing it at scale. How should cyber-defenders respond?

In the past year alone, AI-enabled adversary FAMOUS CHOLLIMA infiltrated over 320 organizations globally — a 220% year-on-year increase — by leveraging GenAI at every stage of the hiring and employment process.

GenAI was used by the North Korean state-sponsored bad actor, from generating persuasive resumes and using real-time deepfakes in interviews, to deploying AI-assisted coding tools once hired.

As GenAI tools become more accessible and intuitive, CrowdStrike has assessed that its use for social engineering and targeted attacks will surge in the near to mid-term. This presents an urgent challenge for organizations to evolve their defenses.

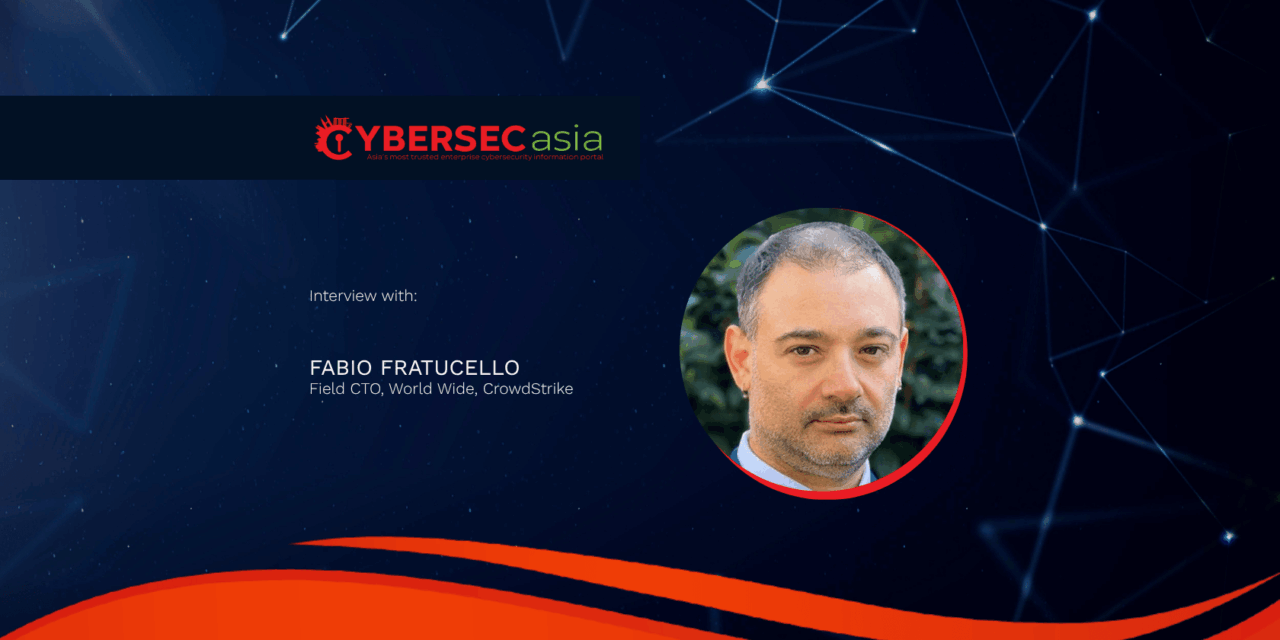
CybersecAsia.net gathered more insights from Fabio Fratucello, Field CTO, World Wide, CrowdStrike:

How are threat actors weaponizing GenAI to augment and enhance their attacks?

Fratucello: The CrowdStrike 2025 Threat Hunting Report shows a significant shift in modern cyberattacks as adversaries increasingly weaponize GenAI to scale their operations and accelerate their attacks. Adversaries such as FAMOUS CHOLLIMA are integrating GenAI throughout their sophisticated insider operations, from building fake resumes, to conducting deepfake interviews, and even automating their coding tasks across multiple roles.

CrowdStrike tracked more than 320 cases of FAMOUS CHOLLIMA operatives working as remote IT workers over the past year – a 220% year-on-year increase – highlighting the pervasive threat of GenAI-driven adversary operations.

Besides attacks, in what other ways are cybercriminals leveraging AI?

Fratucello: Adversaries are increasingly targeting the AI agents and systems that transform organization’s operations.

As outlined in the 2025 Threat Hunting Report, CrowdStrike has observed multiple threat actors exploiting vulnerabilities in tools used to build AI agents, gaining unauthenticated access, establishing persistence, harvesting credentials, and deploying malware and ransomware.

These attacks demonstrate how the enterprise attack surface is expanding with agentic AI adoption, with autonomous workflows and non-human identities the next frontier of adversary exploitation.

How should cyber-defenders respond to attackers sharpening their edge and speed with AI-generated code?

Fratucello: Organizations need to leverage AI to enhance their defenses and counter adversaries’ weaponization of AI. A modern security platform built with AI capabilities from the ground up provides organizations with the foundation they need to power a truly agentic Security Operations Centre (SOC).

They must secure their AI deployments through proactive monitoring of integrations, protection against model tampering, and detecting misconfigurations. For instance, they can leverage tools such as CrowdStrike’s AI Security Posture Management (AI-SPM), which provides comprehensive visibility and protection for AI models by detecting misconfigurations and identifying vulnerabilities.

Solutions like CrowdStrike Falcon Shield secure AI agents across the SaaS stack, by providing agent visibility, mapping agents to human creators, detecting risky behavior, and enabling automatic threat containment.

Falcon Data Protection provides real-time, unified security for how data moves in the AI era, by expanding coverage of runtime protection for local applications and cloud environments to prevent inadvertent exposure and block data leakage across managed and unmanaged GenAI tools. This provides organizations with comprehensive visibility and protection across endpoints, cloud, GenAI, and SaaS applications, and empowers them to securely innovate with AI, while Charlotte AI AgentWorks offers organizations a no-code platform that enables any security team to build, test, and deploy their own agents directly within the Falcon platform — while maintaining enterprise-grade security and governance.

Together, these agentic innovations sharpen defenders’ response by delivering machine-speed capabilities to automate repetitive tasks, accelerate outcomes, and empower analysts to focus on the strategic decisions that strengthen their security. 

What can organizations do today to strengthen their resilience and futureproof themselves against AI-powered threats?

Fratucello: Adversaries’ weaponization of AI is compressing the attack timeline, turning operations that once took months into seconds and collapsing the defender’s window of response. This means organizations’ threat intelligence capability must evolve beyond simply informing defenders to actively countering threats at the speed of AI.

AI can rapidly accelerate defenders’ investigation and threat responses, by eliminating high-friction tasks better suited to machines, while ensuring they remain firmly in command.

For example, CrowdStrike’s Threat AI is an agentic threat intelligence system that automates the most complex, time-consuming intelligence workflows to accelerate security outcomes – informed by years of real-world decisions from CrowdStrike Counter Adversary Operations’ elite threat hunters and intelligence experts – to deliver mission-ready agents for every security analyst that can reason across threat data, proactively hunt adversaries, and take decisive action across the kill chain.
Share:

PreviousDXC Opens First Client Experience Centre in the Philippines, Expanding Its Presence in Asia to Drive Collaboration and AI Innovation
NextTackling the risks of AI innovations in the cloud

Related Posts

Insider risks – when AI agents go rogue

Insider risks – when AI agents go rogue

Monday, August 17, 2026

Some threat actor innovations to watch out for

Some threat actor innovations to watch out for

Tuesday, February 6, 2024

Weed out hard-coded secrets before hackers violate your data!

Weed out hard-coded secrets before hackers violate your data!

Monday, February 6, 2023

We buckle seatbelts instinctively: why not authentication standards?

We buckle seatbelts instinctively: why not authentication standards?

Thursday, April 23, 2026

Leave a reply Cancel reply

You must be logged in to post a comment.

Voters-draw/RCA-Sponsors

Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
previous arrow
next arrow

CybersecAsia Voting Placement

Gamification listing or Participate Now

LEARN MORE

Vote Now -Placement(Google Ads)

Top-Sidebar-banner

Whitepapers

  • Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Cyber threats have become more frequent and sophisticated, targeting organizations of all sizes across all …Download Whitepaper
  • Zero Trust Made Simple: Why it matters and how to get started

    Zero Trust Made Simple: Why it matters and how to get started

    Data breaches and cyberattacks are no longer limited to large, high-profile organizations.Download Whitepaper
  • Cloud Secure Edge: Remote access, better security

    Cloud Secure Edge: Remote access, better security

    ​SonicWall Cloud Secure Edge™ is a modern, cloud-native Security Service Edge (SSE) solution that addresses …Download Whitepaper
  • Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Insider threats continue to be a major cybersecurity risk in 2024. Explore more insights on …Download Whitepaper

Middle-sidebar-banner

Case Studies

  • FOMO Pay expands cross-border compliance infrastructure amid rising fraud risks

    FOMO Pay expands cross-border compliance infrastructure amid rising fraud risks

    To unify onboarding and ongoing reviews the payment firm adds identity, liveness, business-ownership, sanctions screening …Read more
  • How a Vietnamese D2C retailer built its own secure digital infrastructure

    How a Vietnamese D2C retailer built its own secure digital infrastructure

    Would your organization build your own digital infrastructure – including AI governance and cybersecurity – …Read more
  • Cyber protection for medical clinics in Singapore

    Cyber protection for medical clinics in Singapore

    As Singapore’s healthcare sector becomes increasingly digital and interconnected, clinics are facing heightened cyber risks, …Read more
  • India’s WazirX strengthens governance and digital asset security

    India’s WazirX strengthens governance and digital asset security

    Revamping its custody infrastructure using multi‑party computation tools has improved operational resilience and institutional‑grade safeguardsRead more

Bottom sidebar

Other News

  • IQuest Research Releases IQuest-Q1 Technical Report, Detailing Training from Scratch and Results Across 30 Benchmarks

    Friday, October 23, 2026
    BEIJING, Oct. 23, 2026 /PRNewswire/ …Read More »
  • New GASA Research: 71% of Adults Surveyed Across 13 Asian Markets Encountered Scams, with Estimated Losses of US$136.5 Billion

    Thursday, October 22, 2026
    Research highlights a gap between …Read More »
  • NEXCOM NGFW platforms secure growing traffic across modern academic networks

    Thursday, October 22, 2026
    TAIPEI, Oct. 22, 2026 /PRNewswire/ …Read More »
  • Blackpanda and CyberCube Collaborate to Bring Cyber Risk Analytics to Brokers Across Asia

    Wednesday, October 21, 2026
    Blackpanda will refer brokers to …Read More »
  • Cohesity Announces FY2026 Partner Award Winners

    Wednesday, October 21, 2026
    Recognition highlights top performers across …Read More »
  • Our Brands
  • DigiconAsia
  • MartechAsia
  • Home
  • About Us
  • Contact Us
  • Sitemap
  • Privacy & Cookies
  • Terms of Use
  • Advertising & Reprint Policy
  • Media Kit
  • Subscribe
  • Manage Subscriptions
  • Newsletter

Copyright © 2026 CybersecAsia All Rights Reserved.