
As Asia Pacific races ahead with digitalization, the region is rapidly becoming a “breeding ground” for cybercriminals armed with AI and primed for ransomware campaigns.
That’s the central message from Debasish Mukherjee, Vice President, APJ, SonicWall, in an exclusive interview on evolving threats, ransomware, and the role of managed security for SMBs.
“Our region is moving into a digital economy… when a lot of digitization happens, it’s a breeding ground or it’s an easy option for cybercriminals because that’s the hub spot. That’s their interest.”
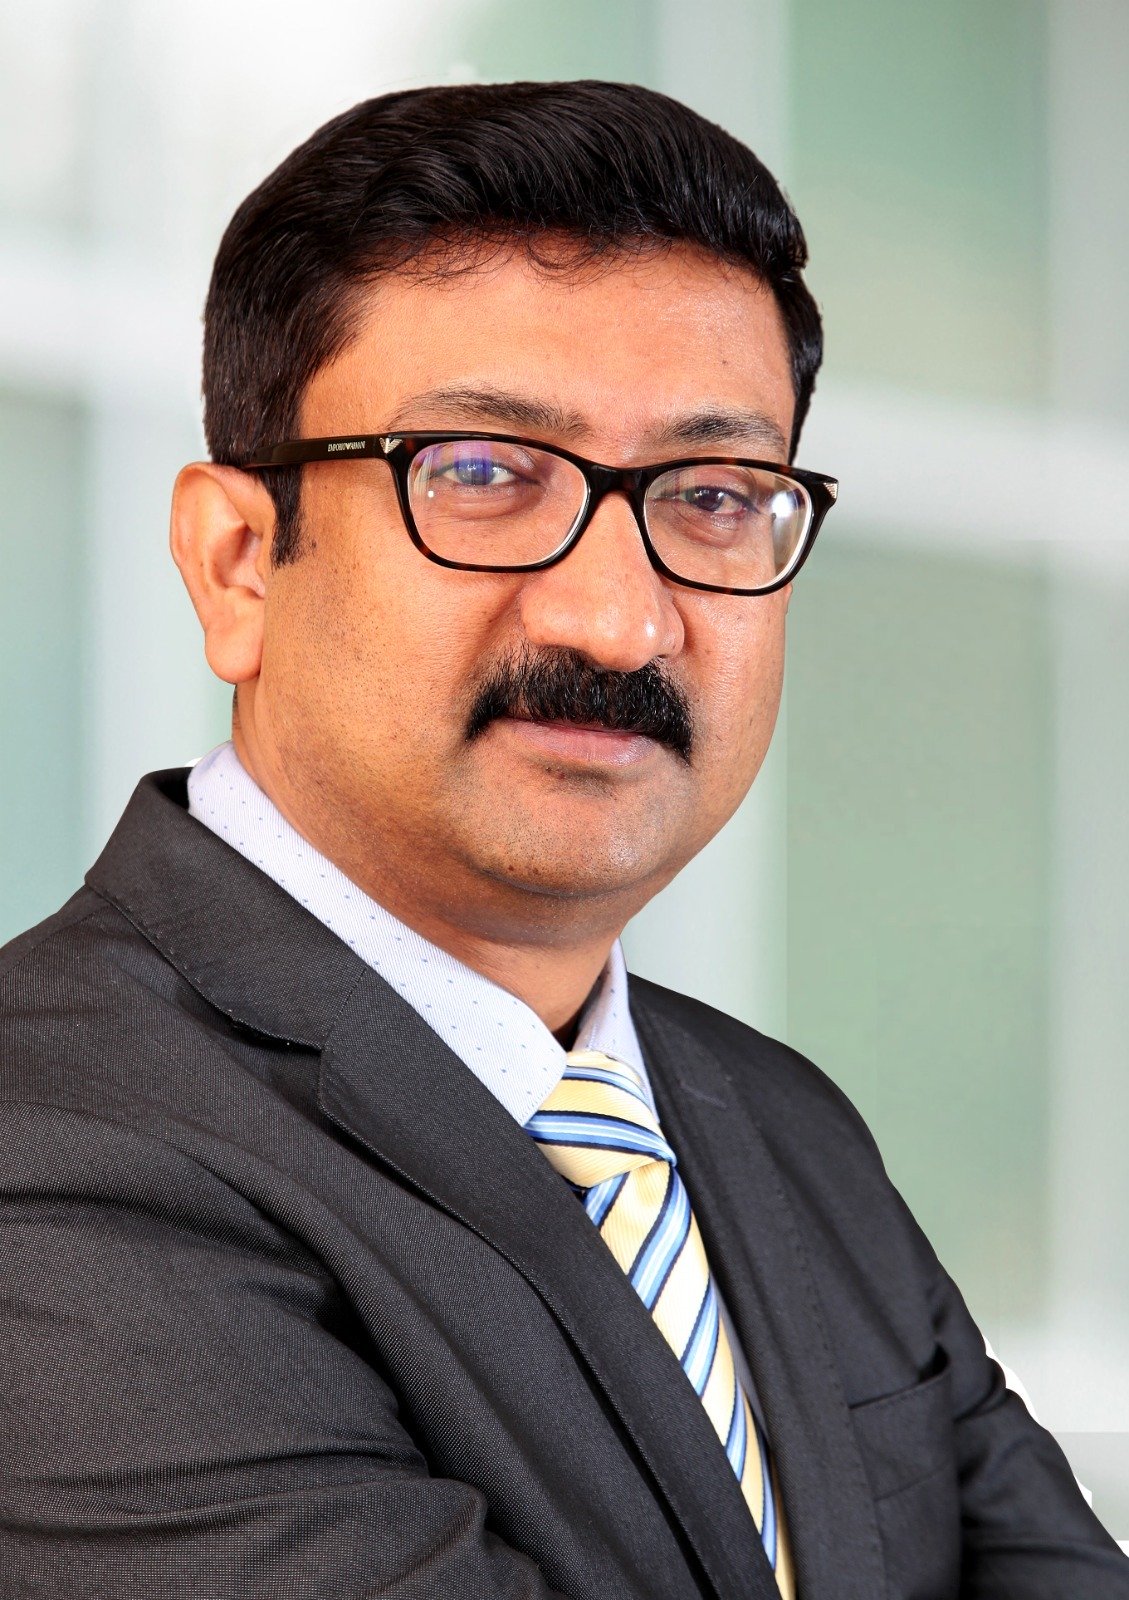
Debasish Mukherjee, Vice President, APJ, SonicWall
AI a hype magnet – and cyberthreat amplifier
Debasish is candid about the AI hype cycle—both in marketing and in security.
On the overuse of “AI”, he commented: “Anything which is in trend, people would like to use that so that we get more eyeballs. Today, AI is more of a marketing term.”
On AI being essential in cybersecurity, Debasish said: “We have to use AI in cybersecurity or else we cannot sustain. And we are using AI for more than 10 years.”
He likens the current AI wave to the early days of the cloud. “If you recall, maybe 15 years back, it was a similar story with cloud. Everyone wanted to hear ‘cloud’, but the adoption is still going on 15 years later. Today, AI is in the same position.”
At the same time, he warns that AI is also amplifying attackers’ capabilities: “With AI-assisted attacks, bad actors do not have to put a lot of effort to create a ransomware attack. Previously, creating an attack took maybe 24 to 36 hours. Today, an attack can be created in seconds using AI tools.”
What drives APAC’s expanding attack surface
According to Debasish, the Asia Pacific and Japan (APJ) region is experiencing a sharp increase in “actionable attacks”, driven by:
- Rapid digitization (India, Vietnam, Indonesia, etc.)
- Widespread hybrid work
- Accelerating IoT and SaaS/cloud adoption
- A historic lag behind developed markets in security maturity
SonicWall’s own research shows an ~20% increase in actionable attacks globally, with APJ heavily represented. The two dominant vectors are:
1. Identity-based attacks
“Identity is the new perimeter,” said Debasish. “Legacy perimeter security no longer protects everything.” Stolen credentials, weak identities, and identity fraud are driving breaches.
To counter this, SonicWall has embedded a credential auditor into its OS. The tool will tell a user, for example, when he or she is inputting a password that this ID or this password is already compromised, and it will keep telling the user till the best credential protection is reached.
2. Legacy vulnerabilities and unpatched systems
Users still running legacy VPNs and expired firewalls are leaving open doors as entry points for cybercriminals.
Debasish noted that price-sensitive markets in APJ often keep obsolete gear “because it still works,” without realizing the exposure. Meanwhile, long-running issues like Log4j remain: “Log4j is still a very popular attack surface… using breached information and finding out that patch management is not done.”
Add to this the distributed enterprise — remote work, SaaS, cloud workloads, OT and IoT — and the traditional perimeter effectively disappears: “Because now there is no perimeter and we have also started using a lot of IoT devices everywhere, all these are creating a problem.”
Ransomware’s favorite targets
Debasish is clear about the ultimate objective of most modern attacks: “Any attack which is happening is primarily now coming as ransomware… they are looking for money.”
SonicWall’s data indicates that around 88% of SMB breaches are ransomware-related, with three sectors standing out:
-
Healthcare
“They cannot afford a downtime; even a few minutes can mean people will die,” Debasish said bluntly.
Attackers understand that life-and-death operations and heavy reliance on connected equipment make hospitals highly likely to pay. SonicWall has observed 13 million remote exploitation attempts in healthcare alone.
-
Financial services
“Where there is money… there is value.” And reputation risk makes financial services a prime ransomware target.
Debasish added: “If a bank gets breached, its customers will go to another bank… so there is a high chance these organizations will pay.”
-
Manufacturing
Manufacturing’s transition from OT-heavy legacy environments to IT/OT convergence is creating a gap. Attackers exploit OT as an easier entry point to get into IT.
Any prolonged downtime directly impacts revenue: “Any manufacturing unit, if it is down for five–six hours, will lose a lot of money, and out of panic they will pay the ransom.”
Despite the focus on big-name breaches, Debasish argued that SMBs are actually more vulnerable than large enterprises: “SMBs are actually the more vulnerable. The reason is because they are easy preys for cybercriminals.”
Key reasons include limited budgets for advanced security tools, lack of in-house skills and 24×7 monitoring, and fragmented, non-integrated point products.
Yet, with AI now radically lowering the effort to launch attacks, attackers don’t need to choose between big and small: “Cybercriminals are not putting their effort in creating energy or intelligence… they are targeting everywhere. Whomsoever falls prey, it’s fine.”
Channel- and SMB-focused
Mukherjee positions SonicWall squarely as a channel- and SMB-focused cybersecurity vendor, particularly for the mid-market (roughly 2,000–2,500 users in their definition).
A key industry shift he has observed is moving away from product-centric thinking to outcome-centric security:
“Buying a product cannot solve your security problems… Buying multiple point products also cannot. What is the outcome? The outcome is you need to get protected from any attack.”
This is driving SMBs toward managed services:
- Customers care less who owns the tools and more about whether they are protected.
- Data and workloads are already in the cloud; ownership without security is meaningless.
To serve this shift, SonicWall has built a unified security platform intended both for direct customers and managed service providers (MSPs).
While North America and Europe are ahead in managed services adoption, APJ is catching up, with India, Singapore, Australia, Japan – including the government sector – now exploring MSP-led models.
Paired with a channel-first, SMB-focused strategy and a unified security platform for MSPs, SonicWall is positioning itself as a bridge between enterprise-grade security and mid-market affordability — in a region where digital growth and cyber risk are rising in tandem.
Debasish closed by emphasizing that, for SonicWall, AI is not a bolt-on buzzword but a decade-long evolution embedded in its OS, analytics, and threat hunting: “Our operating system and our Real-Time Deep Memory Inspection threat hunting capability, which is AI-enabled, has been around for the last 10 years.”