Cybersecurity News in Asia

RECENT STORIES:

SEGA moves faster with flow-based network monitoring
Securing the agentic enterprise – at machine speed
AI drives surge in software vulnerability disclosures in 2026: analysi...
CyberLogitec Brings Tag-Free Collision Prevention to Busan New Port
Operation KillSwitch seizes threat group infrastructure after investig...
Aligning with Global Regulations: iMQ Technology’s SQ713x Secure...
LOGIN REGISTER
CybersecAsia
  • Features
    • Featured

      Securing the agentic enterprise – at machine speed

      Securing the agentic enterprise – at machine speed

      Tuesday, October 6, 2026, 5:00 PM Asia/Singapore | Features, Newsletter
    • Featured

      Why Businesses Need to Treat AI Agents Like Privileged Insiders

      Why Businesses Need to Treat AI Agents Like Privileged Insiders

      Thursday, October 1, 2026, 10:00 AM Asia/Singapore | Expert Opinion, Features, Sponsored
    • Featured

      Shadow AI Is the New Insider Threat

      Shadow AI Is the New Insider Threat

      Monday, September 21, 2026, 9:11 AM Asia/Singapore | Features, Newsletter, Sponsored, Tips
  • Opinions
  • Tips
  • Whitepapers
  • AWARDS 2026
  • Directory
  • E-Learning

Select Page

Opinions

Are the built-in restrictions in Claude Fable 5 sufficient?

By Victor Ng | Friday, June 12, 2026, 8:52 AM Asia/Singapore

Are the built-in restrictions in Claude Fable 5 sufficient?

What does Mythos-class AI in public hands mean for security teams in Asia Pacific? Are the built-in guardrails enough? 

Anthropic’s Claude Fable 5 has landed in APAC, where security and IT teams are already operating under sustained, high-volume attack. Regulators in the region continue to raise expectations on operational resilience, patching cadence and incident response. 

Claude Fable 5 is Anthropic’s highly capable Mythos-class public AI model. To balance its powerful, long-running agent capabilities with security, Anthropic has built in automatic safeguards, so that if a prompt triggers restrictions in high-risk categories, the system dynamically reroutes the request to Claude Opus 4.8 to deliver a safe response.

But is this safety guardrail enough for our overstretched DevSecOps teams?

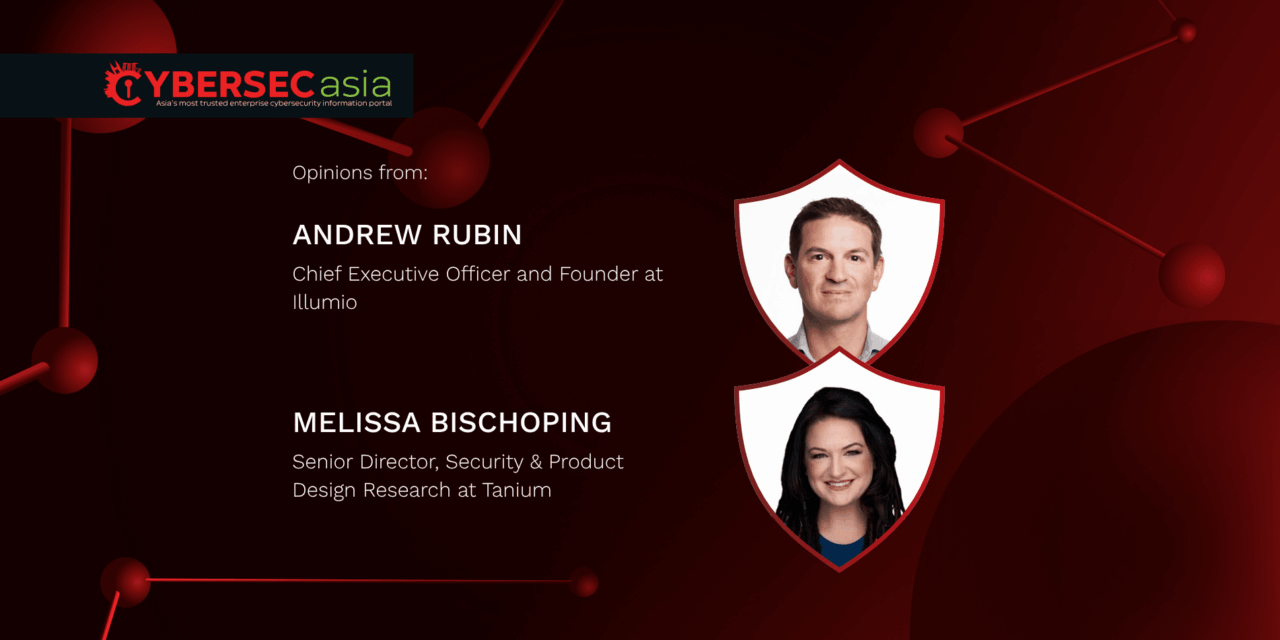
Melissa Bischoping, Senior Director, Security & Product Design Research at Tanium, does not think so: “Guardrails are just that – guardrails. Like the ones on the highway, they can keep most people from accidentally drifting off course, but a sufficiently determined and capable vehicle can break through them or jump over them.”

Andrew Rubin, Chief Executive Officer and Founder at Illumio, concurs: “The introduction of guardrails isn’t evidence that the problem is solved – it’s an admission that even the companies building these models don’t fully trust where the capability leads.”

He adds: “Constraints at the interface don’t change the underlying math; they simply shape how people can interact with it. Attackers won’t operate at that layer. They’ll go straight after the capability itself. And as these tools become more broadly available, the speed and scale of attacks will only increase. The real question isn’t whether guardrails exist – it’s whether defenders are prepared to operate at the same speed.”

On the prospect that broad access to Mythos-level intelligence accelerates the pace at which vulnerabilities are found and exploited, a pressure point for already-stretched regional teams, Bischoping says: “We are already seeing an uptick in reported vulnerabilities, and that problem was already something every org struggled to wrangle even in the pre-AI era.”

What to do

She warns: “We should consider guardrails as one layer of defense, and continue to build our defense-in-depth strategies with this in mind. For defenders, assume the guardrails will keep otherwise honest users from making big mistakes easily, but don’t assume they make a model inherently ‘safe’. These tools allow complex logic and tasks to execute faster than ever before, but ultimately the visibility required to determine when something is wrong in your environment hasn’t changed – you need robust telemetry and incident response playbooks that are capable of moving just as fast.”

Most organizations use CVSS scores and the likes to weight severity and prioritization, but the widespread adoption of Mythos-class AI means that previously ‘low threat/low probability for exploitation’ bugs are more likely to be exploited.

“We need to have a serious conversation about using real-time threat-informed data to prioritize,” says Bischoping. “Beyond just vulnerability response, we should be adopting hygiene practices that reduce the number of unnecessary apps and attack surfaces in general, and improving visibility, policy enforcement, and hardening elsewhere.”

She adds: “We know the technology and knowledge for how to efficiently patch bugs exists, but every leader in every organization needs to take a hard look at the political climate and appetite for modernization and change – this is often the real hurdle to adoption and deployment. It’s not just the patch lifecycles that will be overhauled in this new tech frontier.”

On how long the controls will hold, Bischoping is direct about the planning assumption leaders should adopt: “The math that makes AI work also makes AI vulnerable to attack and manipulation in a near infinite number of ways, so while it’s impossible to say ‘how long’, we do need to be realistic that it’s likely, and that equally capable models with less benevolent alignment training will emerge and be weaponized. Bottom line: Long-term resilience strategy should be operating on the assumption that model capabilities for adversaries and defenders will continue to advance, which further compresses the time between vulnerability discovery and exploitation.”
Share:

PreviousZero-day exploit disclosed hours after massive Patch Tuesday release
NextNorth Korea-linked phishing campaign targets developers through malicious repositories

Related Posts

Experts respond to Spring4Shell vulnerability

Experts respond to Spring4Shell vulnerability

Friday, April 1, 2022

How financial institutions can make ransomware a less lucrative business

How financial institutions can make ransomware a less lucrative business

Monday, May 31, 2021

Absolutely hate your streaming service’s recommended playlists? Here is why …

Absolutely hate your streaming service’s recommended playlists? Here is why …

Tuesday, March 23, 2021

Is the world more secure in their remote-working security now?

Is the world more secure in their remote-working security now?

Tuesday, June 8, 2021

Leave a reply Cancel reply

You must be logged in to post a comment.

Voters-draw/RCA-Sponsors

Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
previous arrow
next arrow

CybersecAsia Voting Placement

Gamification listing or Participate Now

LEARN MORE

Vote Now -Placement(Google Ads)

Top-Sidebar-banner

Whitepapers

  • Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Cyber threats have become more frequent and sophisticated, targeting organizations of all sizes across all …Download Whitepaper
  • Zero Trust Made Simple: Why it matters and how to get started

    Zero Trust Made Simple: Why it matters and how to get started

    Data breaches and cyberattacks are no longer limited to large, high-profile organizations.Download Whitepaper
  • Cloud Secure Edge: Remote access, better security

    Cloud Secure Edge: Remote access, better security

    ​SonicWall Cloud Secure Edge™ is a modern, cloud-native Security Service Edge (SSE) solution that addresses …Download Whitepaper
  • Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Insider threats continue to be a major cybersecurity risk in 2024. Explore more insights on …Download Whitepaper

Middle-sidebar-banner

Case Studies

  • How a Vietnamese D2C retailer built its own secure digital infrastructure

    How a Vietnamese D2C retailer built its own secure digital infrastructure

    Would your organization build your own digital infrastructure – including AI governance and cybersecurity – …Read more
  • Cyber protection for medical clinics in Singapore

    Cyber protection for medical clinics in Singapore

    As Singapore’s healthcare sector becomes increasingly digital and interconnected, clinics are facing heightened cyber risks, …Read more
  • India’s WazirX strengthens governance and digital asset security

    India’s WazirX strengthens governance and digital asset security

    Revamping its custody infrastructure using multi‑party computation tools has improved operational resilience and institutional‑grade safeguardsRead more
  • Bangladesh LGED modernizes communication while addressing data security concerns

    Bangladesh LGED modernizes communication while addressing data security concerns

    To meet emerging data localization/privacy regulations, the government engineering agency deploys a secure, unified digital …Read more

Bottom sidebar

Other News

  • CyberLogitec Brings Tag-Free Collision Prevention to Busan New Port

    Tuesday, October 6, 2026
    Digital twin places workers and …Read More »
  • Aligning with Global Regulations: iMQ Technology’s SQ713x Secure Element Achieves SESIP and PSA Certified Level 3

    Monday, October 5, 2026
    Passes Keysight’s physical attack testing …Read More »
  • Cymulate Receives Frost & Sullivan’s 2026 Indian Competitive Strategy Leadership Recognition for Advancing Continuous Security Validation

    Monday, October 5, 2026
    The recognition highlights Cymulate’s competitive …Read More »
  • CyberDSA 2026 Opens in Kuala Lumpur as Malaysia’s AI Ambition Puts Cybersecurity, Trust and Sovereign Capability in Sharper Focus

    Monday, October 5, 2026
    As CyberDSA opens its fourth …Read More »
  • Dahua and PARC Foundation Join Forces to Protect Dreams and Empower Young Filipino Talent

    Monday, October 5, 2026
    TAGUIG CITY, Philippines, Oct. 5, …Read More »
  • Our Brands
  • DigiconAsia
  • MartechAsia
  • Home
  • About Us
  • Contact Us
  • Sitemap
  • Privacy & Cookies
  • Terms of Use
  • Advertising & Reprint Policy
  • Media Kit
  • Subscribe
  • Manage Subscriptions
  • Newsletter

Copyright © 2026 CybersecAsia All Rights Reserved.