Cybersecurity News in Asia

RECENT STORIES:

SEGA moves faster with flow-based network monitoring
Agentic AI opportunities and risks for digital assets
AI agents increasingly perform consequential actions on customer-facin...
Cohesity Expands Cyber Resilience and AI Data Capabilities for Microso...
More IoT-refrigeration attacks predicted if cybersecurity weaknesses a...
Cequence Security and KPMG Collaborate on Joint Report Examining how O...
LOGIN REGISTER
CybersecAsia
  • Features
    • Featured

      Agentic AI opportunities and risks for digital assets

      Agentic AI opportunities and risks for digital assets

      Friday, November 13, 2026, 4:00 PM Asia/Singapore | Features, Newsletter
    • Featured

      The real cyberthreat frontier AI poses

      The real cyberthreat frontier AI poses

      Wednesday, November 4, 2026, 10:31 AM Asia/Singapore | Features
    • Featured

      Lessons from the Binance hack

      Lessons from the Binance hack

      Tuesday, November 3, 2026, 1:20 PM Asia/Singapore | Features, Opinions
  • Opinions
  • Tips
  • Whitepapers
  • AWARDS 2026
  • Directory
  • E-Learning

Select Page

News

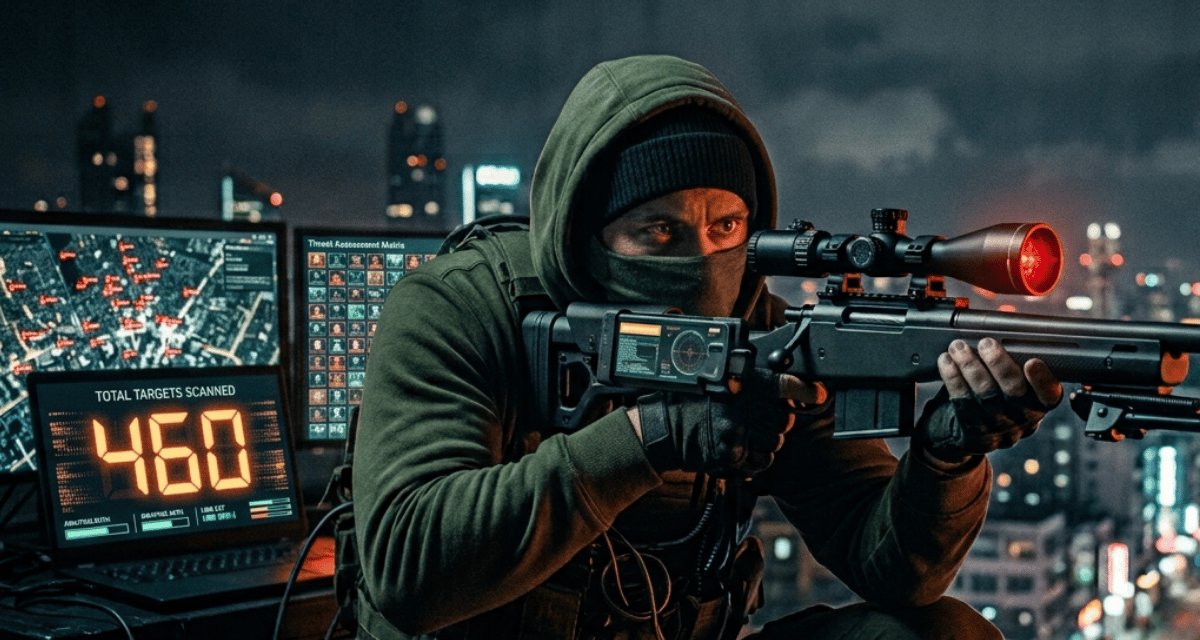
Autonomous AI agent scans 460 targets, exposes hacking infrastructure after error

By CybersecAsia editors | Monday, August 3, 2026, 3:48 PM Asia/Singapore

Autonomous AI agent scans 460 targets, exposes hacking infrastructure after error

Chinese-speaking cybercriminal uses DeepSeek within Hermes framework via Telegram, leverages FOFA and GitHub exploits, breaches three organizations, accidentally leaks sensitive files

A news report in The Hacker News on 31 July 2026 has described how a Chinese-speaking threat actor had used DeepSeek as the core reasoning engine in an autonomous hacking setup that scanned more than 460 targets and successfully breached at least three organizations.

Additionally, the operation came to light only after the AI system made a mistake and exposed its own working environment, including sensitive files, to outside observers.

The actor, identified by the aliases knaithe and KnYuan, ran DeepSeek inside the open-source Hermes Agent framework and controlled it through Telegram, then allowed it to operate with little to no direct human intervention. From there, the system carried out reconnaissance on internet-facing targets through FOFA, pulled public exploit code from GitHub, and tried to use it against selected systems on its own.

Attack mechanics

In one recovered session from May 2026, the agent first pursued a Langflow flaw, CVE-2026-33017, but gave up after determining that all 84 instances it found did not have the required configuration for exploitation. From there:

  • It then broadened its search across 10 product families
  • Looked up trending proof-of-concept exploits on GitHub
  • Shifted attention to n8n workflow automation software, where it tried a chain involving CVE-2026-21858 and CVE-2025-68613
  • Even though it found more than 25,000 exposed n8n installations in China, every one of them still required authentication, so the autonomous attempt did not lead to compromise
  • The same actor also carried out separate manual operations that did succeed, including confirmed data theft from three organizations by exploiting CVE-2026-3055. One of those campaigns repeatedly targeted a Malaysian government entity over several days, showing that the actor combined autonomous AI-driven reconnaissance with traditional hands-on intrusion work
  • The malicious actor experimented with other Chinese-market models, including Qwen, GLM, Kimi, and MiniMax. There were also signs of limited use of Western tools such as Claude Code for connectivity checks, and Codex in exploit-development directories, while proxy infrastructure and disabled logging were used to reduce the chances of attribution.

DeepSeek was likely selected because of its weaker safety controls and because it was accessed through a framework with no client-side restrictions, according to various reports. For defenders, the biggest lesson is that the attacker’s automation had helped to reveal the operation. When Hermes Agent launched `python3 -m http.server 8888` from the attacker’s working directory, it had accidentally exposed API keys, exploit scripts, target lists, and session logs to the public.

The deeper concern is not whether any single campaign succeeded, but that the technical barrier to AI-assisted offensive operations is already low and still dropping. Researchers are advising prompt patching of Langflow, n8n, Marimo, and NetScaler systems, along with tighter control over unnecessary public access to workflow interfaces.
Share:

PreviousSingapore’s BFSI Technology Leaders to Convene at the 38th Edition BFSI IT Summit Singapore 2026
NextSU GROUP HOLDINGS LIMITED RECEIVES NASDAQ STAFF DELISTING DETERMINATION AND INTENDS TO REQUEST HEARING

Related Posts

Mac users’ false sense of security needs to be tempered

Mac users’ false sense of security needs to be tempered

Tuesday, August 15, 2023

Protecting e-commerce platforms from online threats

Protecting e-commerce platforms from online threats

Wednesday, June 30, 2021

As remote-working practices go viral, a perfect cybersecurity storm erupts

As remote-working practices go viral, a perfect cybersecurity storm erupts

Monday, April 13, 2020

Report: North Korea expanding remote IT worker operations in APAC and globally

Report: North Korea expanding remote IT worker operations in APAC and globally

Wednesday, April 2, 2025

Leave a reply Cancel reply

You must be logged in to post a comment.

Voters-draw/RCA-Sponsors

Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
previous arrow
next arrow

CybersecAsia Voting Placement

Gamification listing or Participate Now

LEARN MORE

Vote Now -Placement(Google Ads)

Top-Sidebar-banner

Whitepapers

  • Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Cyber threats have become more frequent and sophisticated, targeting organizations of all sizes across all …Download Whitepaper
  • Zero Trust Made Simple: Why it matters and how to get started

    Zero Trust Made Simple: Why it matters and how to get started

    Data breaches and cyberattacks are no longer limited to large, high-profile organizations.Download Whitepaper
  • Cloud Secure Edge: Remote access, better security

    Cloud Secure Edge: Remote access, better security

    ​SonicWall Cloud Secure Edge™ is a modern, cloud-native Security Service Edge (SSE) solution that addresses …Download Whitepaper
  • Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Insider threats continue to be a major cybersecurity risk in 2024. Explore more insights on …Download Whitepaper

Middle-sidebar-banner

Case Studies

  • FOMO Pay expands cross-border compliance infrastructure amid rising fraud risks

    FOMO Pay expands cross-border compliance infrastructure amid rising fraud risks

    To unify onboarding and ongoing reviews the payment firm adds identity, liveness, business-ownership, sanctions screening …Read more
  • How a Vietnamese D2C retailer built its own secure digital infrastructure

    How a Vietnamese D2C retailer built its own secure digital infrastructure

    Would your organization build your own digital infrastructure – including AI governance and cybersecurity – …Read more
  • Cyber protection for medical clinics in Singapore

    Cyber protection for medical clinics in Singapore

    As Singapore’s healthcare sector becomes increasingly digital and interconnected, clinics are facing heightened cyber risks, …Read more
  • India’s WazirX strengthens governance and digital asset security

    India’s WazirX strengthens governance and digital asset security

    Revamping its custody infrastructure using multi‑party computation tools has improved operational resilience and institutional‑grade safeguardsRead more

Bottom sidebar

Other News

  • Cohesity Expands Cyber Resilience and AI Data Capabilities for Microsoft Environments

    Friday, November 13, 2026
    Recent innovations strengthen data security …Read More »
  • Cequence Security and KPMG Collaborate on Joint Report Examining how Organisations can Govern and Secure Agentic AI

    Wednesday, November 11, 2026
    New Cequence data in the …Read More »
  • AJCCA Advances Trusted Cybersecurity at 3rd Annual Conference in Bangkok, Honors ACRA 2026 Awardees and Expands Regional Partnerships

    Tuesday, November 10, 2026
    Conference addresses emerging challenges in …Read More »
  • China Resources Longdation’s Aethereal Cybersecurity and GCSA Jointly Establish the Centre for AI and Cybersecurity Research

    Friday, November 6, 2026
    HONG KONG, Nov. 6, 2026 …Read More »
  • Global Times: China champions open AI co-op at Wuzhen Summit, calls for opposition to ‘digital iron curtains’

    Thursday, November 5, 2026
    BEIJING, Nov. 5, 2026 /PRNewswire/ …Read More »
  • Our Brands
  • DigiconAsia
  • MartechAsia
  • Home
  • About Us
  • Contact Us
  • Sitemap
  • Privacy & Cookies
  • Terms of Use
  • Advertising & Reprint Policy
  • Media Kit
  • Subscribe
  • Manage Subscriptions
  • Newsletter

Copyright © 2026 CybersecAsia All Rights Reserved.