Cybersecurity News in Asia

RECENT STORIES:

SEGA moves faster with flow-based network monitoring
More than 23,500 customers affected by SIMBA data breach
Cellid and Megane Top Partner to Commercialize and Expand the AR Glass...
ICAC and UNODC’s pioneering international anti-graft training br...
Singapore police flag 3.64m dormant “shell pages” for takedown in Mid-...
Zero-click flaw enables remote code execution in four mainstream AI co...
LOGIN REGISTER
CybersecAsia
  • Features
    • Featured

      Shadow AI Is the New Insider Threat

      Shadow AI Is the New Insider Threat

      Monday, September 21, 2026, 9:11 AM Asia/Singapore | Features, Newsletter, Sponsored, Tips
    • Featured

      Addressing the AI-driven vulnerability debt

      Addressing the AI-driven vulnerability debt

      Thursday, September 17, 2026, 10:03 AM Asia/Singapore | Features, Sponsored
    • Featured

      Cybercriminals zero In on APAC’s digital boom, SMBs in the crosshairs

      Cybercriminals zero In on APAC’s digital boom, SMBs in the crosshairs

      Monday, September 14, 2026, 2:30 PM Asia/Singapore | Features, Sponsored
  • Opinions
  • Tips
  • Whitepapers
  • AWARDS 2026
  • Directory
  • E-Learning

Select Page

Tips

Fake CAPTCHA challenges are weaponizing trust to spread malware across platforms

By L L Seow | Monday, March 30, 2026, 8:13 AM Asia/Singapore

Fake CAPTCHA challenges are weaponizing trust to spread malware across platforms

Attackers are using AI-enhanced social engineering to mimic verification checks and steal data on Windows, macOS, and Android systems: stay vigilant!

It was only a matter of time before a tool to establish trust in web browsing would become weaponized against users. In recent news, the world saw the first known instance of a macOS attack combining the ClickFix social engineering technique with a Python payload (compiled into a native binary using the Nuitka framework).

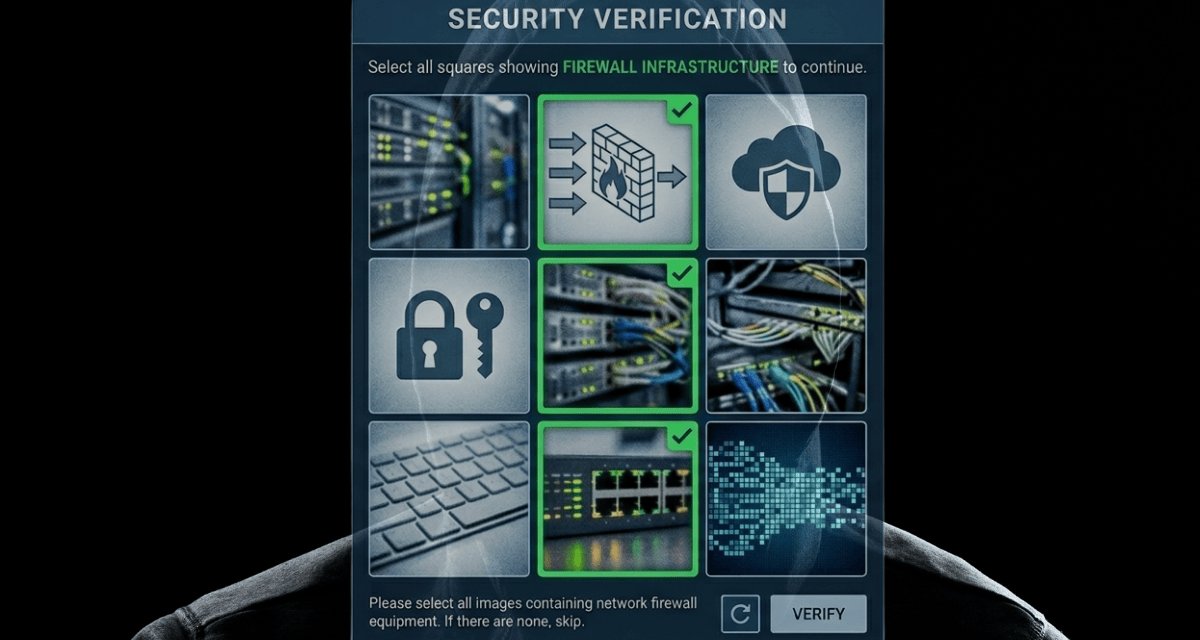
Fake CAPTCHA pages trick users into installing malware by mimicking trusted verification checks from services such as Cloudflare or Google. These attacks, known as ClickFix campaigns, have hit macOS with malicious elements like Infiniti Stealer; Windows browsers via command prompts; and Android through app sideloading.

Attackers now use AI to craft hyper-realistic pages, videos, and personalized lures, making them harder to spot. This guide arms readers with steps to preempt these threats across platforms.

Understand the attack vector

Attackers lure victims via Search Engine Optimization poisoning, phishing emails, or compromised sites to domains hosting fake CAPTCHAs. The infected page claims a “human check” and instructs users to paste commands into Terminal (macOS), Run dialog (Windows), or downloading APKs (Android).

On desktops browsers, this ruse deploys droppers leading to infostealers grabbing passwords, crypto wallets, and screenshots. Android variants push malicious apps hiding as news or ID tools. AI enhances this by generating convincing tutorials, obfuscated code, and dynamic redirects that evade filters.

Such ruses are so convincing that even diligent cybersecurity-savvy web users can be blindsided. So, how can we spot red flags instantly when a particular captcha seems overly “innovative”?

  • Real CAPTCHAs never demand system access. Watch for these hallmarks:
    • Urgent prompts such as “Verify now or lose access.”Requests to open Terminal, Run (Win+R), or enable unknown sources on Android.
    • Mismatched domains: Legitimate Cloudflare humanness checks use checking.cloudflare[.]com, not random strings or dubious servers
    • Embedded videos demoing the “”fix”, now common in AI-boosted campaigns

AI variants may personalize: Pages could be adapted to users’ operating system, browser, or personal information scraped from social media footprints. To foil even circumspect users from hovering over URLs to spot suspicious link, phishers use link shorteners or chains now. On mobile, overlays mimic system alerts, causing some panicky users to drop their guard.

Platform-specific defenses
With fake captcha mechanisms pervasive on most platforms now, it pays to be familiar with the core techniques and protections in case we can help spread the word to others:

  • Windows
    Fake pages target the Run dialog for PowerShell droppers. Run Windows Security full scans weekly. Enable Microsoft Defender real-time protection and cloud-delivered updates. Avoid Win+R for unknown / suspicious captcha challenges: use Task Manager to kill suspicious processes that could be running in the browser window.
  • Android
    Scams push “updates” or fake apps via CAPTCHA gates. Stick to Google Play; revoke side-loading permissions (Settings > Apps > Special access > Install unknown apps). Google Play Protect scans automatically — ensure it is on. Check app permissions before installs.
  • macOS
    Gatekeeper blocks unsigned apps, but ClickFix bypasses via user-run commands. Never paste web-sourced code into Terminal. Enable System Settings > Privacy & Security > Security to require approvals. Install additional malware protection software to scans for info stealers and unusual processes running within the browser.
  • Browser and network shields
    Install uBlock Origin (freeware) or NoScript (open source) to block malicious scripts. AdGuard or NextDNS can filter phishing domains fleet-wide. Enable safe browsing:
    • Chrome/Edge: Settings > Privacy > Safe Browsing (Enhanced)
    • Firefox: Enable HTTPS-Only Mode and Enhanced Tracking Protection
    • Safari: Advanced > Fraudulent Website Warning

For AI threats, use browser extensions that check URLs for poor reputations before even attempting to see if they work. AI detectors in some cybersecurity software can also scan for natural language anomalies in web content.

AI-powered evolution and counters

Nowadays, attackers leverage AI for:

  • Obfuscated payloads dodging signatures
  • Personalized lures from public data
  • Computer-vision CAPTCHAs auto-solving legit checks

To counter these tactics, use AI defenders:

  • Microsoft Defender spots and checks CAPTCHA gates.
  • Bitdefender or Webroot use machine learning to detect zero-day exploits
  • Use phishing simulations to train staff and keep them vigilant
  • Keep all operating systems, security patching and apps updated promptly (watch out for buggy or spurious updates, though)

Respond correctly if compromised

Act fast from a clean device:

  • Change all passwords, revoke API/SSH keys
  • Scan with multiple cybersecurity and anti-malware tools
  • Monitor all accounts for odd activity; freeze credit if needed
  • Check Task Manager/Activity Monitor for anomalies such as high CPU from Nuitka binaries.

Finally, build lasting habits: Alwaysturn cyber vigilance measures into muscle memory and encourage others to do so:

  • Verify sites via direct search: type cloudflare.com manually.
  • Use a password manager with breach alerts.
  • Enable multi-factor authentication everywhere, preferring app-based, instead of the vulnerable SMS pathway alone.
  • Educate others we come into contact with, if they seem to require cyber vigilance assistance

In 2026, with the AI arms race raging, conscious vigilance trumps tech alone — question every prompt,  pop-up dialog box or “error message”!
Share:

PreviousShorter TLS certificate lifespans raise renewal challenges for stretched IT teams
NextDid geopolitical tensions drive 130% surge in Gulf-targeted phishing, malware attacks?

Related Posts

Why APAC Teams Need to Stop Worshipping CVSS Scores

Why APAC Teams Need to Stop Worshipping CVSS Scores

Monday, August 3, 2026

Can legacy cybersecurity solutions protect the new reality of distributed workforces?

Can legacy cybersecurity solutions protect the new reality of distributed workforces?

Wednesday, February 23, 2022

The Triple Threat: Cyber, AI, and Quantum

The Triple Threat: Cyber, AI, and Quantum

Thursday, October 17, 2024

Know the four thrusts of corporate cyber resilience and vigilance

Know the four thrusts of corporate cyber resilience and vigilance

Friday, March 17, 2023

Leave a reply Cancel reply

You must be logged in to post a comment.

Voters-draw/RCA-Sponsors

Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
previous arrow
next arrow

CybersecAsia Voting Placement

Gamification listing or Participate Now

LEARN MORE

Vote Now -Placement(Google Ads)

Top-Sidebar-banner

Whitepapers

  • Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Cyber threats have become more frequent and sophisticated, targeting organizations of all sizes across all …Download Whitepaper
  • Zero Trust Made Simple: Why it matters and how to get started

    Zero Trust Made Simple: Why it matters and how to get started

    Data breaches and cyberattacks are no longer limited to large, high-profile organizations.Download Whitepaper
  • Cloud Secure Edge: Remote access, better security

    Cloud Secure Edge: Remote access, better security

    ​SonicWall Cloud Secure Edge™ is a modern, cloud-native Security Service Edge (SSE) solution that addresses …Download Whitepaper
  • Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Insider threats continue to be a major cybersecurity risk in 2024. Explore more insights on …Download Whitepaper

Middle-sidebar-banner

Case Studies

  • How a Vietnamese D2C retailer built its own secure digital infrastructure

    How a Vietnamese D2C retailer built its own secure digital infrastructure

    Would your organization build your own digital infrastructure – including AI governance and cybersecurity – …Read more
  • Cyber protection for medical clinics in Singapore

    Cyber protection for medical clinics in Singapore

    As Singapore’s healthcare sector becomes increasingly digital and interconnected, clinics are facing heightened cyber risks, …Read more
  • India’s WazirX strengthens governance and digital asset security

    India’s WazirX strengthens governance and digital asset security

    Revamping its custody infrastructure using multi‑party computation tools has improved operational resilience and institutional‑grade safeguardsRead more
  • Bangladesh LGED modernizes communication while addressing data security concerns

    Bangladesh LGED modernizes communication while addressing data security concerns

    To meet emerging data localization/privacy regulations, the government engineering agency deploys a secure, unified digital …Read more

Bottom sidebar

Other News

  • Cellid and Megane Top Partner to Commercialize and Expand the AR Glasses Business

    Friday, September 25, 2026
    Combining Cellid’s Technological Expertise with Megane …Read More »
  • ICAC and UNODC’s pioneering international anti-graft training brings together law enforcers worldwide to combat illicit enrichment

    Friday, September 25, 2026
    HONG KONG, Sept. 25, 2026 …Read More »
  • Cohesity Introduces Agent Resilience to Protect and Recover AI Agent Infrastructure

    Tuesday, September 22, 2026
    Cohesity Agent Resilience launches with …Read More »
  • LRQA Named ‘Best in Critical Infrastructure Protection’ at CybersecAsia Readers’ Choice Awards 2026

    Monday, September 21, 2026
    Prestigious regional recognition highlights LRQA’s …Read More »
  • Cyble and Cyber Security Council of UAE Sign MOU to Strengthen National Threat Intelligence Capabilities

    Thursday, September 17, 2026
    ABU DHABI, UAE, Sept. 17, …Read More »
  • Our Brands
  • DigiconAsia
  • MartechAsia
  • Home
  • About Us
  • Contact Us
  • Sitemap
  • Privacy & Cookies
  • Terms of Use
  • Advertising & Reprint Policy
  • Media Kit
  • Subscribe
  • Manage Subscriptions
  • Newsletter

Copyright © 2026 CybersecAsia All Rights Reserved.