Cybersecurity News in Asia

RECENT STORIES:

SEGA moves faster with flow-based network monitoring
Post Quantum Cryptography readiness in South-east Asia: an update
Advantech Partners with DEKRA, Signing MOU to Strengthen Global Indust...
Hackers cause legacy IoT refrigerators at hundreds of French supermark...
AUTOCRYPT Celebrated As “Automotive Cybersecurity Company of the...
Communications infrastructure – from legacy risk to modern resilience...
LOGIN REGISTER
CybersecAsia
  • Features
    • Featured

      Communications infrastructure – from legacy risk to modern resilience

      Communications infrastructure – from legacy risk to modern resilience

      Thursday, October 15, 2026, 2:08 PM Asia/Singapore | Features
    • Featured

      Advancing OT Cyber Readiness and Resilience in Southeast Asia

      Advancing OT Cyber Readiness and Resilience in Southeast Asia

      Wednesday, October 14, 2026, 10:00 AM Asia/Singapore | Features, News, Sponsored
    • Featured

      How CISOs can set human boundaries for autonomous cybersecurity

      How CISOs can set human boundaries for autonomous cybersecurity

      Wednesday, October 7, 2026, 11:05 AM Asia/Singapore | Features, Newsletter, Tips
  • Opinions
  • Tips
  • Whitepapers
  • AWARDS 2026
  • Directory
  • E-Learning

Select Page

News

Researchers discover way to bypass CPU Spectre v2 protections to intercept sensitive data

By CybersecAsia editors | Friday, August 14, 2026, 12:25 PM Asia/Singapore

Researchers discover way to bypass CPU Spectre v2 protections to intercept sensitive data

Researchers detail Interrupt Injection side-channel on AMD and Intel processors, exposing /etc/shadow contents despite eIBRS and Safe RET mitigations

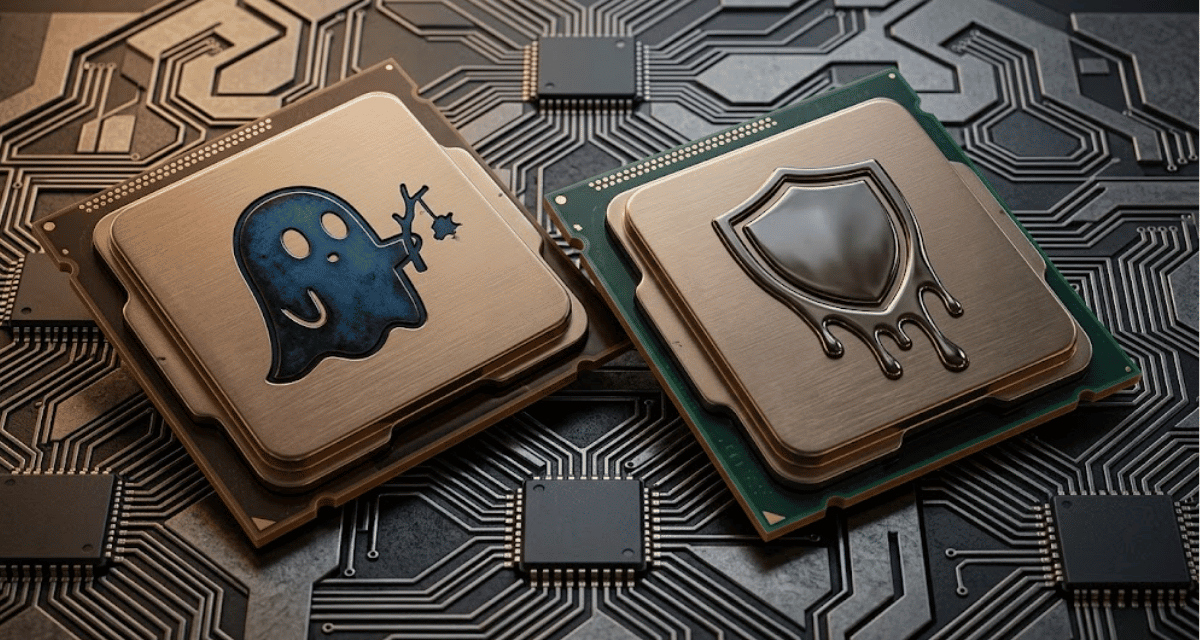
Researchers at MIT’s Computer Science and Artificial Intelligence Laboratory (CSAIL) have unveiled findings on 6 August 2026, a new CPU side-channel technique that cuts straight through existing Spectre v2 defenses on both AMD and Intel chips, showing that it is possible to pull Linux password hashes out of kernel memory despite modern mitigations.

The work, described on their website, targets Spectre v2-style branch prediction protections that vendors have promoted as core safeguards against speculative execution attacks.

The attack primitive is named TONTOU (“Time-of-Neutralization to Time-of-Use”) and it focuses on a subtle timing gap in how processors handle branch predictor cleanup. Contemporary Spectre v2 countermeasures such as Intel’s Enhanced Indirect Branch Restricted Speculation (eIBRS) and AMD’s Safe RET mechanism, operate by flushing or compartmentalizing branch prediction state so it cannot be abused by speculative execution.

However, as PhD student Daniël Trujillo and associate professor Mengjia Yan discovered, there is an unavoidable window between the instant the branch predictor is sanitized and the point at which those sanitized predictions are actually consumed by the CPU. TONTOU weaponizes that tiny interval using what the researchers call “Interrupt Injection”.

Interrupt Injection explained

By carefully arranging for a hardware interrupt to arrive precisely inside that neutralized-to-use gap, an unprivileged user-space process can re-poison the branch predictor after the defense has already executed, but before the CPU relies on the supposedly safe prediction data.

In a conversation with security outlet BleepingComputer, Trujillo explained that this enables an attacker with no special privileges “to read arbitrary memory from the system, including sensitive data such as hashed passwords.” The result is that protection schemes previously thought to block speculative branch mispredictions can be sidestepped by extremely fine-grained timing control delivered purely from local code.

In 10 independent trials, the exploit succeeded in identifying and extracting the contents of the /etc/shadow file — which on Linux holds the system’s password hashes — in five cases. On average, each successful run took about 18 minutes to complete from start to finish, illustrating that the leak is slow but feasible in realistic time frames for a determined local adversary.

The researchers also confirmed that the same TONTOU concept applies to Intel processors that ship with Spectre v2 defenses like eIBRS. Nonetheless, they note that practical exploitation on Intel hardware is more complex because it depends on additional software conditions and configuration details, making the proof-of-concept attack harder to reproduce than on the tested AMD Zen 2 system. That nuance is important: both vendors’ CPUs are theoretically exposed, but the real-world barrier to exploitation differs per platform.

Official responses

AMD has responded to the disclosure by acknowledging that the problem “appears to be associated” with how the Linux kernel integrates the Safe RET mitigation rather than being purely a consequence of the microarchitecture itself. In other words, the interaction between the operating system’s implementation and the CPU’s protective feature is what opens the timing window that TONTOU can reach. MIT CSAIL notes that AMD has now issued a patch aimed at neutralizing the attack path, and that mitigation is being delivered to end users through standard operating system updates, including Linux distributions.

The group intend to publish more technical detail when they present at USENIX Security 2026 in October. Their research highlights a persistent reality in hardware and microarchitecture security: even carefully engineered Spectre v2 mitigations can still leave exploitable timing gaps that attackers with only unprivileged local code execution can surgically target. As speculative execution defenses grow more intricate, TONTOU serves as a reminder that defenders must consider not just what state is sanitized, but exactly when and how that sanitization intersects with real-world CPU behavior.

Share:

PreviousSUPCON and Certis Sign Strategic Cooperation Agreement to Advance Robotics in Security Operations
NextGeeLark Upgrades Browser Infrastructure with Version 150 and Team Password Management

Related Posts

Tips for tightening fraud management in the e-commerce boom

Tightening fraud management in the e-commerce boom

Tuesday, July 20, 2021

EU demands tech giants explain safeguards as online financial scams surge across digital platforms

EU demands tech giants explain safeguards as online financial scams surge across digital platforms

Monday, September 29, 2025

Sep–Nov 2025 data breaches in review: Prevention and proactive-ness are key

Sep–Nov 2025 data breaches in review: Prevention and proactive-ness are key

Tuesday, November 11, 2025

Gaming operators in the region struggle with a cyber game they dread losing

Gaming operators in the region struggle with a cyber game they dread losing

Wednesday, November 2, 2022

Leave a reply Cancel reply

You must be logged in to post a comment.

Voters-draw/RCA-Sponsors

Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
previous arrow
next arrow

CybersecAsia Voting Placement

Gamification listing or Participate Now

LEARN MORE

Vote Now -Placement(Google Ads)

Top-Sidebar-banner

Whitepapers

  • Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Cyber threats have become more frequent and sophisticated, targeting organizations of all sizes across all …Download Whitepaper
  • Zero Trust Made Simple: Why it matters and how to get started

    Zero Trust Made Simple: Why it matters and how to get started

    Data breaches and cyberattacks are no longer limited to large, high-profile organizations.Download Whitepaper
  • Cloud Secure Edge: Remote access, better security

    Cloud Secure Edge: Remote access, better security

    ​SonicWall Cloud Secure Edge™ is a modern, cloud-native Security Service Edge (SSE) solution that addresses …Download Whitepaper
  • Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Insider threats continue to be a major cybersecurity risk in 2024. Explore more insights on …Download Whitepaper

Middle-sidebar-banner

Case Studies

  • FOMO Pay expands cross-border compliance infrastructure amid rising fraud risks

    FOMO Pay expands cross-border compliance infrastructure amid rising fraud risks

    To unify onboarding and ongoing reviews the payment firm adds identity, liveness, business-ownership, sanctions screening …Read more
  • How a Vietnamese D2C retailer built its own secure digital infrastructure

    How a Vietnamese D2C retailer built its own secure digital infrastructure

    Would your organization build your own digital infrastructure – including AI governance and cybersecurity – …Read more
  • Cyber protection for medical clinics in Singapore

    Cyber protection for medical clinics in Singapore

    As Singapore’s healthcare sector becomes increasingly digital and interconnected, clinics are facing heightened cyber risks, …Read more
  • India’s WazirX strengthens governance and digital asset security

    India’s WazirX strengthens governance and digital asset security

    Revamping its custody infrastructure using multi‑party computation tools has improved operational resilience and institutional‑grade safeguardsRead more

Bottom sidebar

Other News

  • Advantech Partners with DEKRA, Signing MOU to Strengthen Global Industrial Cybersecurity Compliance in Response to EU CRA

    Friday, October 16, 2026
    TAIPEI, Oct. 16, 2026 /PRNewswire/ …Read More »
  • AUTOCRYPT Celebrated As “Automotive Cybersecurity Company of the Year” In 2026 AutoTech Breakthrough Awards Program

    Thursday, October 15, 2026
    Annual Awards Program Recognizes Breakthrough …Read More »
  • Taoping Receives Nasdaq Notification Regarding Minimum Bid Price Deficiency

    Thursday, October 15, 2026
    TIANJIN, China, Oct. 15, 2026 …Read More »
  • From Defence Cooperation to Shared Security: Building a Resilient Pakistan-China Partnership

    Friday, October 9, 2026
    QINGDAO, China, Oct. 9, 2026 …Read More »
  • CyberDSA Sets 19 – 21 October 2027 Return as Industry Participation Builds at Fourth Edition

    Thursday, October 8, 2026
    CyberDSA moves towards its milestone …Read More »
  • Our Brands
  • DigiconAsia
  • MartechAsia
  • Home
  • About Us
  • Contact Us
  • Sitemap
  • Privacy & Cookies
  • Terms of Use
  • Advertising & Reprint Policy
  • Media Kit
  • Subscribe
  • Manage Subscriptions
  • Newsletter

Copyright © 2026 CybersecAsia All Rights Reserved.