Cybersecurity News in Asia

RECENT STORIES:

SEGA moves faster with flow-based network monitoring
Agentic AI opportunities and risks for digital assets
AI agents increasingly perform consequential actions on customer-facin...
Cohesity Expands Cyber Resilience and AI Data Capabilities for Microso...
More IoT-refrigeration attacks predicted if cybersecurity weaknesses a...
Cequence Security and KPMG Collaborate on Joint Report Examining how O...
LOGIN REGISTER
CybersecAsia
  • Features
    • Featured

      Agentic AI opportunities and risks for digital assets

      Agentic AI opportunities and risks for digital assets

      Friday, November 13, 2026, 4:00 PM Asia/Singapore | Features, Newsletter
    • Featured

      The real cyberthreat frontier AI poses

      The real cyberthreat frontier AI poses

      Wednesday, November 4, 2026, 10:31 AM Asia/Singapore | Features
    • Featured

      Lessons from the Binance hack

      Lessons from the Binance hack

      Tuesday, November 3, 2026, 1:20 PM Asia/Singapore | Features, Opinions
  • Opinions
  • Tips
  • Whitepapers
  • AWARDS 2026
  • Directory
  • E-Learning

Select Page

News

North Korean group linked to multiple open-source supply chain package attacks

By CybersecAsia editors | Friday, July 31, 2026, 2:41 PM Asia/Singapore

North Korean group linked to multiple open-source supply chain package attacks

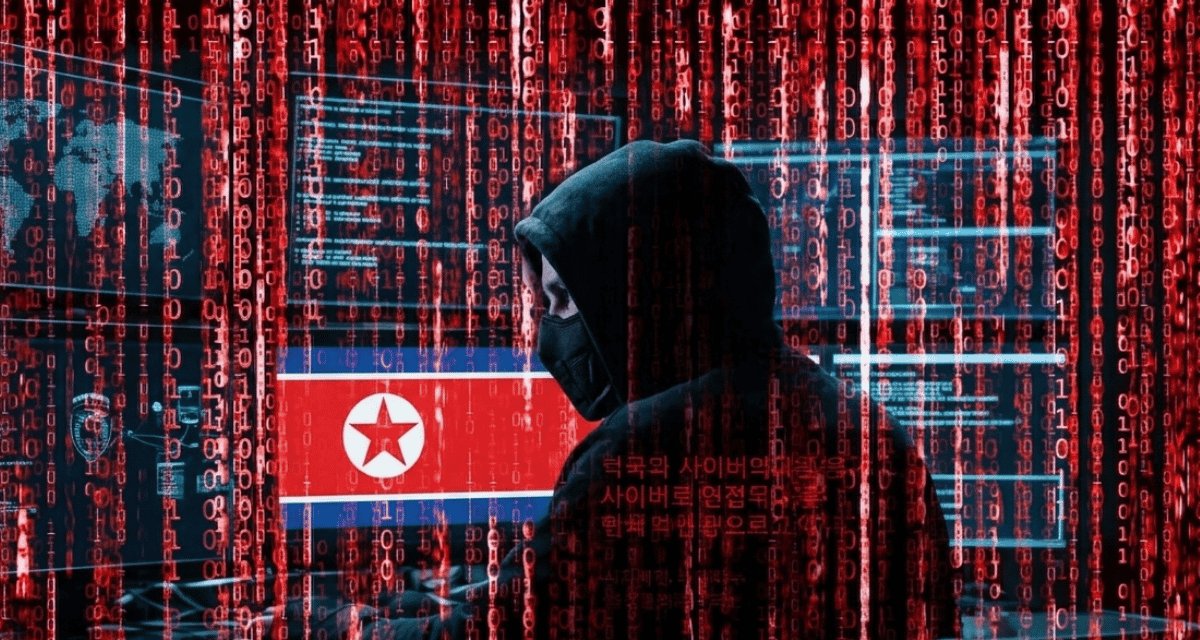
Threat investigators connect four previous npm library breaches affecting axios, debug, chalk, and typo-crypto packages, to a single source.

After investigating a series of seemingly unrelated high-profile open-source software attacks on open-source software packages, Amazon’s threat-intelligence unit has established that four previous attacks can be linked to a single North Korean hacking group.

The firm has announced that the breaches of four Node Package Manager (npm) libraries — axios, debug, chalk, and typo-crypto — can be traced to a cluster of aliases linked to Pyongyang: Sapphire Sleet, Stardust Chollima, BlueNoroff, CageyChameleon, and Alluring Pisces.

Starting in March 2025, the North Korean threat group had seeded a trojanized file named core.js inside the small, little-used open source typo-crypto package, masquerading it as the legitimate core-js library and activating only when it detected a specific numeric input before reaching out to an attacker-controlled server to fetch a second-stage payload tailored to Windows, macOS, or Linux. It is now believed to have been a dry run for the subsequent attacks.

Six months on, in September 2025, the same playbook had been used against debug and chalk, two widely-used logging and styling utilities. According to some reports, roughly one in 10 cloud environments had been affected within a two-hour window.

The campaign then culminated in March 2026 with the compromise of axios, a ubiquitous HTTP client library downloaded more than 100m times each week, which had already been linked to the North Korean cluster tracked as UNC1069.

In each case, the attackers did not break in through technical vulnerabilities but instead had cultivated relationships with trusted maintainers who already had publishing rights. This was exploited to push malicious updates containing hidden code. A spokesperson said the threat actors had basically earned the trust of an employee “to hand them the keys.” Also, the investigations have found that the attackers had used generative AI to:

  • draft and obfuscate payloads
  • apply execution gating to evade sandboxes
  • probe AI-based code-auditing tools
  • create synthetic maintainer identities
  • exploit “slopsquatting” opportunities to hallucinate package names

The attribution to North Korean entities is tagged with “medium confidence” in geopolitical terms: implying that greater operational efficiency translates directly into more illicit revenue to fund further prohibited activities.
Share:

PreviousHow converging physical and digital identity systems can reduce risk and improve governance
NextWhy APAC Teams Need to Stop Worshipping CVSS Scores

Related Posts

Despite strong talent supply growth, APAC is short of 2.2m cybersecurity professionals

Despite strong talent supply growth, APAC is short of 2.2m cybersecurity professionals

Wednesday, October 26, 2022

Eight ever-growing cyber threats that should keep CISOs up at night

Eight ever-growing cyber threats that should keep CISOs up at night

Tuesday, January 21, 2025

Hackers are now abusing emails from legitimate online services to snare victims

Hackers are now abusing emails from legitimate online services to snare victims

Wednesday, April 5, 2023

CISOs can navigate emerging risks from autonomous AI with a new security framework

CISOs can navigate emerging risks from autonomous AI with a new security framework

Tuesday, August 26, 2025

Leave a reply Cancel reply

You must be logged in to post a comment.

Voters-draw/RCA-Sponsors

Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
previous arrow
next arrow

CybersecAsia Voting Placement

Gamification listing or Participate Now

LEARN MORE

Vote Now -Placement(Google Ads)

Top-Sidebar-banner

Whitepapers

  • Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Cyber threats have become more frequent and sophisticated, targeting organizations of all sizes across all …Download Whitepaper
  • Zero Trust Made Simple: Why it matters and how to get started

    Zero Trust Made Simple: Why it matters and how to get started

    Data breaches and cyberattacks are no longer limited to large, high-profile organizations.Download Whitepaper
  • Cloud Secure Edge: Remote access, better security

    Cloud Secure Edge: Remote access, better security

    ​SonicWall Cloud Secure Edge™ is a modern, cloud-native Security Service Edge (SSE) solution that addresses …Download Whitepaper
  • Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Insider threats continue to be a major cybersecurity risk in 2024. Explore more insights on …Download Whitepaper

Middle-sidebar-banner

Case Studies

  • FOMO Pay expands cross-border compliance infrastructure amid rising fraud risks

    FOMO Pay expands cross-border compliance infrastructure amid rising fraud risks

    To unify onboarding and ongoing reviews the payment firm adds identity, liveness, business-ownership, sanctions screening …Read more
  • How a Vietnamese D2C retailer built its own secure digital infrastructure

    How a Vietnamese D2C retailer built its own secure digital infrastructure

    Would your organization build your own digital infrastructure – including AI governance and cybersecurity – …Read more
  • Cyber protection for medical clinics in Singapore

    Cyber protection for medical clinics in Singapore

    As Singapore’s healthcare sector becomes increasingly digital and interconnected, clinics are facing heightened cyber risks, …Read more
  • India’s WazirX strengthens governance and digital asset security

    India’s WazirX strengthens governance and digital asset security

    Revamping its custody infrastructure using multi‑party computation tools has improved operational resilience and institutional‑grade safeguardsRead more

Bottom sidebar

Other News

  • Cohesity Expands Cyber Resilience and AI Data Capabilities for Microsoft Environments

    Friday, November 13, 2026
    Recent innovations strengthen data security …Read More »
  • Cequence Security and KPMG Collaborate on Joint Report Examining how Organisations can Govern and Secure Agentic AI

    Wednesday, November 11, 2026
    New Cequence data in the …Read More »
  • AJCCA Advances Trusted Cybersecurity at 3rd Annual Conference in Bangkok, Honors ACRA 2026 Awardees and Expands Regional Partnerships

    Tuesday, November 10, 2026
    Conference addresses emerging challenges in …Read More »
  • China Resources Longdation’s Aethereal Cybersecurity and GCSA Jointly Establish the Centre for AI and Cybersecurity Research

    Friday, November 6, 2026
    HONG KONG, Nov. 6, 2026 …Read More »
  • Global Times: China champions open AI co-op at Wuzhen Summit, calls for opposition to ‘digital iron curtains’

    Thursday, November 5, 2026
    BEIJING, Nov. 5, 2026 /PRNewswire/ …Read More »
  • Our Brands
  • DigiconAsia
  • MartechAsia
  • Home
  • About Us
  • Contact Us
  • Sitemap
  • Privacy & Cookies
  • Terms of Use
  • Advertising & Reprint Policy
  • Media Kit
  • Subscribe
  • Manage Subscriptions
  • Newsletter

Copyright © 2026 CybersecAsia All Rights Reserved.