Cybersecurity News in Asia

RECENT STORIES:

SEGA moves faster with flow-based network monitoring
FBI warning: Attackers increasingly use ARTEX AI framework to automate...
Hidden software bug of July 2026 blamed for global office software out...
As Hijacked Billboards Make Headlines, CAYIN SMP Players Keep Screens ...
Agentic AI opportunities and risks for digital assets
AI agents increasingly perform consequential actions on customer-facin...
LOGIN REGISTER
CybersecAsia
  • Features
    • Featured

      Agentic AI opportunities and risks for digital assets

      Agentic AI opportunities and risks for digital assets

      Friday, November 13, 2026, 4:00 PM Asia/Singapore | Features, Newsletter
    • Featured

      The real cyberthreat frontier AI poses

      The real cyberthreat frontier AI poses

      Wednesday, November 4, 2026, 10:31 AM Asia/Singapore | Features
    • Featured

      Lessons from the Binance hack

      Lessons from the Binance hack

      Tuesday, November 3, 2026, 1:20 PM Asia/Singapore | Features, Opinions
  • Opinions
  • Tips
  • Whitepapers
  • AWARDS 2026
  • Directory
  • E-Learning

Select Page

News

FBI warning: Attackers increasingly use ARTEX AI framework to automate intrusions

By CybersecAsia Editors | Tuesday, November 17, 2026, 4:24 PM Asia/Singapore

FBI warning: Attackers increasingly use ARTEX AI framework to automate intrusions

The agency says criminals and state-linked groups have exploited the open-source tool since August 2026, targeting multiple sectors and reaching privileged access within hours

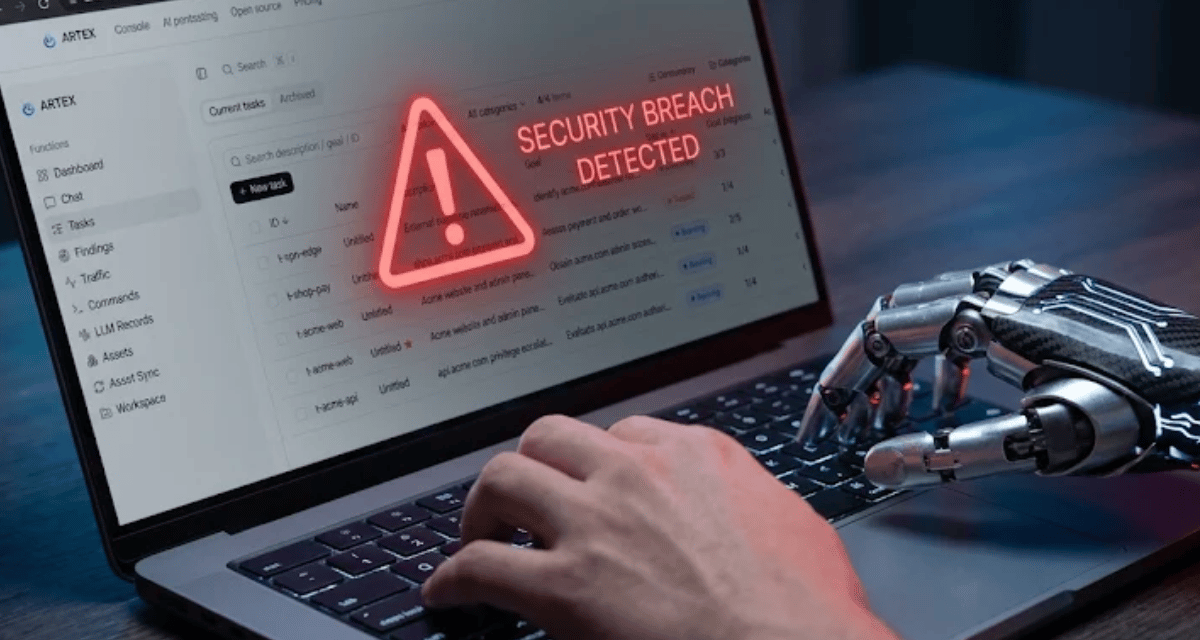
The FBI has warned that attackers are increasingly using ARTEX, an open-source, AI-driven penetration-testing framework, to automate intrusions at “machine speed.”

According to Bleeping Computer, the agency had issued a FLASH alert on 13 November 2026, saying malicious actors have used ARTEX since at least August 2026 against organizations in financial services, government, defense, energy, healthcare and other sectors.)

Some intrusions had progressed from initial targeting to privileged access in under three hours. ARTEX does not include its own AI model; it connects to external providers including Anthropic’s Claude, OpenAI’s GPT and DeepSeek.

The framework has also been linked to a recent breach of cloud-security firm Barracuda. An attacker had entered parts of the firm’s cloud environment between 1 November 2026 and 2 November 2026, reaching about 10 cloud accounts in roughly 44 hours. The firm discovered the intrusion on 4 November 2026.

Breach incident details

The attacker had used a valid cloud access key that the firm had issued to a third-party AI vendor for a completed project. Barracuda said it did not retire the key when the work ended, acknowledging that the lapse was its responsibility. It believes the key had been stolen in October 2026 from a configuration file in the vendor’s GitHub repository. Then:

  • Using credentials found in one system, the intruder had moved into the firm’s data analytics environment, source-code repositories and Kubernetes clusters.
  • According to the firm, the attacker’s probe names, sequence of activity and automated routines for finding credentials and cryptocurrency wallets matched ARTEX.
  • The attacker then searched for Ethereum keystore files and seed phrases, and installed a backdoor in a Kubernetes cluster. It had also accessed a system containing integration credentials for the firm’s XDR managed threat-detection service.
  • The firm has yet to find evidence that those credentials were stolen, but has asked potentially-affected customers to revoke and recreate them.

Barracuda has not attributed the intrusion to a particular actor.

Growing abuse

Although ARTEX’s original developer had removed its GitHub repository on 8 October 2026, the FBI has said the tool continues to circulate through community forks, localized variants, archived copies and a commercial version. In early November 2026 researchers at Censys had identified more than 1,600 publicly exposed ARTEX consoles.

The American Hospital Association has urged hospitals to inventory every internet-facing application. John Riggi, its national advisor for cybersecurity and risk, said ARTEX enables both skilled and unskilled hackers to operate at “machine speed.”

On 16 November 2026, Google said its threat analysts had observed several threat actors using ARTEX and similar frameworks in live intrusions since late August 2026. The group also named CAIRN, CyberStrikeAI, HexStrike AI and PentAGI as other open-source, multi-agent frameworks being abused, according to this report.)
Share:

PreviousHidden software bug of July 2026 blamed for global office software outage

Related Posts

What causes ransomware victims to pay up despite “do not pay” policies?

What causes ransomware victims to pay up despite “do not pay” policies?

Thursday, July 25, 2024

Embedding cybersecurity culture in financial institutions: lessons in leadership, collaboration, and cyber resilience

Embedding cybersecurity culture in financial institutions: lessons in leadership, collaboration, and cyber resilience

Thursday, October 30, 2025

At just US$100 a day to rent malicious botnets, DDoS attacks must escalate

At just US$100 a day to rent malicious botnets, DDoS attacks must escalate

Tuesday, November 30, 2021

Out with emotet, in with trickbot: February 2021’s most wanted malware

Out with emotet, in with trickbot: February 2021’s most wanted malware

Monday, March 15, 2021

Leave a reply Cancel reply

You must be logged in to post a comment.

Voters-draw/RCA-Sponsors

Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
previous arrow
next arrow

CybersecAsia Voting Placement

Gamification listing or Participate Now

LEARN MORE

Vote Now -Placement(Google Ads)

Top-Sidebar-banner

Whitepapers

  • Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Cyber threats have become more frequent and sophisticated, targeting organizations of all sizes across all …Download Whitepaper
  • Zero Trust Made Simple: Why it matters and how to get started

    Zero Trust Made Simple: Why it matters and how to get started

    Data breaches and cyberattacks are no longer limited to large, high-profile organizations.Download Whitepaper
  • Cloud Secure Edge: Remote access, better security

    Cloud Secure Edge: Remote access, better security

    ​SonicWall Cloud Secure Edge™ is a modern, cloud-native Security Service Edge (SSE) solution that addresses …Download Whitepaper
  • Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Insider threats continue to be a major cybersecurity risk in 2024. Explore more insights on …Download Whitepaper

Middle-sidebar-banner

Case Studies

  • FOMO Pay expands cross-border compliance infrastructure amid rising fraud risks

    FOMO Pay expands cross-border compliance infrastructure amid rising fraud risks

    To unify onboarding and ongoing reviews the payment firm adds identity, liveness, business-ownership, sanctions screening …Read more
  • How a Vietnamese D2C retailer built its own secure digital infrastructure

    How a Vietnamese D2C retailer built its own secure digital infrastructure

    Would your organization build your own digital infrastructure – including AI governance and cybersecurity – …Read more
  • Cyber protection for medical clinics in Singapore

    Cyber protection for medical clinics in Singapore

    As Singapore’s healthcare sector becomes increasingly digital and interconnected, clinics are facing heightened cyber risks, …Read more
  • India’s WazirX strengthens governance and digital asset security

    India’s WazirX strengthens governance and digital asset security

    Revamping its custody infrastructure using multi‑party computation tools has improved operational resilience and institutional‑grade safeguardsRead more

Bottom sidebar

Other News

  • As Hijacked Billboards Make Headlines, CAYIN SMP Players Keep Screens in Owners’ Hands

    Monday, November 16, 2026
    After a run of hijacked …Read More »
  • Cohesity Expands Cyber Resilience and AI Data Capabilities for Microsoft Environments

    Friday, November 13, 2026
    Recent innovations strengthen data security …Read More »
  • Cequence Security and KPMG Collaborate on Joint Report Examining how Organisations can Govern and Secure Agentic AI

    Wednesday, November 11, 2026
    New Cequence data in the …Read More »
  • AJCCA Advances Trusted Cybersecurity at 3rd Annual Conference in Bangkok, Honors ACRA 2026 Awardees and Expands Regional Partnerships

    Tuesday, November 10, 2026
    Conference addresses emerging challenges in …Read More »
  • China Resources Longdation’s Aethereal Cybersecurity and GCSA Jointly Establish the Centre for AI and Cybersecurity Research

    Friday, November 6, 2026
    HONG KONG, Nov. 6, 2026 …Read More »
  • Our Brands
  • DigiconAsia
  • MartechAsia
  • Home
  • About Us
  • Contact Us
  • Sitemap
  • Privacy & Cookies
  • Terms of Use
  • Advertising & Reprint Policy
  • Media Kit
  • Subscribe
  • Manage Subscriptions
  • Newsletter

Copyright © 2026 CybersecAsia All Rights Reserved.