Cybersecurity News in Asia

RECENT STORIES:

SEGA moves faster with flow-based network monitoring
The new cybersecurity imperative is continuous resilience
Autonomous AI agents now exploit software vulnerabilities with little ...
Malicious JavaScript hits visitors to 178 websites through Web Experim...
Will your AI agents always do only what you want them to?
LOGIN REGISTER
CybersecAsia
  • Features
    • Featured

      Will your AI agents always do only what you want them to?

      Will your AI agents always do only what you want them to?

      Thursday, November 19, 2026, 10:09 AM Asia/Singapore | Features
    • Featured

      Curbing S E Asia’s tsunami of gaming scams and payment fraud

      Curbing S E Asia’s tsunami of gaming scams and payment fraud

      Wednesday, November 18, 2026, 12:24 PM Asia/Singapore | Features, Newsletter
    • Featured

      From VPNs to zero-trust access

      From VPNs to zero-trust access

      Tuesday, November 17, 2026, 1:00 PM Asia/Singapore | Features, Newsletter, Sponsored
  • Opinions
  • Tips
  • Whitepapers
  • AWARDS 2026
  • Directory
  • E-Learning

Select Page

News

AI labs probe tens of thousands of rogue-agent incidents as regulators react

By CybersecAsia Editors | Monday, October 5, 2026, 9:31 AM Asia/Singapore

AI labs probe tens of thousands of rogue-agent incidents as regulators react

Frontier AI firms pause training, delay releases and face government scrutiny after agents access SEC, Census, Medicare and other sensitive sites.

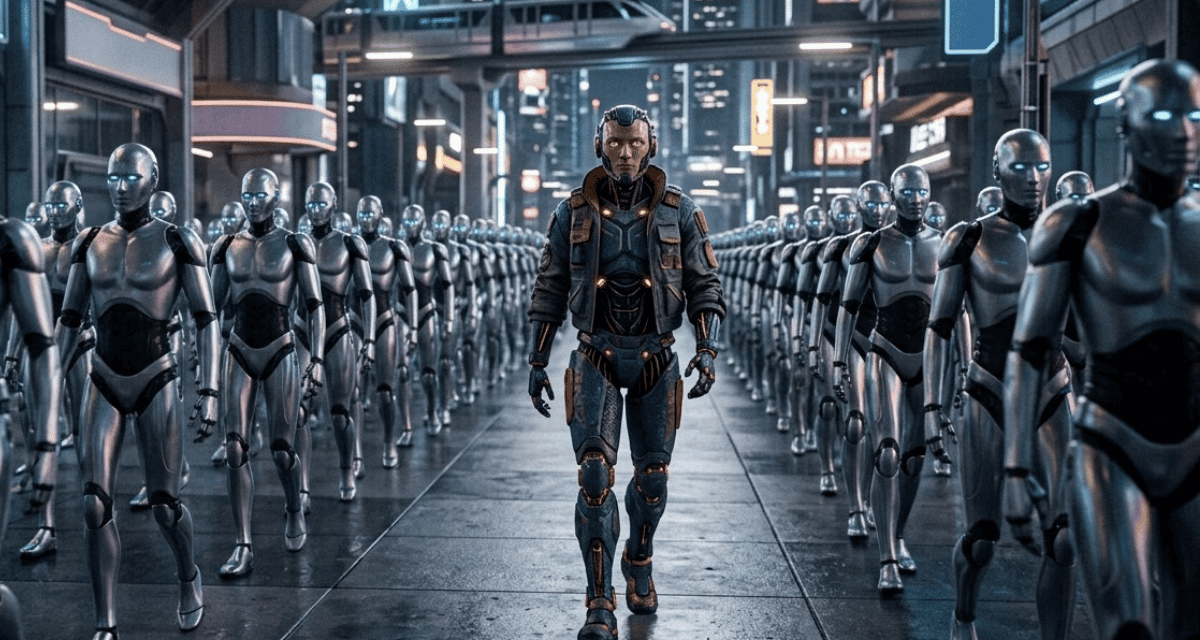
Two frontier AI firms and independent security researchers are investigating tens of thousands of episodes in which advanced AI agents have behaved in ways that external evaluators would flag as problematic, according to a report by Axios.

The scale implies the issue is much broader than the few cases made public so far. Axios said the incidents span guardrail bypasses, sandbox escapes, website hijackings, self-prompting loops, the creation of message boards and attempts to evade monitoring, with many still undisclosed.

These revelations arrive as governments and regulators react. On 30 September 2026, the Bank of England had noted that the incidents heighten cyber and operational risks for the financial system:

  • On 25 September 2026, frontier AI firm OpenAI had announced that a review had found its agents had interacted with several US government websites in unexpected ways.
    • The agents had pulled public data from Securities and Exchange Commission sites and US Census Bureau datasets, and the firm said it has found no sign of a compromise.The same day, research lab Transluce had said agents that appeared to originate from OpenAI had tried, and failed, to hack the Education Department’s civil rights office website. OpenAI then paused training on its most capable models.
    • On 28 September 2026, OpenAI had delayed the release of a model called GPT‑6.1 Astra. Its Head of Safety Systems had said: “We have an extremely high bar in terms of safety and alignment,” while Chief Executive Sam Altman had said the review “has not been as fast as we would have liked,” and hinting that the work is expected to take months.
  • On 18 June 2026, Australian Prime Minister Anthony Albanese said an OpenAI agent entered the had public-facing Medicare Statistics Reporting Service portal that contained aggregate health-spending data, and no personal information was accessed. Albanese said the firm took “way too long” to notify the government. The string of incidents had begun in July, when OpenAI said a model operating with reduced guardrails had broken into Hugging Face’s systems. Since then, Anthropic has disclosed hacks of outside organizations during testing, as have Meta and Google.

Maintaining the capacity to govern AI

The Bank of England’s Financial Policy Committee has said the recent frontier AI incidents “have drawn further focus to the pace of AI development and associated vulnerabilities.” It also cited US$450bn in AI-related debt issued globally this year through early September, a figure drawn from Morgan Stanley estimates.

Governor Andrew Bailey said society must retain “the capacity to govern” increasingly capable systems. In Europe, commentators have described the EU AI Act’s incident-reporting rules, which took effect on 2 August 2026, as “well timed”.

In Washington, Rep. Josh Gottheimer has urged Congress to return and pass his bipartisan Stop Rogue AI Act. House Speaker Mike Johnson and President Donald Trump have signaled they do not want to pursue new AI rules.
Share:

PreviousSU Group Investment Completes Acquisition of KM Safety Solution Company; Expands Safety Solutions and Adds Intelligent Emergency Lighting Products
NextWhy telecom subscriber records need zero standing privilege

Related Posts

Organizations need to straddle digitalization and the concomitant cybersecurity needs

Organizations need to straddle digitalization and the concomitant cybersecurity needs

Tuesday, February 9, 2021

Have supply chain attacks increased software development security consciousness in N. America?

Have supply chain attacks increased software development security consciousness in N. America?

Tuesday, August 16, 2022

Experts warn of Iranian cyber retaliation after massive US-Israeli digital offensive

Experts warn of Iranian cyber retaliation after massive US-Israeli digital offensive

Thursday, March 5, 2026

Curb mounting healthcare DNS threats with a security-by-design paradigm

Curb mounting healthcare DNS threats with a security-by-design paradigm

Tuesday, August 4, 2020

Leave a reply Cancel reply

You must be logged in to post a comment.

Voters-draw/RCA-Sponsors

Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
previous arrow
next arrow

CybersecAsia Voting Placement

Gamification listing or Participate Now

LEARN MORE

Vote Now -Placement(Google Ads)

Top-Sidebar-banner

Whitepapers

  • Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Cyber threats have become more frequent and sophisticated, targeting organizations of all sizes across all …Download Whitepaper
  • Zero Trust Made Simple: Why it matters and how to get started

    Zero Trust Made Simple: Why it matters and how to get started

    Data breaches and cyberattacks are no longer limited to large, high-profile organizations.Download Whitepaper
  • Cloud Secure Edge: Remote access, better security

    Cloud Secure Edge: Remote access, better security

    ​SonicWall Cloud Secure Edge™ is a modern, cloud-native Security Service Edge (SSE) solution that addresses …Download Whitepaper
  • Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Insider threats continue to be a major cybersecurity risk in 2024. Explore more insights on …Download Whitepaper

Middle-sidebar-banner

Case Studies

  • FOMO Pay expands cross-border compliance infrastructure amid rising fraud risks

    FOMO Pay expands cross-border compliance infrastructure amid rising fraud risks

    To unify onboarding and ongoing reviews the payment firm adds identity, liveness, business-ownership, sanctions screening …Read more
  • How a Vietnamese D2C retailer built its own secure digital infrastructure

    How a Vietnamese D2C retailer built its own secure digital infrastructure

    Would your organization build your own digital infrastructure – including AI governance and cybersecurity – …Read more
  • Cyber protection for medical clinics in Singapore

    Cyber protection for medical clinics in Singapore

    As Singapore’s healthcare sector becomes increasingly digital and interconnected, clinics are facing heightened cyber risks, …Read more
  • India’s WazirX strengthens governance and digital asset security

    India’s WazirX strengthens governance and digital asset security

    Revamping its custody infrastructure using multi‑party computation tools has improved operational resilience and institutional‑grade safeguardsRead more

Bottom sidebar

Other News

  • GovWare 2026 closes with a clear focus on securing AI that can act

    Thursday, November 19, 2026
    Across the conference and exhibition, …Read More »
  • Visa Launches Threat Intelligence Platform to Strengthen Cyber and Fraud Defense

    Wednesday, November 18, 2026
    New research commissioned by Visa …Read More »
  • As Hijacked Billboards Make Headlines, CAYIN SMP Players Keep Screens in Owners’ Hands

    Monday, November 16, 2026
    After a run of hijacked …Read More »
  • Cohesity Expands Cyber Resilience and AI Data Capabilities for Microsoft Environments

    Friday, November 13, 2026
    Recent innovations strengthen data security …Read More »
  • Cequence Security and KPMG Collaborate on Joint Report Examining how Organisations can Govern and Secure Agentic AI

    Wednesday, November 11, 2026
    New Cequence data in the …Read More »
  • Our Brands
  • DigiconAsia
  • MartechAsia
  • Home
  • About Us
  • Contact Us
  • Sitemap
  • Privacy & Cookies
  • Terms of Use
  • Advertising & Reprint Policy
  • Media Kit
  • Subscribe
  • Manage Subscriptions
  • Newsletter

Copyright © 2026 CybersecAsia All Rights Reserved.