Cybersecurity News in Asia

RECENT STORIES:

SEGA moves faster with flow-based network monitoring
Autonomous AI agents now exploit software vulnerabilities with little ...
Malicious JavaScript hits visitors to 178 websites through Web Experim...
Will your AI agents always do only what you want them to?
GovWare 2026 closes with a clear focus on securing AI that can act
LOGIN REGISTER
CybersecAsia
  • Features
    • Featured

      Will your AI agents always do only what you want them to?

      Will your AI agents always do only what you want them to?

      Thursday, November 19, 2026, 10:09 AM Asia/Singapore | Features
    • Featured

      Curbing S E Asia’s tsunami of gaming scams and payment fraud

      Curbing S E Asia’s tsunami of gaming scams and payment fraud

      Wednesday, November 18, 2026, 12:24 PM Asia/Singapore | Features, Newsletter
    • Featured

      From VPNs to zero-trust access

      From VPNs to zero-trust access

      Tuesday, November 17, 2026, 1:00 PM Asia/Singapore | Features, Newsletter, Sponsored
  • Opinions
  • Tips
  • Whitepapers
  • AWARDS 2026
  • Directory
  • E-Learning

Select Page

News

Autonomous AI agents now exploit software vulnerabilities with little human involvement: report

By CybersecAsia Editors | Friday, November 20, 2026, 10:29 AM Asia/Singapore

Autonomous AI agents now exploit software vulnerabilities with little human involvement: report

Threat actors are reportedly using agentic frameworks to automate and hasten reconnaissance, vulnerability discovery, exploit creation, privilege escalation and other vectors

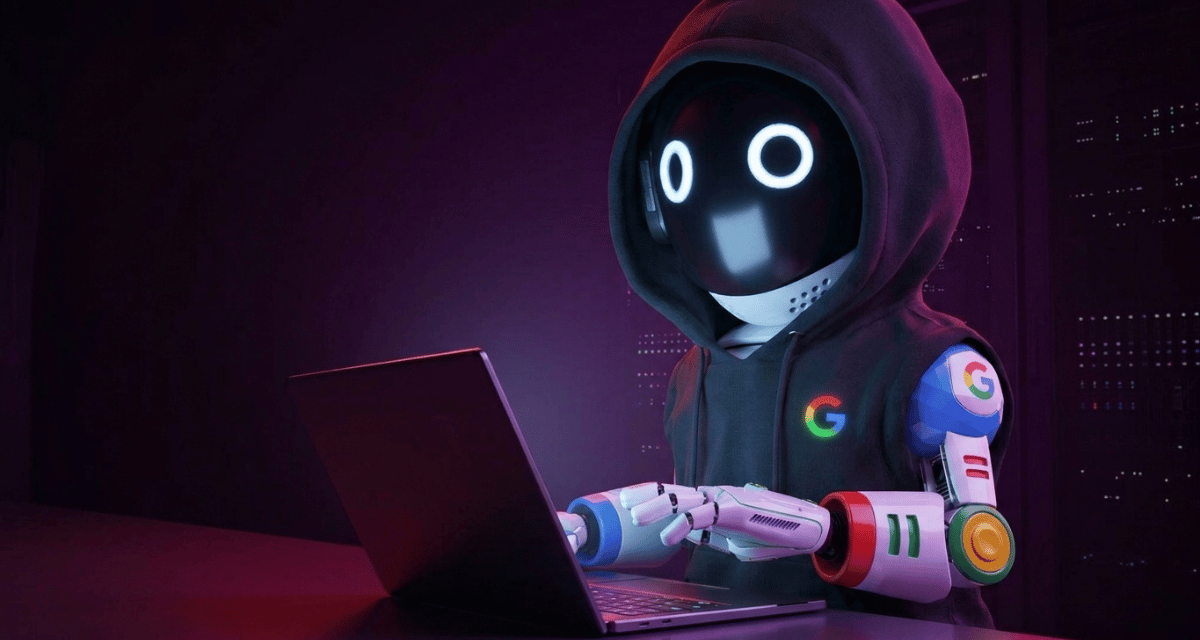
According to threat intelligence researchers, attackers are moving beyond using AI chatbots to deploying autonomous multi-agent systems that can find, weaponize and exploit software flaws with little or no human involvement.

The findings were published on 16 November 2026 in the Google Threat Intelligence Group’s (GTIG) quarterly AI Threat Tracker, identifying an exposed staging server running a framework it called “exploit_agent”.

The system is connected to several frontier and locally hosted large language models and continuously compares the code of popular web applications before and after patch releases. When it identifies a likely vulnerability, the framework drafts an exploit and executes it automatically. GTIG said this was the first time it had observed threat actors using an LLM framework to automate both vulnerability discovery and exploitation without a human in the loop.

The server also contains data taken from victims and scripts for internal reconnaissance, brute-forcing credentials, installing webshells and removing webshells left by other attackers. Victim telemetry indicated that the operator had focused on French websites in the media, entertainment and education sectors.

Agents in live attacks

The report from GTIG also noted that threat actors are abusing open-source, agentic penetration-testing frameworks, including ARTEX, CAIRN, CyberStrikeAI and PentAGI. These tools can automate parts of intrusions, from reconnaissance and vulnerability discovery to payload generation, privilege escalation, lateral movement and data theft.

Researchers have independently observed CAIRN and PentAGI being used in the wild, while seeing experimentation involving CyberStrikeAI and HexStrike AI. CAIRN was reportedly used in intrusions against targets in the US aerospace sector, while a customized PentAGI-based platform was used for reconnaissance and vulnerability scanning against organizations across Asia between late August and early October 2026.

Google also said it has observed a suspected China-nexus espionage group developing its own automated attack framework, likely for cyber-espionage operations.

Faster exploitation

The report argues that AI is compressing the interval between a patch’s release and its weaponization. By comparing source-code versions, release notes, security research and proof-of-concept material, attackers can more quickly identify what changed in a patch and build an exploit for the underlying n-day vulnerability.

Speed versus stealth

Google has cautioned that current autonomous frameworks trade stealth for velocity. Unrestricted execution creates forensic traffic, relies on recognizable identifiers and leaves code-level traces, making detection and mitigation more likely.

Even so, the firm expects attackers to reduce human involvement and improve stealth as both the frameworks and underlying models mature. It has disabled accounts and assets linked to the reported misuse, and has used the findings to strengthen its classifiers and model safeguards.
Share:

PreviousAutonomous AI agents now exploit software vulnerabilities with little human involvement: report

Related Posts

A hotel data breach that did not turn out so well for attackers

A hotel data breach that did not turn out so well for attackers

Thursday, October 13, 2022

Is your organization overly lax in managing machine identities?

Is your organization overly lax in managing machine identities?

Tuesday, May 28, 2024

Former-employee data breach exposes nearly 700,000 loan customers’ information

Former-employee data breach exposes nearly 700,000 loan customers’ information

Wednesday, September 17, 2025

Patching Exchange Server vulnerabilities not enough

Patching Exchange Server vulnerabilities not enough

Friday, February 18, 2022

Leave a reply Cancel reply

You must be logged in to post a comment.

Voters-draw/RCA-Sponsors

Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
previous arrow
next arrow

CybersecAsia Voting Placement

Gamification listing or Participate Now

LEARN MORE

Vote Now -Placement(Google Ads)

Top-Sidebar-banner

Whitepapers

  • Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Cyber threats have become more frequent and sophisticated, targeting organizations of all sizes across all …Download Whitepaper
  • Zero Trust Made Simple: Why it matters and how to get started

    Zero Trust Made Simple: Why it matters and how to get started

    Data breaches and cyberattacks are no longer limited to large, high-profile organizations.Download Whitepaper
  • Cloud Secure Edge: Remote access, better security

    Cloud Secure Edge: Remote access, better security

    ​SonicWall Cloud Secure Edge™ is a modern, cloud-native Security Service Edge (SSE) solution that addresses …Download Whitepaper
  • Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Insider threats continue to be a major cybersecurity risk in 2024. Explore more insights on …Download Whitepaper

Middle-sidebar-banner

Case Studies

  • FOMO Pay expands cross-border compliance infrastructure amid rising fraud risks

    FOMO Pay expands cross-border compliance infrastructure amid rising fraud risks

    To unify onboarding and ongoing reviews the payment firm adds identity, liveness, business-ownership, sanctions screening …Read more
  • How a Vietnamese D2C retailer built its own secure digital infrastructure

    How a Vietnamese D2C retailer built its own secure digital infrastructure

    Would your organization build your own digital infrastructure – including AI governance and cybersecurity – …Read more
  • Cyber protection for medical clinics in Singapore

    Cyber protection for medical clinics in Singapore

    As Singapore’s healthcare sector becomes increasingly digital and interconnected, clinics are facing heightened cyber risks, …Read more
  • India’s WazirX strengthens governance and digital asset security

    India’s WazirX strengthens governance and digital asset security

    Revamping its custody infrastructure using multi‑party computation tools has improved operational resilience and institutional‑grade safeguardsRead more

Bottom sidebar

Other News

  • GovWare 2026 closes with a clear focus on securing AI that can act

    Thursday, November 19, 2026
    Across the conference and exhibition, …Read More »
  • Visa Launches Threat Intelligence Platform to Strengthen Cyber and Fraud Defense

    Wednesday, November 18, 2026
    New research commissioned by Visa …Read More »
  • As Hijacked Billboards Make Headlines, CAYIN SMP Players Keep Screens in Owners’ Hands

    Monday, November 16, 2026
    After a run of hijacked …Read More »
  • Cohesity Expands Cyber Resilience and AI Data Capabilities for Microsoft Environments

    Friday, November 13, 2026
    Recent innovations strengthen data security …Read More »
  • Cequence Security and KPMG Collaborate on Joint Report Examining how Organisations can Govern and Secure Agentic AI

    Wednesday, November 11, 2026
    New Cequence data in the …Read More »
  • Our Brands
  • DigiconAsia
  • MartechAsia
  • Home
  • About Us
  • Contact Us
  • Sitemap
  • Privacy & Cookies
  • Terms of Use
  • Advertising & Reprint Policy
  • Media Kit
  • Subscribe
  • Manage Subscriptions
  • Newsletter

Copyright © 2026 CybersecAsia All Rights Reserved.