Cybersecurity News in Asia

RECENT STORIES:

SEGA moves faster with flow-based network monitoring
Agentic AI opportunities and risks for digital assets
AI agents increasingly perform consequential actions on customer-facin...
Cohesity Expands Cyber Resilience and AI Data Capabilities for Microso...
More IoT-refrigeration attacks predicted if cybersecurity weaknesses a...
Cequence Security and KPMG Collaborate on Joint Report Examining how O...
LOGIN REGISTER
CybersecAsia
  • Features
    • Featured

      Agentic AI opportunities and risks for digital assets

      Agentic AI opportunities and risks for digital assets

      Friday, November 13, 2026, 4:00 PM Asia/Singapore | Features, Newsletter
    • Featured

      The real cyberthreat frontier AI poses

      The real cyberthreat frontier AI poses

      Wednesday, November 4, 2026, 10:31 AM Asia/Singapore | Features
    • Featured

      Lessons from the Binance hack

      Lessons from the Binance hack

      Tuesday, November 3, 2026, 1:20 PM Asia/Singapore | Features, Opinions
  • Opinions
  • Tips
  • Whitepapers
  • AWARDS 2026
  • Directory
  • E-Learning

Select Page

News

Emergency updates fix CoreGraphics zero day linked to targeted zero click attacks

By CybersecAsia Editors | Wednesday, September 30, 2026, 11:39 AM Asia/Singapore

Emergency updates fix CoreGraphics zero day linked to targeted zero click attacks

An out-of-bounds write flaw in iOS/iPadOS/macOS requires urgent patching; the attack method and number of people affected remain undisclosed

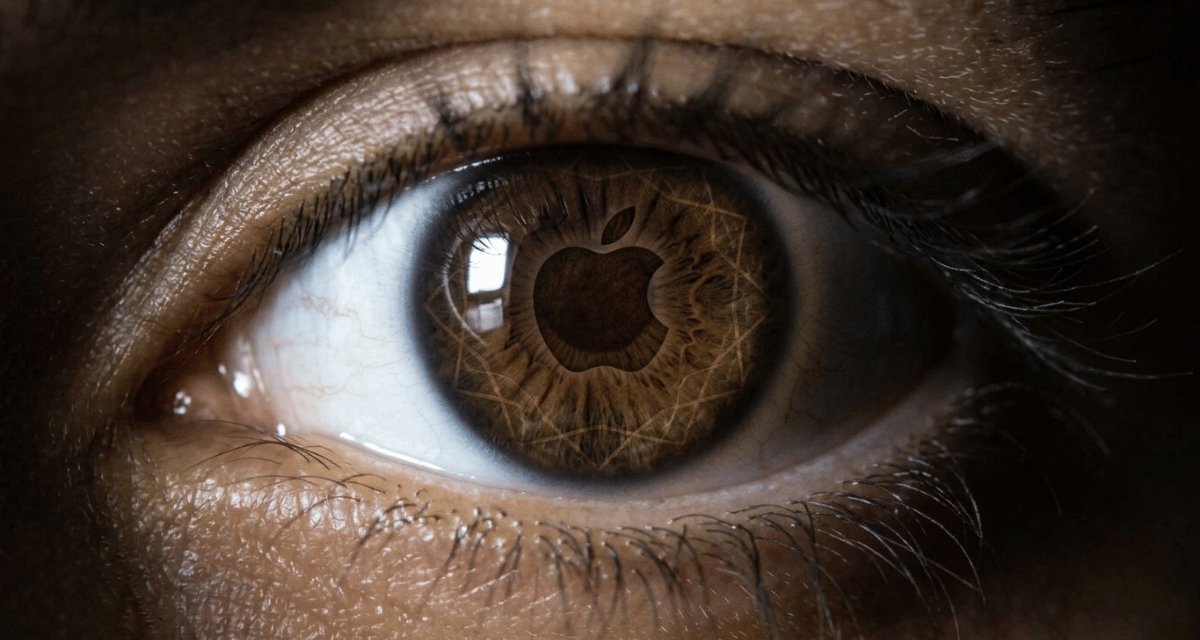
On 29 September 2026, Apple released emergency security updates to fix a zero day vulnerability in its CoreGraphics framework that may have been exploited in an “extremely sophisticated attack against specific targeted individuals” using older versions of iOS.

The flaw, tracked as CVE-2026-86950, is an out-of-bounds write bug that could allow arbitrary code execution when a device processes a maliciously crafted file. The issue has been addressed with improved bounds checking in iOS 26.7.1, iPadOS 26.7.1, macOS Tahoe 26.7.1, and macOS Sequoia 15.8.1. The firm’s newest operating systems — iOS 27, iPadOS 27, and macOS Golden Gate 27 — do not appear to be vulnerable to the flaw.

The vulnerability, reported by Meta Product Security, has drawn attention given a similar chain of events last year. In 2025, WhatsApp had disclosed that a vulnerability in its iOS and macOS apps (CVE-2025-55177) was likely used alongside an Apple ImageIO zero day in zero-click attacks targeting fewer than 200 users. It remains unclear whether the newly patched CoreGraphics flaw was exploited through WhatsApp or another vector.

Because CoreGraphics handles 2D graphics and PDF rendering across the operating system, a malicious file could arrive via web pages, email attachments, or messaging apps where automatic previews could enable zero-click exploitation. Apple has not disclosed how many individuals have been targeted; whether any attacks succeeded; or when exploitation first occurred, according to news sources.

Links to previous sophisticated attacks?

CVE-2026-86950 is the second zero day Apple has patched this year that was linked to “extremely sophisticated” targeted attacks. In February this year, the firm had fixed CVE-2026-20700, a memory corruption issue in the dynamic linker in macOS and iOS. The disclosure also follows a September report from the SHARE Foundation, a Serbian civil society organisation, which had found that at least 14 people in Serbia had been targeted with Pegasus spyware since the beginning of 2026 using zero-click exploits.

Apple has not drawn a direct connection between those attacks and CVE-2026-86950. CISA has yet to add the vulnerability to its Known Exploited Vulnerabilities catalog. The firm has urged all users to install the updates promptly.

CoreGraphics presents an attractive attack surface because it is invoked automatically in many common scenarios, from opening a message preview in WhatsApp to viewing a document attachment in Mail. The fact that Meta’s security team identified the issue suggests that the firm’s internal telemetry or threat intelligence may have detected anomalous behavior consistent with exploitation attempts, although neither Apple nor Meta has provided specifics on the attribution or the identity of the threat actor.

Enterprise and high-risk users have been advised to maintain up-to-date devices even when the perceived threat appears limited to a small number of individuals. Apple’s decision to backport the fix to older operating system versions indicates that the vulnerability affects a broad swath of the installed base, and the characterisation of the flaw exploitation as “extremely sophisticated” suggests capabilities typically associated with well-resourced adversaries.

Organisations should verify that all managed devices are running the latest available security updates and consider additional mitigations such as Lockdown Mode for users that may be at elevated risk of targeted cyberattacks.
Share:

PreviousSU Group Narrows First-Half Operating Loss, Executes on Long-Term Strategy
NextAutonomous agents flood UN website with thousands of data requests

Related Posts

Elevation of Privilege was 2022’s #1 vulnerability in Microsoft products

Elevation of Privilege was 2022’s #1 vulnerability in Microsoft products

Monday, March 27, 2023

McAfee: cloud-native breaches differ greatly from malware attacks of the past

McAfee: cloud-native breaches differ greatly from malware attacks of the past

Wednesday, September 25, 2019

Are SMEs in South-east Asia prone to paying off cyber ransoms?

Are SMEs in South-east Asia prone to paying off cyber ransoms?

Tuesday, August 16, 2022

Cyber readiness survey finds flat progress among respondents from 2023 to 2024

Cyber readiness survey finds flat progress among respondents from 2023 to 2024

Sunday, May 11, 2025

Leave a reply Cancel reply

You must be logged in to post a comment.

Voters-draw/RCA-Sponsors

Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
previous arrow
next arrow

CybersecAsia Voting Placement

Gamification listing or Participate Now

LEARN MORE

Vote Now -Placement(Google Ads)

Top-Sidebar-banner

Whitepapers

  • Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Cyber threats have become more frequent and sophisticated, targeting organizations of all sizes across all …Download Whitepaper
  • Zero Trust Made Simple: Why it matters and how to get started

    Zero Trust Made Simple: Why it matters and how to get started

    Data breaches and cyberattacks are no longer limited to large, high-profile organizations.Download Whitepaper
  • Cloud Secure Edge: Remote access, better security

    Cloud Secure Edge: Remote access, better security

    ​SonicWall Cloud Secure Edge™ is a modern, cloud-native Security Service Edge (SSE) solution that addresses …Download Whitepaper
  • Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Insider threats continue to be a major cybersecurity risk in 2024. Explore more insights on …Download Whitepaper

Middle-sidebar-banner

Case Studies

  • FOMO Pay expands cross-border compliance infrastructure amid rising fraud risks

    FOMO Pay expands cross-border compliance infrastructure amid rising fraud risks

    To unify onboarding and ongoing reviews the payment firm adds identity, liveness, business-ownership, sanctions screening …Read more
  • How a Vietnamese D2C retailer built its own secure digital infrastructure

    How a Vietnamese D2C retailer built its own secure digital infrastructure

    Would your organization build your own digital infrastructure – including AI governance and cybersecurity – …Read more
  • Cyber protection for medical clinics in Singapore

    Cyber protection for medical clinics in Singapore

    As Singapore’s healthcare sector becomes increasingly digital and interconnected, clinics are facing heightened cyber risks, …Read more
  • India’s WazirX strengthens governance and digital asset security

    India’s WazirX strengthens governance and digital asset security

    Revamping its custody infrastructure using multi‑party computation tools has improved operational resilience and institutional‑grade safeguardsRead more

Bottom sidebar

Other News

  • Cohesity Expands Cyber Resilience and AI Data Capabilities for Microsoft Environments

    Friday, November 13, 2026
    Recent innovations strengthen data security …Read More »
  • Cequence Security and KPMG Collaborate on Joint Report Examining how Organisations can Govern and Secure Agentic AI

    Wednesday, November 11, 2026
    New Cequence data in the …Read More »
  • AJCCA Advances Trusted Cybersecurity at 3rd Annual Conference in Bangkok, Honors ACRA 2026 Awardees and Expands Regional Partnerships

    Tuesday, November 10, 2026
    Conference addresses emerging challenges in …Read More »
  • China Resources Longdation’s Aethereal Cybersecurity and GCSA Jointly Establish the Centre for AI and Cybersecurity Research

    Friday, November 6, 2026
    HONG KONG, Nov. 6, 2026 …Read More »
  • Global Times: China champions open AI co-op at Wuzhen Summit, calls for opposition to ‘digital iron curtains’

    Thursday, November 5, 2026
    BEIJING, Nov. 5, 2026 /PRNewswire/ …Read More »
  • Our Brands
  • DigiconAsia
  • MartechAsia
  • Home
  • About Us
  • Contact Us
  • Sitemap
  • Privacy & Cookies
  • Terms of Use
  • Advertising & Reprint Policy
  • Media Kit
  • Subscribe
  • Manage Subscriptions
  • Newsletter

Copyright © 2026 CybersecAsia All Rights Reserved.