Cybersecurity News in Asia

RECENT STORIES:

SEGA moves faster with flow-based network monitoring
FBI warning: Attackers increasingly use ARTEX AI framework to automate...
Hidden software bug of July 2026 blamed for global office software out...
As Hijacked Billboards Make Headlines, CAYIN SMP Players Keep Screens ...
Agentic AI opportunities and risks for digital assets
AI agents increasingly perform consequential actions on customer-facin...
LOGIN REGISTER
CybersecAsia
  • Features
    • Featured

      Agentic AI opportunities and risks for digital assets

      Agentic AI opportunities and risks for digital assets

      Friday, November 13, 2026, 4:00 PM Asia/Singapore | Features, Newsletter
    • Featured

      The real cyberthreat frontier AI poses

      The real cyberthreat frontier AI poses

      Wednesday, November 4, 2026, 10:31 AM Asia/Singapore | Features
    • Featured

      Lessons from the Binance hack

      Lessons from the Binance hack

      Tuesday, November 3, 2026, 1:20 PM Asia/Singapore | Features, Opinions
  • Opinions
  • Tips
  • Whitepapers
  • AWARDS 2026
  • Directory
  • E-Learning

Select Page

News

Hackers phish for cloud accounts and payment passkeys using executive impersonation, social media lures

By CybersecAsia editors | Tuesday, September 15, 2026, 9:59 AM Asia/Singapore

Hackers phish for cloud accounts and payment passkeys using executive impersonation, social media lures

The threat actors spoof executive leaders, seek fund transfers, capture credentials, and register authentication methods to exfiltrate sensitive data

Hackers have been abusing trusted services and social engineering to phish for cloud access keys: one sent more than 1m fraudulent emails seeking payments, while the other used passkey-themed lures to compromise cloud accounts and steal data.

The first operation had run from 3 August to 5 August 2026 and impersonated company CEOs in messages aimed at accounts-payable teams.

The attackers sought ACH transfers for a supposedly legitimate annual ServiceNow subscription. Their targets were primarily US organizations in IT services, consumer goods, real estate and discrete manufacturing.

The operators appear to have used generative AI to prepare recipient-specific templates and emails. The campaign had combined spoofed executive identities, trusted email infrastructure, fake invoices, vendor branding and fabricated approval threads. The messages used the names and email addresses of CEOs, CFOs and presidents, while lookalike domains included [service-nowinc[.]com] and [domainlify[.]net]

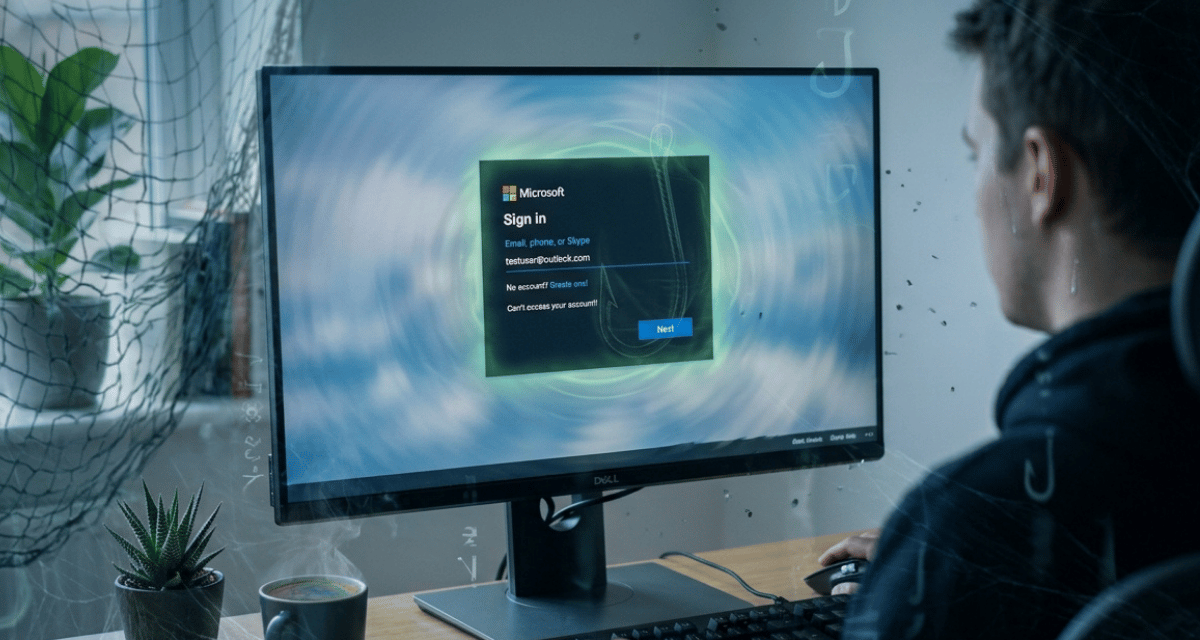
The second campaign, observed since May 2026, targeted Microsoft cloud identities. Attackers contacted employees through calls or text messages, posing as IT help-desk staff and claiming that users needed to update passkey, multifactor authentication or single sign-on settings to prevent service interruptions.

Victims were directed to counterfeit Microsoft sign-in pages and pushed through adversary-in-the-middle or device-code authentication flows. These methods could capture credentials or persuade users to authorize access without realizing it. The attackers also conducted extensive reconnaissance before targeting victims, using public information about employees and organizational structures. In some cases, compromised accounts were used to distribute similar messages through Microsoft Teams.

Threat groups linked to the heist

The threat actors registered domains themed around passkeys, identity verification and SSO enrollment, including:

  • passkeyhelpdesk[.]com]
  • [secure-passkey[.]com]
  • [setupmypasskey[.]com]
  • [add-passkey[.]com]
  • [integratedsso[.]com]
  • [oktasession[.]com]
  • [syncmykey[.]com]
  • [portalsetuphub[.]com]

Target-specific subdomains were used to make the sites appear more credible.

Microsoft has linked the activity to several threat groups, including Storm-3121 and Storm-3032, and said it overlaps with infrastructure associated with Cordial Spider, O-UNC-045, PREY-0058 and UNC6671.

After gaining access, attackers had attempted to establish persistence by registering their own phone number, authenticator app or software-based one-time-password token. They then used Microsoft Graph to map users, groups, permissions and services; searched mailboxes and attachments; downloaded data from SharePoint, OneDrive and Exchange; and maintained exfiltration for hours or days.

The attackers rotated infrastructure and IP addresses between authentication, reconnaissance and theft, making isolated indicators less useful.
Share:

PreviousFujitsu launches made-in-Japan next-generation CPU FUJITSU-MONAKA and Fujitsu MONAKA Server for sovereign AI infrastructure
NextASOCIO Digital & AI Summit 2026

Related Posts

The pivotal role of HR in cybersecurity

The pivotal role of HR in cybersecurity

Wednesday, November 11, 2020

Survey reveals C-level concerns over GenAI risks and staffing/cost challenges

Survey reveals C-level concerns over GenAI risks and staffing/cost challenges

Tuesday, March 4, 2025

Lazarus misuses legitimate security software in a supply-chain attack in South Korea

Lazarus misuses legitimate security software in a supply-chain attack in South Korea

Tuesday, November 17, 2020

What is the # 1 malware threat? _ _ _ som _ _ _ _!

What is the # 1 malware threat? _ _ _ som _ _ _ _!

Thursday, January 21, 2021

Leave a reply Cancel reply

You must be logged in to post a comment.

Voters-draw/RCA-Sponsors

Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
previous arrow
next arrow

CybersecAsia Voting Placement

Gamification listing or Participate Now

LEARN MORE

Vote Now -Placement(Google Ads)

Top-Sidebar-banner

Whitepapers

  • Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Cyber threats have become more frequent and sophisticated, targeting organizations of all sizes across all …Download Whitepaper
  • Zero Trust Made Simple: Why it matters and how to get started

    Zero Trust Made Simple: Why it matters and how to get started

    Data breaches and cyberattacks are no longer limited to large, high-profile organizations.Download Whitepaper
  • Cloud Secure Edge: Remote access, better security

    Cloud Secure Edge: Remote access, better security

    ​SonicWall Cloud Secure Edge™ is a modern, cloud-native Security Service Edge (SSE) solution that addresses …Download Whitepaper
  • Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Insider threats continue to be a major cybersecurity risk in 2024. Explore more insights on …Download Whitepaper

Middle-sidebar-banner

Case Studies

  • FOMO Pay expands cross-border compliance infrastructure amid rising fraud risks

    FOMO Pay expands cross-border compliance infrastructure amid rising fraud risks

    To unify onboarding and ongoing reviews the payment firm adds identity, liveness, business-ownership, sanctions screening …Read more
  • How a Vietnamese D2C retailer built its own secure digital infrastructure

    How a Vietnamese D2C retailer built its own secure digital infrastructure

    Would your organization build your own digital infrastructure – including AI governance and cybersecurity – …Read more
  • Cyber protection for medical clinics in Singapore

    Cyber protection for medical clinics in Singapore

    As Singapore’s healthcare sector becomes increasingly digital and interconnected, clinics are facing heightened cyber risks, …Read more
  • India’s WazirX strengthens governance and digital asset security

    India’s WazirX strengthens governance and digital asset security

    Revamping its custody infrastructure using multi‑party computation tools has improved operational resilience and institutional‑grade safeguardsRead more

Bottom sidebar

Other News

  • As Hijacked Billboards Make Headlines, CAYIN SMP Players Keep Screens in Owners’ Hands

    Monday, November 16, 2026
    After a run of hijacked …Read More »
  • Cohesity Expands Cyber Resilience and AI Data Capabilities for Microsoft Environments

    Friday, November 13, 2026
    Recent innovations strengthen data security …Read More »
  • Cequence Security and KPMG Collaborate on Joint Report Examining how Organisations can Govern and Secure Agentic AI

    Wednesday, November 11, 2026
    New Cequence data in the …Read More »
  • AJCCA Advances Trusted Cybersecurity at 3rd Annual Conference in Bangkok, Honors ACRA 2026 Awardees and Expands Regional Partnerships

    Tuesday, November 10, 2026
    Conference addresses emerging challenges in …Read More »
  • China Resources Longdation’s Aethereal Cybersecurity and GCSA Jointly Establish the Centre for AI and Cybersecurity Research

    Friday, November 6, 2026
    HONG KONG, Nov. 6, 2026 …Read More »
  • Our Brands
  • DigiconAsia
  • MartechAsia
  • Home
  • About Us
  • Contact Us
  • Sitemap
  • Privacy & Cookies
  • Terms of Use
  • Advertising & Reprint Policy
  • Media Kit
  • Subscribe
  • Manage Subscriptions
  • Newsletter

Copyright © 2026 CybersecAsia All Rights Reserved.