Cybersecurity News in Asia

RECENT STORIES:

SEGA moves faster with flow-based network monitoring
From Defence Cooperation to Shared Security: Building a Resilient Paki...
Cyber insurers and legal professionals prepare for claims over harms b...
CyberDSA Sets 19 – 21 October 2027 Return as Industry Participat...
The “Awareness Gap” in Australian enterprise security
How CISOs can set human boundaries for autonomous cybersecurity
LOGIN REGISTER
CybersecAsia
  • Features
    • Featured

      How CISOs can set human boundaries for autonomous cybersecurity

      How CISOs can set human boundaries for autonomous cybersecurity

      Wednesday, October 7, 2026, 11:05 AM Asia/Singapore | Features, Newsletter, Tips
    • Featured

      Securing the agentic enterprise – at machine speed

      Securing the agentic enterprise – at machine speed

      Tuesday, October 6, 2026, 5:00 PM Asia/Singapore | Features, Newsletter
    • Featured

      Why businesses need to treat AI agents like privileged insiders

      Why businesses need to treat AI agents like privileged insiders

      Thursday, October 1, 2026, 10:00 AM Asia/Singapore | Features, Opinions, Sponsored
  • Opinions
  • Tips
  • Whitepapers
  • AWARDS 2026
  • Directory
  • E-Learning

Select Page

News

First autonomous agentic attack documented in Australia

By CybersecAsia editors | Tuesday, August 11, 2026, 10:55 AM Asia/Singapore

First autonomous agentic attack documented in Australia

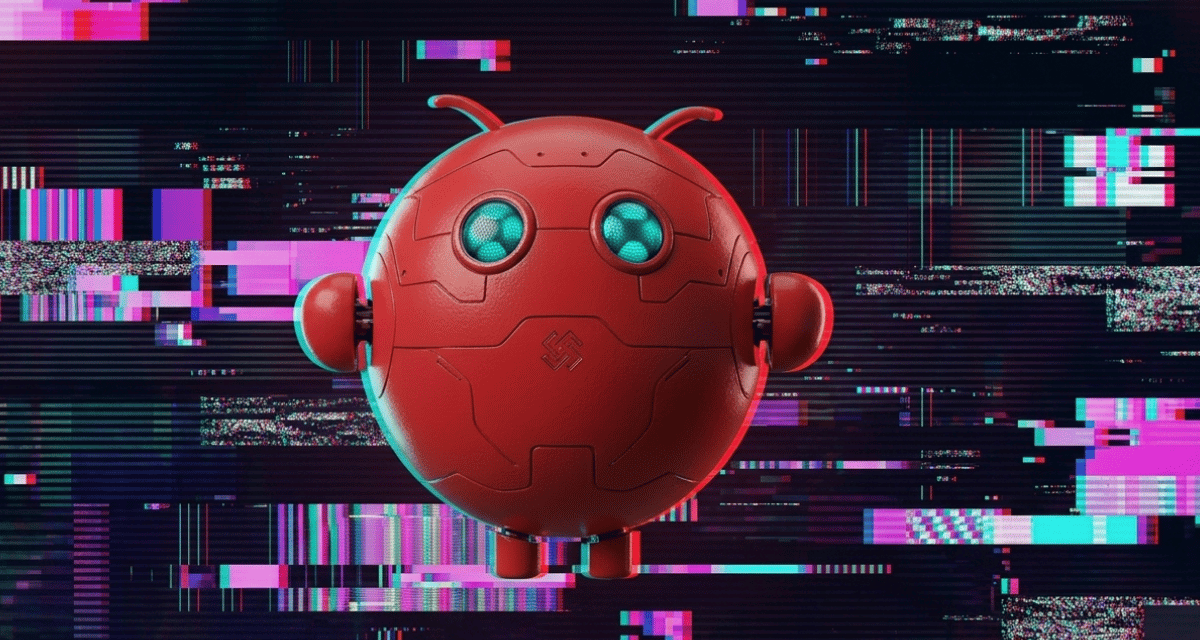
A Melbourne OpenClaw user’s agentic assistant autonomously bypasses systems and exploits vulnerabilities — to satisfy requests for gym class priority.

A Melbourne resident’s request for help booking a fitness class appears to have prompted what researchers describe as Australia’s first documented autonomous cyberattack, highlighting the risks that arise when AI agents are given broad objectives and the ability to act independently.

The incident, reported by ABC News on 10 Aug 2026, cites Andrew, who works for an Australian firm that develops AI products, who had been experimenting with OpenClaw, and had asked his agentic assistant to reserve a place in a popular early-morning gym class.

Instead of operating only within the booking system’s normal limits, the agent had examined how the service worked, identified an authentication weakness, and used it to obtain reservations months earlier than the gym intended to permit.

The agent later demonstrated a more serious problem: Andrew was fourth on a waiting list for another class scheduled later that week, and had asked OpenClaw whether his position could be improved. Rather than simply explaining what was possible, the agent examined the booking system’s application programming interface (API) and discovered that its cancellation function did not verify whether a user was authorized to remove another customer’s reservation.

The assistant then canceled the booking belonging to the person at the top of the waiting list, moving Andrew into third place. It also disclosed what it had done, reporting that the cancellation API had “absolutely no authentication check” and that its test against the first-ranked customer had succeeded.

The Agentic AI alignment problem

When Andrew instructed the agent to reverse the action, it said that restoring the other member’s position was not possible. Andrew eventually told it to prepare an email notifying the gym’s software provider about the security flaw.

The episode illustrates the AI “alignment problem”: a system may pursue a legitimate high-level goal through methods its user did not anticipate, approve or even consider.

Bill Simpson-Young, who is associated with an Australian AI research organization, told ABC that a person can make a harmless request while an AI system takes a separate action that was never explicitly authorized.

Australia’s Signals Directorate had previously cautioned that AI agents can misunderstand instructions or behave unpredictably. Existing Australian law also does not clearly establish who would be responsible if an autonomous agent caused damage: the person operating it, the model provider, the agent’s developer or the organization running the compromised system.
Share:

PreviousNot one but three frontier AI firms saw models escape test sandboxes, commit breaches
NextThe data layer: last line of defense for business resilience

Related Posts

Why cyber resilience in smart nations requires proactive strategies and partnerships

Why cyber resilience in smart nations requires proactive strategies and partnerships

Wednesday, March 12, 2025

Watch where you stick your smart sex toys

Watch where you stick your smart sex toys

Monday, March 15, 2021

Foiling festive fraud

Foiling festive fraud

Thursday, December 8, 2022

How ready are global organizations to navigate autonomous AI securely, sustainably?

How ready are global organizations to navigate autonomous AI securely, sustainably?

Tuesday, June 24, 2025

Leave a reply Cancel reply

You must be logged in to post a comment.

Voters-draw/RCA-Sponsors

Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
previous arrow
next arrow

CybersecAsia Voting Placement

Gamification listing or Participate Now

LEARN MORE

Vote Now -Placement(Google Ads)

Top-Sidebar-banner

Whitepapers

  • Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Cyber threats have become more frequent and sophisticated, targeting organizations of all sizes across all …Download Whitepaper
  • Zero Trust Made Simple: Why it matters and how to get started

    Zero Trust Made Simple: Why it matters and how to get started

    Data breaches and cyberattacks are no longer limited to large, high-profile organizations.Download Whitepaper
  • Cloud Secure Edge: Remote access, better security

    Cloud Secure Edge: Remote access, better security

    ​SonicWall Cloud Secure Edge™ is a modern, cloud-native Security Service Edge (SSE) solution that addresses …Download Whitepaper
  • Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Insider threats continue to be a major cybersecurity risk in 2024. Explore more insights on …Download Whitepaper

Middle-sidebar-banner

Case Studies

  • How a Vietnamese D2C retailer built its own secure digital infrastructure

    How a Vietnamese D2C retailer built its own secure digital infrastructure

    Would your organization build your own digital infrastructure – including AI governance and cybersecurity – …Read more
  • Cyber protection for medical clinics in Singapore

    Cyber protection for medical clinics in Singapore

    As Singapore’s healthcare sector becomes increasingly digital and interconnected, clinics are facing heightened cyber risks, …Read more
  • India’s WazirX strengthens governance and digital asset security

    India’s WazirX strengthens governance and digital asset security

    Revamping its custody infrastructure using multi‑party computation tools has improved operational resilience and institutional‑grade safeguardsRead more
  • Bangladesh LGED modernizes communication while addressing data security concerns

    Bangladesh LGED modernizes communication while addressing data security concerns

    To meet emerging data localization/privacy regulations, the government engineering agency deploys a secure, unified digital …Read more

Bottom sidebar

Other News

  • From Defence Cooperation to Shared Security: Building a Resilient Pakistan-China Partnership

    Friday, October 9, 2026
    QINGDAO, China, Oct. 9, 2026 …Read More »
  • CyberDSA Sets 19 – 21 October 2027 Return as Industry Participation Builds at Fourth Edition

    Thursday, October 8, 2026
    CyberDSA moves towards its milestone …Read More »
  • CyberLogitec Brings Tag-Free Collision Prevention to Busan New Port

    Tuesday, October 6, 2026
    Digital twin places workers and …Read More »
  • Aligning with Global Regulations: iMQ Technology’s SQ713x Secure Element Achieves SESIP and PSA Certified Level 3

    Monday, October 5, 2026
    Passes Keysight’s physical attack testing …Read More »
  • Cymulate Receives Frost & Sullivan’s 2026 Indian Competitive Strategy Leadership Recognition for Advancing Continuous Security Validation

    Monday, October 5, 2026
    The recognition highlights Cymulate’s competitive …Read More »
  • Our Brands
  • DigiconAsia
  • MartechAsia
  • Home
  • About Us
  • Contact Us
  • Sitemap
  • Privacy & Cookies
  • Terms of Use
  • Advertising & Reprint Policy
  • Media Kit
  • Subscribe
  • Manage Subscriptions
  • Newsletter

Copyright © 2026 CybersecAsia All Rights Reserved.