Cybersecurity News in Asia

RECENT STORIES:

SEGA moves faster with flow-based network monitoring
From Defence Cooperation to Shared Security: Building a Resilient Paki...
Cyber insurers and legal professionals prepare for claims over harms b...
CyberDSA Sets 19 – 21 October 2027 Return as Industry Participat...
The “Awareness Gap” in Australian enterprise security
How CISOs can set human boundaries for autonomous cybersecurity
LOGIN REGISTER
CybersecAsia
  • Features
    • Featured

      How CISOs can set human boundaries for autonomous cybersecurity

      How CISOs can set human boundaries for autonomous cybersecurity

      Wednesday, October 7, 2026, 11:05 AM Asia/Singapore | Features, Newsletter, Tips
    • Featured

      Securing the agentic enterprise – at machine speed

      Securing the agentic enterprise – at machine speed

      Tuesday, October 6, 2026, 5:00 PM Asia/Singapore | Features, Newsletter
    • Featured

      Why businesses need to treat AI agents like privileged insiders

      Why businesses need to treat AI agents like privileged insiders

      Thursday, October 1, 2026, 10:00 AM Asia/Singapore | Features, Opinions, Sponsored
  • Opinions
  • Tips
  • Whitepapers
  • AWARDS 2026
  • Directory
  • E-Learning

Select Page

News

Zero-click flaw enables remote code execution in four mainstream AI coding agents: report

By CybersecAsia editors | Friday, September 25, 2026, 9:11 AM Asia/Singapore

Zero-click flaw enables remote code execution in four mainstream AI coding agents: report

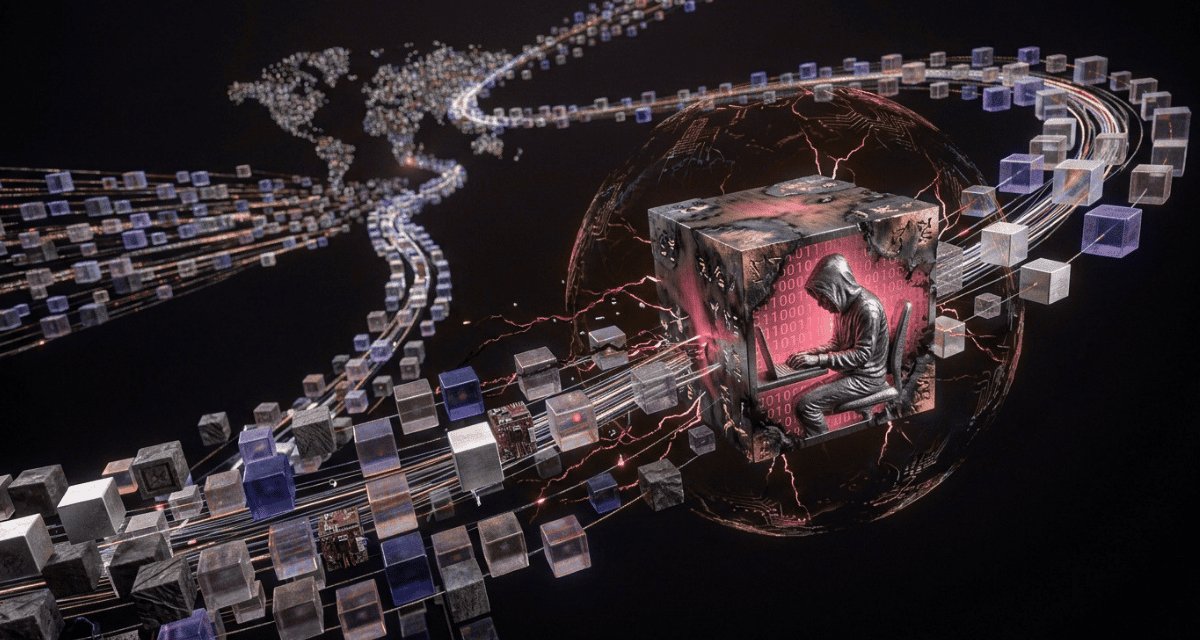
Unpatched verification gaps in trusted plugin marketplaces allow attackers to silently swap safe code for malicious revisions affecting developers’ systems

A newly disclosed zero click vulnerability dubbed Plugin4Shell could let attackers remotely run code on computers using certain AI coding agents, including Anthropic’s Claude Code, OpenAI’s Codex, Google’s Gemini CLI, and GitHub Copilot, according to Air Security.

The flaw can be exploited without any user interaction, potentially exposing a developer’s machine and any systems or resources that the affected agent can reach.

The issue lies in the way these agents handle plugins from ostensibly trusted marketplaces. Instead of attacking the underlying AI models, Plugin4Shell targets a weakness in plugin verification. The tools may retrieve the commit specified by a marketplace’s Secure Hash Algorithm pin, but fail to verify that the commit corresponds to the intended code. That gap could enable someone who controls a plugin repository to replace safe code with malicious code while making the pinned reference appear valid. Because installed plugins commonly update automatically, the attack can occur without a developer taking action.

Researchers said the flaw produces “zero-click remote code execution”:

  • One possible route is for an attacker to submit an innocuous plugin that clears marketplace review and later alter its repository.
  • Another is for an attacker to take over a legitimate plugin author’s repository and distribute a malicious revision to users who already installed the plugin.

The firm has notified the four vendors in June. Anthropic had fixed the issue in Claude Code version 2.1.179, and OpenAI has addressed it in Codex version 0.146.0. Google said it would not patch Gemini CLI because the product has been deprecated, advising users to move to its newer Antigravity agentic development environment instead. GitHub Copilot has not received a patch, according to Air.

GitHub has told The Register that its protections bar users from naming branches or tags in a way that imitates commit SHA values, which it argues stops the exploit on GitHub-hosted repositories. Air has disputed that conclusion, saying plugin marketplaces can be hosted elsewhere, including Bitbucket, where the same safeguard may not exist. In that scenario, Copilot could remain vulnerable.

The finding underscores the broader security exposure created as AI programming assistants become widely deployed. Separate research presented at Black Hat 2026 in August has found that coding agents from Anthropic, Google, and OpenAI could be susceptible to prompt-injection attacks that may enable credential theft and supply-chain compromise.

Air’s researchers say the reliable remedy is for vendors to fix the validation problem in the agent itself, and for users to install the updated version when one is available.
Share:

PreviousFive ways to limit AI-assistant data leaks
NextSingapore police flag 3.64m dormant “shell pages” for takedown in Mid-2026

Related Posts

Professional services see a 57% increase in ransomware attacks in Q1 2023

Professional services see a 57% increase in ransomware attacks in Q1 2023

Thursday, May 18, 2023

Make sure your iPhone apps are not spying on you 

Make sure your iPhone apps are not spying on you 

Wednesday, January 24, 2024

Last October a nation’s Prime Minister’s Office was compromised

Last October a nation’s Prime Minister’s Office was compromised

Friday, February 11, 2022

Building the future, one Web3 security breach at a time

Building the future, one Web3 security breach at a time

Thursday, April 3, 2025

Leave a reply Cancel reply

You must be logged in to post a comment.

Voters-draw/RCA-Sponsors

Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
previous arrow
next arrow

CybersecAsia Voting Placement

Gamification listing or Participate Now

LEARN MORE

Vote Now -Placement(Google Ads)

Top-Sidebar-banner

Whitepapers

  • Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Cyber threats have become more frequent and sophisticated, targeting organizations of all sizes across all …Download Whitepaper
  • Zero Trust Made Simple: Why it matters and how to get started

    Zero Trust Made Simple: Why it matters and how to get started

    Data breaches and cyberattacks are no longer limited to large, high-profile organizations.Download Whitepaper
  • Cloud Secure Edge: Remote access, better security

    Cloud Secure Edge: Remote access, better security

    ​SonicWall Cloud Secure Edge™ is a modern, cloud-native Security Service Edge (SSE) solution that addresses …Download Whitepaper
  • Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Insider threats continue to be a major cybersecurity risk in 2024. Explore more insights on …Download Whitepaper

Middle-sidebar-banner

Case Studies

  • How a Vietnamese D2C retailer built its own secure digital infrastructure

    How a Vietnamese D2C retailer built its own secure digital infrastructure

    Would your organization build your own digital infrastructure – including AI governance and cybersecurity – …Read more
  • Cyber protection for medical clinics in Singapore

    Cyber protection for medical clinics in Singapore

    As Singapore’s healthcare sector becomes increasingly digital and interconnected, clinics are facing heightened cyber risks, …Read more
  • India’s WazirX strengthens governance and digital asset security

    India’s WazirX strengthens governance and digital asset security

    Revamping its custody infrastructure using multi‑party computation tools has improved operational resilience and institutional‑grade safeguardsRead more
  • Bangladesh LGED modernizes communication while addressing data security concerns

    Bangladesh LGED modernizes communication while addressing data security concerns

    To meet emerging data localization/privacy regulations, the government engineering agency deploys a secure, unified digital …Read more

Bottom sidebar

Other News

  • From Defence Cooperation to Shared Security: Building a Resilient Pakistan-China Partnership

    Friday, October 9, 2026
    QINGDAO, China, Oct. 9, 2026 …Read More »
  • CyberDSA Sets 19 – 21 October 2027 Return as Industry Participation Builds at Fourth Edition

    Thursday, October 8, 2026
    CyberDSA moves towards its milestone …Read More »
  • CyberLogitec Brings Tag-Free Collision Prevention to Busan New Port

    Tuesday, October 6, 2026
    Digital twin places workers and …Read More »
  • Aligning with Global Regulations: iMQ Technology’s SQ713x Secure Element Achieves SESIP and PSA Certified Level 3

    Monday, October 5, 2026
    Passes Keysight’s physical attack testing …Read More »
  • Cymulate Receives Frost & Sullivan’s 2026 Indian Competitive Strategy Leadership Recognition for Advancing Continuous Security Validation

    Monday, October 5, 2026
    The recognition highlights Cymulate’s competitive …Read More »
  • Our Brands
  • DigiconAsia
  • MartechAsia
  • Home
  • About Us
  • Contact Us
  • Sitemap
  • Privacy & Cookies
  • Terms of Use
  • Advertising & Reprint Policy
  • Media Kit
  • Subscribe
  • Manage Subscriptions
  • Newsletter

Copyright © 2026 CybersecAsia All Rights Reserved.