Cybersecurity News in Asia

RECENT STORIES:

SEGA moves faster with flow-based network monitoring
Vendor data flags 36.4% of Asia Pacific login attempts as high or crit...
China Resources Longdation’s Aethereal Cybersecurity and GCSA Jo...
Global Times: China champions open AI co-op at Wuzhen Summit, calls fo...
Viettel Group and Vietnam’s Government Cipher Committee Unveil S...
87% See AI Vulnerabilities as the Fastest-Growing Risk
LOGIN REGISTER
CybersecAsia
  • Features
    • Featured

      The real cyberthreat frontier AI poses

      The real cyberthreat frontier AI poses

      Wednesday, November 4, 2026, 10:31 AM Asia/Singapore | Features
    • Featured

      Lessons from the Binance hack

      Lessons from the Binance hack

      Tuesday, November 3, 2026, 1:20 PM Asia/Singapore | Features, Opinions
    • Featured

      How social-engineered approvals are defeating hardware wallets

      How social-engineered approvals are defeating hardware wallets

      Thursday, October 29, 2026, 11:05 AM Asia/Singapore | Features
  • Opinions
  • Tips
  • Whitepapers
  • AWARDS 2026
  • Directory
  • E-Learning

Select Page

Features

Rethinking customer identity for financial cybersecurity

By Victor Ng | Tuesday, January 27, 2026, 4:13 PM Asia/Singapore

Rethinking customer identity for financial cybersecurity

What should banks in Asia Pacific pay attention to this year to protect themselves and their customers?

Financial institutions face an average of $6.08M per breach, 22% above the global average. What should banks and financial institutions do to protect themselves and their customers?

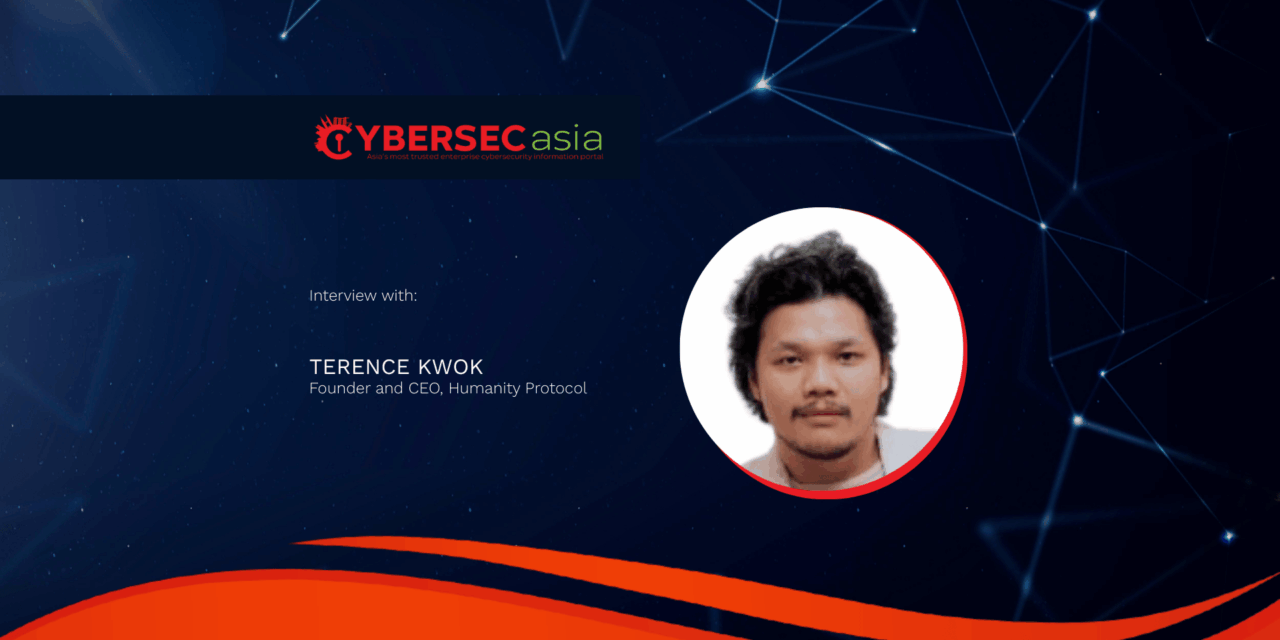
We find out more from Terence Kwok, Founder and CEO, Humanity Protocol, on how banks can materially reduce this exposure by rethinking customer identity.

Why are traditional KYC processes and centralized data stores still the weakest link for banks?

Kwok: Traditionally, KYC processes require banks to collect, duplicate, and store large volumes of sensitive identity data. This creates centralised repositories that remain attractive targets long after onboarding is complete. These data stores contain static information such as passports, ID documents, and proof of address, which attackers can easily monetise through identity theft or the creation of synthetic identities.

The issue is structural. Even when security controls improve, the underlying model still forces institutions to hold data that is no longer operationally necessary but still carries significant long-term liability. IBM’s recent breach analysis shows that most financial-sector breach impact comes from data at rest rather than data in transit. This exposes a fundamental mismatch. Verification is a single event, yet the associated custodial responsibility persists indefinitely.

As digital channels expand, centralised data stores become harder to secure and more costly to maintain. Banks inherit long-term risk simply by holding information that attackers actively seek. The system meets compliance requirements, but it enlarges the threat surface at the same time.

How does removing high-value data “honeypots” change the economics of a potential breach?

Kwok: When storage of sensitive information is eliminated, the financial and operational consequences of a breach change significantly. Breaches involving personal data trigger a long and expensive chain of remediation activities that include regulatory reporting, customer notification, identity restoration support, and reputational management. These costs often extend for years.

If verification is achieved through cryptographic proofs rather than stored documents, attackers have very little to gain. There are no passport scans, utility bills, or identification records to extract. Cyberattackers rely on concentrated, easily monetisable data sets. When those data sets no longer exist, the potential reward falls sharply.

This changes the nature of incidents. Breaches become operational disruptions rather than large-scale data exposure events. Institutions focus on restoring systems, not mitigating identity compromise. The overall cost profile becomes more predictable and far less severe. By removing high-value honeypots, organisations significantly reduce the economic incentive for attackers.

How can decentralized, privacy-preserving identity fit within today’s regulatory expectations for AML and KYC?

Kwok: Decentralized, privacy-preserving identity models can meet AML and KYC requirements by providing the assurance and auditability regulators expect without requiring institutions to store excess personal data. Regulators care about whether an institution can prove that a customer meets specific criteria. They do not require organisations to hold more information than is necessary to demonstrate compliance.

Using cryptographic verification methods such as or zkTLS (zero-knowledge transport layer security), institutions can validate attributes such as account ownership or eligibility against sanctions lists without accessing or storing the underlying documents. These verification steps can be logged, audited and reproduced, which preserves regulatory integrity.

This approach also aligns with a broader shift toward data minimisation in frameworks such as GDPR, MAS guidelines, PDPA, and new requirements across the Middle East and Asia Pacific. Many regulators are now encouraging institutions to reduce the amount of identity data they retain, as unnecessary storage is increasingly viewed as a security and compliance risk.

In practical terms, privacy-preserving identity models do not reduce oversight. They strengthen it by allowing institutions to verify what is required while avoiding the long-term custodial obligations that create unnecessary risk.
Share:

PreviousScammers abuse popular collaboration tools to send phishing emails
NextRegASK Achieves ISO 27701 Privacy Certification, Strengthening Verifiable Trust in the AI Era

Related Posts

Why APAC Teams Need to Stop Worshipping CVSS Scores

Why APAC Teams Need to Stop Worshipping CVSS Scores

Monday, August 3, 2026

Balancing the need for great digital experiences while keeping threats away

Balancing the need for great digital experiences while keeping threats away

Wednesday, March 10, 2021

The new CISO mandate: protect DevOps!

The new CISO mandate: protect DevOps!

Saturday, August 21, 2021

Why digital resilience pays off

Why digital resilience pays off

Tuesday, May 16, 2023

Leave a reply Cancel reply

You must be logged in to post a comment.

Voters-draw/RCA-Sponsors

Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
previous arrow
next arrow

CybersecAsia Voting Placement

Gamification listing or Participate Now

LEARN MORE

Vote Now -Placement(Google Ads)

Top-Sidebar-banner

Whitepapers

  • Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Cyber threats have become more frequent and sophisticated, targeting organizations of all sizes across all …Download Whitepaper
  • Zero Trust Made Simple: Why it matters and how to get started

    Zero Trust Made Simple: Why it matters and how to get started

    Data breaches and cyberattacks are no longer limited to large, high-profile organizations.Download Whitepaper
  • Cloud Secure Edge: Remote access, better security

    Cloud Secure Edge: Remote access, better security

    ​SonicWall Cloud Secure Edge™ is a modern, cloud-native Security Service Edge (SSE) solution that addresses …Download Whitepaper
  • Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Insider threats continue to be a major cybersecurity risk in 2024. Explore more insights on …Download Whitepaper

Middle-sidebar-banner

Case Studies

  • FOMO Pay expands cross-border compliance infrastructure amid rising fraud risks

    FOMO Pay expands cross-border compliance infrastructure amid rising fraud risks

    To unify onboarding and ongoing reviews the payment firm adds identity, liveness, business-ownership, sanctions screening …Read more
  • How a Vietnamese D2C retailer built its own secure digital infrastructure

    How a Vietnamese D2C retailer built its own secure digital infrastructure

    Would your organization build your own digital infrastructure – including AI governance and cybersecurity – …Read more
  • Cyber protection for medical clinics in Singapore

    Cyber protection for medical clinics in Singapore

    As Singapore’s healthcare sector becomes increasingly digital and interconnected, clinics are facing heightened cyber risks, …Read more
  • India’s WazirX strengthens governance and digital asset security

    India’s WazirX strengthens governance and digital asset security

    Revamping its custody infrastructure using multi‑party computation tools has improved operational resilience and institutional‑grade safeguardsRead more

Bottom sidebar

Other News

  • China Resources Longdation’s Aethereal Cybersecurity and GCSA Jointly Establish the Centre for AI and Cybersecurity Research

    Friday, November 6, 2026
    HONG KONG, Nov. 6, 2026 …Read More »
  • Global Times: China champions open AI co-op at Wuzhen Summit, calls for opposition to ‘digital iron curtains’

    Thursday, November 5, 2026
    BEIJING, Nov. 5, 2026 /PRNewswire/ …Read More »
  • Viettel Group and Vietnam’s Government Cipher Committee Unveil Security Chip Embedding Vietnamese Cryptography in Silicon

    Thursday, November 5, 2026
    HANOI, Vietnam, Nov. 4, 2026 …Read More »
  • 87% See AI Vulnerabilities as the Fastest-Growing Risk

    Thursday, November 5, 2026
    -AJCCA at the ASOCIO Digital & …Read More »
  • OID 2026: Advancing Technology Partnerships to Power the Next-Gen Industrial City

    Thursday, November 5, 2026
    HO CHI MINH CITY, Vietnam, …Read More »
  • Our Brands
  • DigiconAsia
  • MartechAsia
  • Home
  • About Us
  • Contact Us
  • Sitemap
  • Privacy & Cookies
  • Terms of Use
  • Advertising & Reprint Policy
  • Media Kit
  • Subscribe
  • Manage Subscriptions
  • Newsletter

Copyright © 2026 CybersecAsia All Rights Reserved.