Cybersecurity News in Asia

RECENT STORIES:

SEGA moves faster with flow-based network monitoring
More than 23,500 customers affected by SIMBA data breach
Cellid and Megane Top Partner to Commercialize and Expand the AR Glass...
ICAC and UNODC’s pioneering international anti-graft training br...
Singapore police flag 3.64m dormant “shell pages” for takedown in Mid-...
Zero-click flaw enables remote code execution in four mainstream AI co...
LOGIN REGISTER
CybersecAsia
  • Features
    • Featured

      Shadow AI Is the New Insider Threat

      Shadow AI Is the New Insider Threat

      Monday, September 21, 2026, 9:11 AM Asia/Singapore | Features, Newsletter, Sponsored, Tips
    • Featured

      Addressing the AI-driven vulnerability debt

      Addressing the AI-driven vulnerability debt

      Thursday, September 17, 2026, 10:03 AM Asia/Singapore | Features, Sponsored
    • Featured

      Cybercriminals zero In on APAC’s digital boom, SMBs in the crosshairs

      Cybercriminals zero In on APAC’s digital boom, SMBs in the crosshairs

      Monday, September 14, 2026, 2:30 PM Asia/Singapore | Features, Sponsored
  • Opinions
  • Tips
  • Whitepapers
  • AWARDS 2026
  • Directory
  • E-Learning

Select Page

News

Can your anti-phishing software detect these new URLO obfuscation techniques?

By CybersecAsia editors | Friday, September 12, 2025, 8:33 AM Asia/Singapore

Can your anti-phishing software detect these new URLO obfuscation techniques?

Cybercriminals are employing novel ways such as invisible spaces and confusing URLs to foil email scanning software and wary users.

Phishing emails and social media posts often contain harmful links that direct victims to fake websites where they could be tricked into downloading malware or reveal personal information such as login IDs and passwords.

As security systems become better at spotting these malicious links, cybercriminals are developing crafty new ways to hide them and slip past defenses unnoticed.

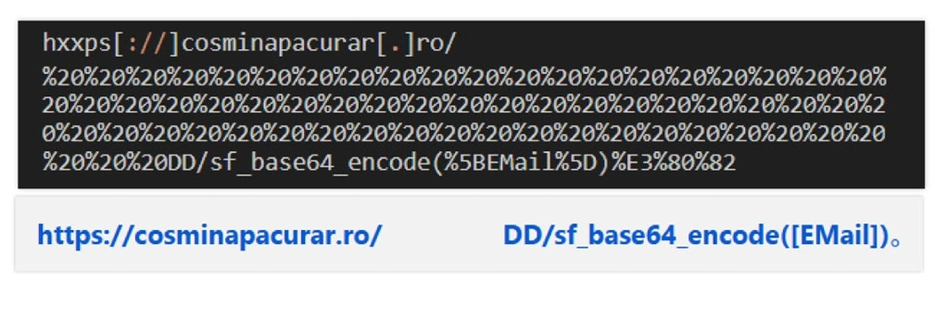
On 9 September 2025, one cybersecurity firm has shared some new findings about several clever tricks being used to obscure actual URLs. The methods are: Inserting invisible spaces (code %20) and unusual characters into web addresses, to push the malicious part of the link out of sight of security scanners or suspicious eyes. Attackers can also add fake elements such as a hidden email address or secret codes at the end of the links that can track victims or redirect them to malicious sites. To make their trap look more convincing, the attackers sometimes include fake verification tests such as CAPTCHA prompts that make the site appear legitimate.

  • Inserting invisible spaces (code %20) and unusual characters into web addresses, to push the malicious part of the link out of sight of security scanners or suspicious eyes. Attackers can also add fake elements such as a hidden email address or secret codes at the end of the links that can track victims or redirect them to malicious sites. To make their trap look more convincing, the attackers sometimes include fake verification tests such as CAPTCHA prompts that make the site appear legitimate.

    E.g.: A malicious URL padded with invisible spaces to be visually broken up into two parts that look harmless.
  • Using the Redundant Protocol Prefix technique to craft a URL that is only partially hyperlinked or that contains invalid elements (such as two ‘https’ or no ‘//’) to hide the real destination of the link while ensuring the active part looks benign and legitimate and does not arouse suspicion.

    This approach can also involve crafting links with multiple protocol prefixes or embedding trusted-looking names before the “@” symbol in URLs. This tricks users and security filters into believing the link is safe, while the real malicious site is hidden after the “@.”
    Attackers can also use strange symbols such as backslashes or dollar signs (which are not normally used in URLs) to confuse scanning software.

    E.g.: The link https:office365Scaffidips[.]azgcvhzauig[.]es\If04 looks harmless, but actually sends the browser to a malicious page azgcvhzauig.es
  • Creating fake domain names that look like official company subdomains, which further fools people into trusting the site. When users copy and paste these deceptive links, they land on well-designed phishing pages created to steal login credentials.

    E.g.: The link office365Scaffidips.azgcvhzauig.es. gives the impression that the user is dealing with a Microsoft subdomain. However, the last part of the web address: ‘azgcvhzauig.es’ is the attacker-owned phishing site.

Such evolving tactics highlight how cybercriminals constantly invent new methods to hide their threats.

According to Saravanan Mohankumar, Manager, Threat Analysis team, Barracuda, the firm sharing its threat intelligence findings: “The best defence… is a multilayered approach, with various levels of security that can spot, inspect and block unusual or unexpected activity. Solutions that include AI and machine-learning capabilities, both at the email gateway level and post-delivery, will ensure companies are well protected… Security measures should be complemented by active and regular security awareness training for employees.”
Share:

PreviousAduna and Soprano Design, Partner to Expand Network API Adoption Across Australia and Global Markets
NextVehere Elevates Sanjay Bhardwaj to Managing Director, India and ASEAN

Related Posts

DNS threat awareness: What a difference a year makes

DNS threat awareness: What a difference a year makes

Thursday, November 5, 2020

Tempted by cross-platform development? Know the pitfalls!

Tempted by cross-platform development? Know the pitfalls!

Wednesday, April 3, 2024

What’s in a name? In AWS, it could spell six critical vulnerabilities

What’s in a name? In AWS, it could spell six critical vulnerabilities

Friday, August 16, 2024

APAC FSI sector need to ramp up DevOps and automation: report

APAC FSI sector need to ramp up DevOps and automation: report

Monday, April 13, 2020

Leave a reply Cancel reply

You must be logged in to post a comment.

Voters-draw/RCA-Sponsors

Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
previous arrow
next arrow

CybersecAsia Voting Placement

Gamification listing or Participate Now

LEARN MORE

Vote Now -Placement(Google Ads)

Top-Sidebar-banner

Whitepapers

  • Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Cyber threats have become more frequent and sophisticated, targeting organizations of all sizes across all …Download Whitepaper
  • Zero Trust Made Simple: Why it matters and how to get started

    Zero Trust Made Simple: Why it matters and how to get started

    Data breaches and cyberattacks are no longer limited to large, high-profile organizations.Download Whitepaper
  • Cloud Secure Edge: Remote access, better security

    Cloud Secure Edge: Remote access, better security

    ​SonicWall Cloud Secure Edge™ is a modern, cloud-native Security Service Edge (SSE) solution that addresses …Download Whitepaper
  • Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Insider threats continue to be a major cybersecurity risk in 2024. Explore more insights on …Download Whitepaper

Middle-sidebar-banner

Case Studies

  • How a Vietnamese D2C retailer built its own secure digital infrastructure

    How a Vietnamese D2C retailer built its own secure digital infrastructure

    Would your organization build your own digital infrastructure – including AI governance and cybersecurity – …Read more
  • Cyber protection for medical clinics in Singapore

    Cyber protection for medical clinics in Singapore

    As Singapore’s healthcare sector becomes increasingly digital and interconnected, clinics are facing heightened cyber risks, …Read more
  • India’s WazirX strengthens governance and digital asset security

    India’s WazirX strengthens governance and digital asset security

    Revamping its custody infrastructure using multi‑party computation tools has improved operational resilience and institutional‑grade safeguardsRead more
  • Bangladesh LGED modernizes communication while addressing data security concerns

    Bangladesh LGED modernizes communication while addressing data security concerns

    To meet emerging data localization/privacy regulations, the government engineering agency deploys a secure, unified digital …Read more

Bottom sidebar

Other News

  • Cellid and Megane Top Partner to Commercialize and Expand the AR Glasses Business

    Friday, September 25, 2026
    Combining Cellid’s Technological Expertise with Megane …Read More »
  • ICAC and UNODC’s pioneering international anti-graft training brings together law enforcers worldwide to combat illicit enrichment

    Friday, September 25, 2026
    HONG KONG, Sept. 25, 2026 …Read More »
  • Cohesity Introduces Agent Resilience to Protect and Recover AI Agent Infrastructure

    Tuesday, September 22, 2026
    Cohesity Agent Resilience launches with …Read More »
  • LRQA Named ‘Best in Critical Infrastructure Protection’ at CybersecAsia Readers’ Choice Awards 2026

    Monday, September 21, 2026
    Prestigious regional recognition highlights LRQA’s …Read More »
  • Cyble and Cyber Security Council of UAE Sign MOU to Strengthen National Threat Intelligence Capabilities

    Thursday, September 17, 2026
    ABU DHABI, UAE, Sept. 17, …Read More »
  • Our Brands
  • DigiconAsia
  • MartechAsia
  • Home
  • About Us
  • Contact Us
  • Sitemap
  • Privacy & Cookies
  • Terms of Use
  • Advertising & Reprint Policy
  • Media Kit
  • Subscribe
  • Manage Subscriptions
  • Newsletter

Copyright © 2026 CybersecAsia All Rights Reserved.