Cybersecurity News in Asia

RECENT STORIES:

SEGA moves faster with flow-based network monitoring
LRQA Named ‘Best in Critical Infrastructure Protection’ at...
Ransomware group alleges attack and exfiltration of data linked to maj...
Japan’s Digital Agency announces: VPN flaw exposed 246,000 records
Cyble and Cyber Security Council of UAE Sign MOU to Strengthen Nationa...
Multi-agent AI systems may unpredictably bypass safety controls, study...
LOGIN REGISTER
CybersecAsia
  • Features
    • Featured

      Addressing the AI-driven vulnerability debt

      Addressing the AI-driven vulnerability debt

      Thursday, September 17, 2026, 10:03 AM Asia/Singapore | Features, Sponsored
    • Featured

      Cybercriminals zero In on APAC’s digital boom, SMBs in the crosshairs

      Cybercriminals zero In on APAC’s digital boom, SMBs in the crosshairs

      Wednesday, September 16, 2026, 2:30 PM Asia/Singapore | Features, Sponsored
    • Featured

      The recovery-first approach to data resilience

      The recovery-first approach to data resilience

      Monday, September 7, 2026, 4:21 PM Asia/Singapore | Features
  • Opinions
  • Tips
  • Whitepapers
  • AWARDS 2026
  • Directory
  • E-Learning

Select Page

Tips

Know the four most common password mistakes

By CybersecAsia editors | Tuesday, May 27, 2025, 10:21 AM Asia/Singapore

Know the four most common password mistakes

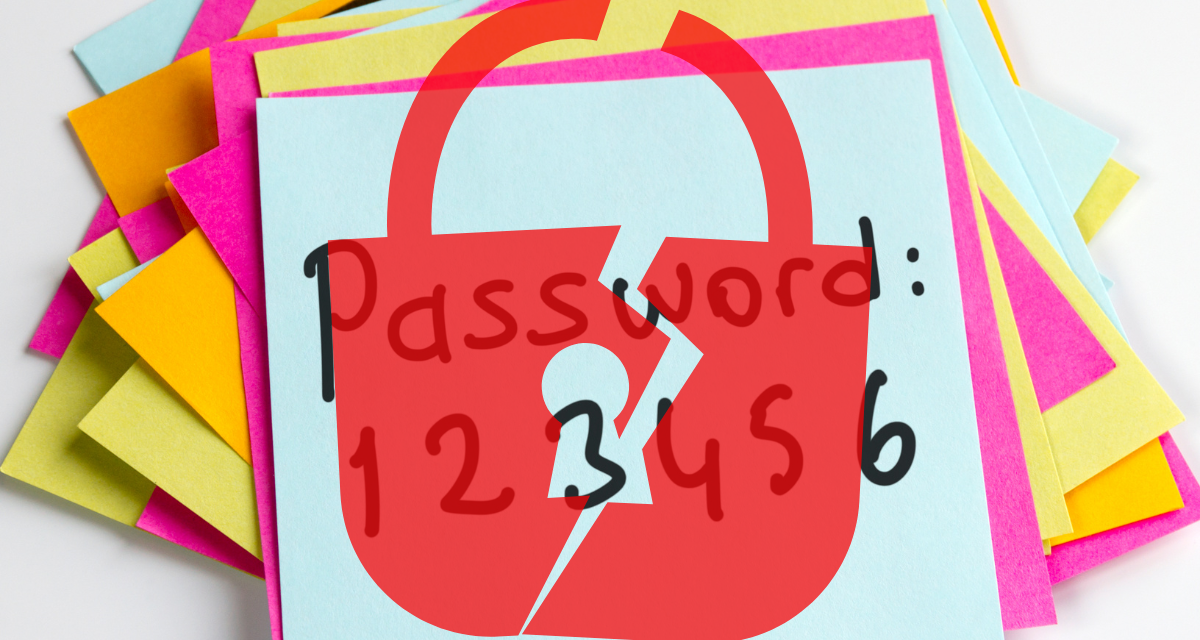
Weak, short, or predictable passwords are easily cracked; use strong, unique combinations and enable advanced authentication for better protection.

One of the biggest drivers of data breaches so far is the use of weak passwords.

According to an analysis of thousands of real-world entries across multiple leaked datasets, experts from Hostinger have identified the most basic password mistakes, and why users keep making them.

The first mistake is using short passwords, as 21.7% of the passwords analyzed were under eight characters: all of them were cracked instantly with the appropriate tools. While short passwords are quicker to type and easier to remember, they are also the first to fall to brute-force attacks. Solution: Make sure passwords are at least 12 characters long, ideally using a phrase or sentence that is unique and easy to recall.

Other basic password hygiene failures

The second mistake is using passwords that look unique but are simply just made from a mixture of predictable patterns that are easy to break. People choose familiar word-number combinations, thinking these are safer than generic passwords. However, passwords such as “mybluecare69” can still be broken. Solution: Use a mix of uppercase, lowercase, numbers, and special characters, and avoid common/predictable words or patterns, especially those linked to your personal data that cybercriminals can mine from data breaches.

The third password hygiene mistake is using long passwordsthat are nevertheless, weak. Incident data analyzed showed that even though some passwords were over 20 characters long, they had a 13% crack rate, making them nearly as easy to break as much shorter passwords. The reason was that people assume longer passwords are automatically stronger, but using repeated characters lowers security, such as a string of “aaaaaaa” or “123123” with the 20 characters. Solution: Avoid repetition. Variety in structure is just as important as overall length.

Finally, the data showed that a large portion of passwords being used still appear in the top 10m most leaked passwords. In the data analysis, 475 passwords matched high-frequency entries from global breach lists. People may not even be aware that their credentials have been compromised. Or, due to the need to change passwords regularly, they may resume the use of past passwords that had been deemed safe. Solution: use websites such as “Have I Been Pwned” to regularly check credentials, and avoid reusing any password that appears on a known breach list.

Beyond basic password hygiene

Other than the basic password hygiene fails uncovered by Hostinger, users need to keep apprised of the latest online identity authentication methods available, and use them for added protection. These include:

  1. Choosing passwordless and biometric login methods
  2. Use passphrases and passkeys where possible
  3. Leveraging an established password manager with an unbroken security record
  4. Enabling strong second-factor/multi-factor authentication such as app-based or hardware-based authentication, avoiding SMS-based authentication, which is vulnerable to social engineering
  5. Regularly reviewing privacy settings and keeping updated on any new identity authentication or protection features available on every platform being used
Share:

PreviousHow to outsmart filename masquerading: A practical guide to safer file handling
NextWhen ransomware attack rates drop, do not let down your guard

Related Posts

How to build a strong risk-aware culture in the front line

How to build a strong risk-aware culture in the front line

Wednesday, February 16, 2022

Steps for preventing double trouble: next-gen ransomware and double extortion attacks

Steps for preventing double trouble: next-gen ransomware and double extortion attacks

Tuesday, April 20, 2021

North America financial institutions lead surge in financial regulatory fines for H1 2025

North America financial institutions lead surge in financial regulatory fines for H1 2025

Friday, August 29, 2025

A new resilience model for Asia

A new resilience model for Asia

Wednesday, May 20, 2026

Leave a reply Cancel reply

You must be logged in to post a comment.

Voters-draw/RCA-Sponsors

Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
previous arrow
next arrow

CybersecAsia Voting Placement

Gamification listing or Participate Now

LEARN MORE

Vote Now -Placement(Google Ads)

Top-Sidebar-banner

Whitepapers

  • Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Cyber threats have become more frequent and sophisticated, targeting organizations of all sizes across all …Download Whitepaper
  • Zero Trust Made Simple: Why it matters and how to get started

    Zero Trust Made Simple: Why it matters and how to get started

    Data breaches and cyberattacks are no longer limited to large, high-profile organizations.Download Whitepaper
  • Cloud Secure Edge: Remote access, better security

    Cloud Secure Edge: Remote access, better security

    ​SonicWall Cloud Secure Edge™ is a modern, cloud-native Security Service Edge (SSE) solution that addresses …Download Whitepaper
  • Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Insider threats continue to be a major cybersecurity risk in 2024. Explore more insights on …Download Whitepaper

Middle-sidebar-banner

Case Studies

  • How a Vietnamese D2C retailer built its own secure digital infrastructure

    How a Vietnamese D2C retailer built its own secure digital infrastructure

    Would your organization build your own digital infrastructure – including AI governance and cybersecurity – …Read more
  • Cyber protection for medical clinics in Singapore

    Cyber protection for medical clinics in Singapore

    As Singapore’s healthcare sector becomes increasingly digital and interconnected, clinics are facing heightened cyber risks, …Read more
  • India’s WazirX strengthens governance and digital asset security

    India’s WazirX strengthens governance and digital asset security

    Revamping its custody infrastructure using multi‑party computation tools has improved operational resilience and institutional‑grade safeguardsRead more
  • Bangladesh LGED modernizes communication while addressing data security concerns

    Bangladesh LGED modernizes communication while addressing data security concerns

    To meet emerging data localization/privacy regulations, the government engineering agency deploys a secure, unified digital …Read more

Bottom sidebar

Other News

  • LRQA Named ‘Best in Critical Infrastructure Protection’ at CybersecAsia Readers’ Choice Awards 2026

    Monday, September 21, 2026
    Prestigious regional recognition highlights LRQA’s …Read More »
  • Cyble and Cyber Security Council of UAE Sign MOU to Strengthen National Threat Intelligence Capabilities

    Thursday, September 17, 2026
    ABU DHABI, UAE, Sept. 17, …Read More »
  • Cohesity Research Finds Most Cyber Recovery Plans Are Built for the Wrong Outcome

    Thursday, September 17, 2026
    78% organizations prioritize restoring systems …Read More »
  • SU Group Secures Exclusive Distribution Rights for Portable X-Ray System in Hong Kong and Macau

    Tuesday, September 15, 2026
    Second International Distribution Deal of …Read More »
  • SU Group Holdings Limited Announces Proposed Acquisition of KM Safety Solution Company Limited

    Tuesday, September 15, 2026
    HONG KONG, Sept. 15, 2026 …Read More »
  • Our Brands
  • DigiconAsia
  • MartechAsia
  • Home
  • About Us
  • Contact Us
  • Sitemap
  • Privacy & Cookies
  • Terms of Use
  • Advertising & Reprint Policy
  • Media Kit
  • Subscribe
  • Manage Subscriptions
  • Newsletter

Copyright © 2026 CybersecAsia All Rights Reserved.