Cybersecurity News in Asia

RECENT STORIES:

SEGA moves faster with flow-based network monitoring
Post Quantum Cryptography readiness in South-east Asia: an update
Advantech Partners with DEKRA, Signing MOU to Strengthen Global Indust...
Hackers cause legacy IoT refrigerators at hundreds of French supermark...
AUTOCRYPT Celebrated As “Automotive Cybersecurity Company of the...
Communications infrastructure – from legacy risk to modern resilience...
LOGIN REGISTER
CybersecAsia
  • Features
    • Featured

      Communications infrastructure – from legacy risk to modern resilience

      Communications infrastructure – from legacy risk to modern resilience

      Thursday, October 15, 2026, 2:08 PM Asia/Singapore | Features
    • Featured

      Advancing OT Cyber Readiness and Resilience in Southeast Asia

      Advancing OT Cyber Readiness and Resilience in Southeast Asia

      Wednesday, October 14, 2026, 10:00 AM Asia/Singapore | Features, News, Sponsored
    • Featured

      How CISOs can set human boundaries for autonomous cybersecurity

      How CISOs can set human boundaries for autonomous cybersecurity

      Wednesday, October 7, 2026, 11:05 AM Asia/Singapore | Features, Newsletter, Tips
  • Opinions
  • Tips
  • Whitepapers
  • AWARDS 2026
  • Directory
  • E-Learning

Select Page

News

Analysis of 17 months of incident data by IT firm yields APAC enterprise ransomware trends

By CybersecAsia editors | Saturday, August 2, 2025, 11:05 PM Asia/Singapore

Analysis of 17 months of incident data by IT firm yields APAC enterprise ransomware trends

Increasing incidents of quadruple extortion, AI abuse, and regulatory challenges were some of the shifts in regional enterprise-customer cybersecurity trends.

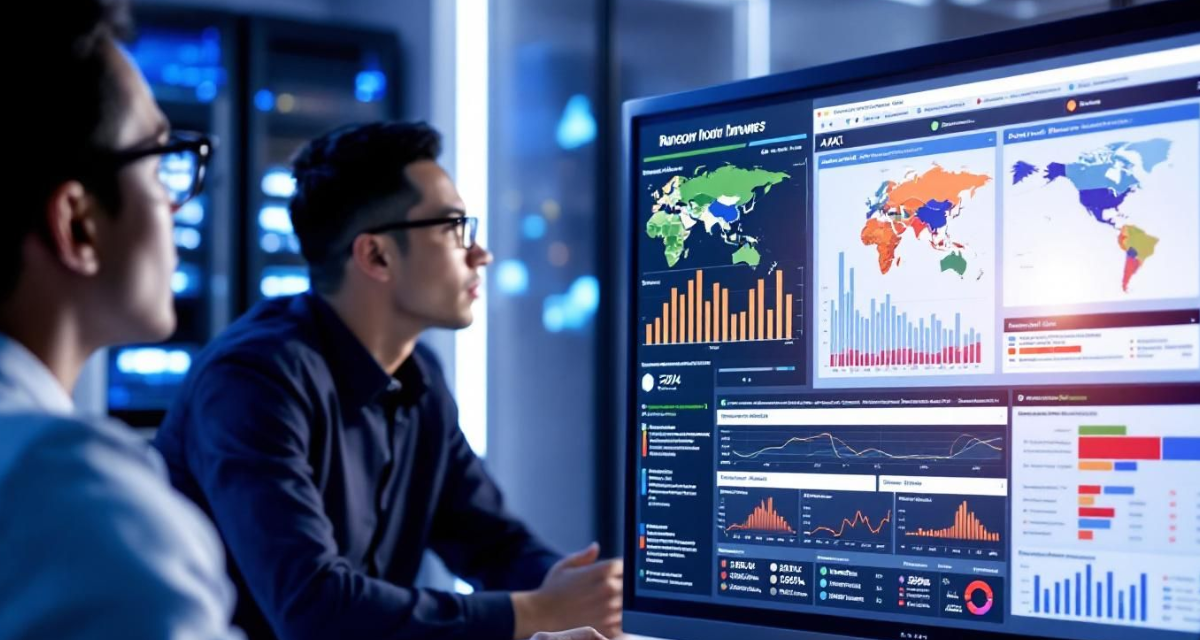
A new technical report released on 30 July 2025 details the evolving nature of ransomware attacks in a cybersecurity and cloud computing firm’s user base in the Asia Pacific region (APAC), emphasizing shifts in extortion techniques, target selection, and regulatory exploitation throughout 2024 and early 2025.

The analysis is based on data from enterprise monitoring and detection of billions of events monthly, covering over 100 ransomware groups, but includes a data outage in April 2025, and omits certain global customer segments, introducing modest data continuity concerns.

Some key technical findings include:

  • There has been a rise in “quadruple extortion” tactics in the 17-month data, with attackers combining data encryption, threats to leak stolen data, distributed denial-of-service (DDoS) disruptions, and targeted pressure through outreach to partners, customers, or the media.
  • Double extortion remained the most common ransomware method observed in the wild.
  • Major ransomware collectives associated with high-impact APAC attacks have targeted customer sectors such as healthcare, legal services, public sector entities, and manufacturing. Recent breaches include the theft of 1.5TB of medical organization data, and a multimillion-dollar legal-sector extortion in Singapore.
  • Newer criminal groups have been exploiting Ransomware-as-a-Service models to extend their reach. These actors have increasingly target small and midsize organizations in the firm’s user base, sometimes leveraging vulnerabilities linked to partners and supply chain vendors.
  • Attackers in the data have been capitalizing on disparate regulatory and compliance frameworks in the region. Enforcement and penalties for breach reporting vary greatly, with India allowing for potential criminal penalties, Japan currently having no formal financial fines, and Singapore imposing fines of up to 10% of annual revenue under certain statutes.
  • Technical advancements in attack methodology during the 17 months have included widespread use of generative AI to:
    • Generate new ransomware code variants
    • Craft more convincing phishing or social engineering content
    • Deploy automated chatbots for victim negotiations
  • Cryptocurrency mining malware incidents continued to harm non-profit and educational institutions users in the user base
  • The Trickbot malware family remained active and dangerous, implicated in cumulative cryptocurrency extortion. Also, there has been increased convergence between criminal ransomware and ideologically motivated hacktivist activity, with groups combining both technical and social-political drivers in their attacks.

In terms of methodology limitations, the analysis is based on detection telemetry across enterprise customers, classifying any communication attempt with a known malicious domain or IP as an event regardless of actual compromise. The report’s scope excludes full global representation and is affected by minor data interruptions (April 2025, due to a “data collection issue”), which may slightly affect trend analysis for certain periods.

According to Reuben Koh, Director of Security Technology and Strategy (Asia-Pacific and Japan), Akamai, the firm sharing its 17-month findings, enterprises “need to re-assess their security posture and double-down in their efforts to be more cyber resilient… with regular recovery drills and incident response simulations… against attacks like ransomware.”
Share:

PreviousData analysis based on cyber insurance-driven, multimodal survey data yields expected cyber trends
NextFescaro bucks industry norms to become Korea’s first full-stack auto cybersecurity provider

Related Posts

Uppsala Security unveils risk assessment tool to strengthen your cyber-defenses

Uppsala Security unveils risk assessment tool to strengthen your cyber-defenses

Monday, October 7, 2019

Hacker steals US2m in crypto via seed phrase trick

Hacker steals US$282m in crypto via seed phrase trick

Wednesday, January 21, 2026

Which cyber defense tech works best to stave off ransomware threats?

Which cyber defense tech works best to stave off ransomware threats?

Thursday, October 14, 2021

Scattered Spider: still spinning phishing webs on corporate land?

Scattered Spider: still spinning phishing webs on corporate land?

Wednesday, May 14, 2025

Leave a reply Cancel reply

You must be logged in to post a comment.

Voters-draw/RCA-Sponsors

Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
Slide
previous arrow
next arrow

CybersecAsia Voting Placement

Gamification listing or Participate Now

LEARN MORE

Vote Now -Placement(Google Ads)

Top-Sidebar-banner

Whitepapers

  • Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Critical Security Threatsand the Need for ZTNA: How evolving cyberattacks demand a Zero Trust approach

    Cyber threats have become more frequent and sophisticated, targeting organizations of all sizes across all …Download Whitepaper
  • Zero Trust Made Simple: Why it matters and how to get started

    Zero Trust Made Simple: Why it matters and how to get started

    Data breaches and cyberattacks are no longer limited to large, high-profile organizations.Download Whitepaper
  • Cloud Secure Edge: Remote access, better security

    Cloud Secure Edge: Remote access, better security

    ​SonicWall Cloud Secure Edge™ is a modern, cloud-native Security Service Edge (SSE) solution that addresses …Download Whitepaper
  • Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Closing the Gap in Email Security:How To Stop The 7 Most SinisterAI-Powered Phishing Threats

    Insider threats continue to be a major cybersecurity risk in 2024. Explore more insights on …Download Whitepaper

Middle-sidebar-banner

Case Studies

  • FOMO Pay expands cross-border compliance infrastructure amid rising fraud risks

    FOMO Pay expands cross-border compliance infrastructure amid rising fraud risks

    To unify onboarding and ongoing reviews the payment firm adds identity, liveness, business-ownership, sanctions screening …Read more
  • How a Vietnamese D2C retailer built its own secure digital infrastructure

    How a Vietnamese D2C retailer built its own secure digital infrastructure

    Would your organization build your own digital infrastructure – including AI governance and cybersecurity – …Read more
  • Cyber protection for medical clinics in Singapore

    Cyber protection for medical clinics in Singapore

    As Singapore’s healthcare sector becomes increasingly digital and interconnected, clinics are facing heightened cyber risks, …Read more
  • India’s WazirX strengthens governance and digital asset security

    India’s WazirX strengthens governance and digital asset security

    Revamping its custody infrastructure using multi‑party computation tools has improved operational resilience and institutional‑grade safeguardsRead more

Bottom sidebar

Other News

  • Advantech Partners with DEKRA, Signing MOU to Strengthen Global Industrial Cybersecurity Compliance in Response to EU CRA

    Friday, October 16, 2026
    TAIPEI, Oct. 16, 2026 /PRNewswire/ …Read More »
  • AUTOCRYPT Celebrated As “Automotive Cybersecurity Company of the Year” In 2026 AutoTech Breakthrough Awards Program

    Thursday, October 15, 2026
    Annual Awards Program Recognizes Breakthrough …Read More »
  • Taoping Receives Nasdaq Notification Regarding Minimum Bid Price Deficiency

    Thursday, October 15, 2026
    TIANJIN, China, Oct. 15, 2026 …Read More »
  • From Defence Cooperation to Shared Security: Building a Resilient Pakistan-China Partnership

    Friday, October 9, 2026
    QINGDAO, China, Oct. 9, 2026 …Read More »
  • CyberDSA Sets 19 – 21 October 2027 Return as Industry Participation Builds at Fourth Edition

    Thursday, October 8, 2026
    CyberDSA moves towards its milestone …Read More »
  • Our Brands
  • DigiconAsia
  • MartechAsia
  • Home
  • About Us
  • Contact Us
  • Sitemap
  • Privacy & Cookies
  • Terms of Use
  • Advertising & Reprint Policy
  • Media Kit
  • Subscribe
  • Manage Subscriptions
  • Newsletter

Copyright © 2026 CybersecAsia All Rights Reserved.